Tag: Government

  • Federal court tosses Trump lawsuit challenging Alaska Senate certification

    A federal judge dismissed a lawsuit from the federal government seeking to preemptively block Democratic Senate candidate Mary Peltola from assuming office if she wins her race.

    The Department of Justice sued Alaska last month, arguing that an alleged scheme by Peltola to recruit Daniel J. Sullivan, an independent candidate who shares a name with incumbent Republican Sen. Dan S. Sullivan, would confuse voters.

    Peltola’s campaign, the Democratic Senate Campaign Committee and civic groups including the League of Women Voters of Alaska and Common Cause all filed motions to dismiss the lawsuit, arguing the federal government lacks standing and constitutional authority to weigh in on Alaska’s elections.

    They also said the court cannot grant relief because there is no legal way to determine whether a voter mistakenly voted for one Sullivan over the other without violating the secret ballot.

    U.S. District Judge Sharon Gleason reached the same conclusion, noting in an order “the absence of any explanation from the United States as to how its requested relief could redress its alleged injury while simultaneously maintaining the secrecy of the ballot.” She also wrote that she “cannot grant the United States the relief it seeks because the United States has failed to establish the redressability prerequisite for Article III standing.”

    Gleason’s opinion recounts Daniel J. Sullivan’s independent candidacy. Alaska Director of Elections Carol Beecher decertified it in June, later testifying that she did not believe he was running in good faith. State courts disagreed and restored his candidacy, and the Alaska Supreme Court upheld that ruling. 

    Alaskan election officials still took steps to distinguish the two candidates, listing their full names and labeling them “Incumbent,” “Republican candidate” and “Independent.” Alaska’s ranked-choice system lets voters rank both Sullivans, so they are not limited to a single candidate.

    State officials and election experts also noted that nearly 60,000 Alaskan voters have already cast early or mail ballots, and there is no feasible way to reissue them.

    The government’s one-sentence response said the state could segregate ballots and asked the court to allow a federal investigation into whether any voters were deceived. Gleason rejected that approach, saying the government offered no explanation of how ballot segregation or a law enforcement inquiry into voters’ intent could be carried out while preserving ballot secrecy.

    Gleason also questioned the government’s constitutional basis, writing that the executive branch has no legitimate role in determining which candidates appear on Alaska’s ballots. The government said it was not seeking to change the time, place or manner of the election, but Gleason noted that its requests, including limits on certification, ballot segregation and an investigation of voters’ intent, all concern those matters, which are the state’s responsibility.

    The lawsuit drew heavy media attention and concern from democracy advocates, but legal experts widely viewed it as exceptionally weak.

    “Today’s ruling marks a victory for Alaska state sovereignty and Alaskan voters,” said David Becker, executive director of the nonprofit Center for Election Innovation and Research and a former voting rights attorney at DOJ. “By soundly rejecting the administration’s unlawful and now unsuccessful attempt to interfere, the court concurred with the State of Alaska that this is purely a matter of state law and that, under the U.S. Constitution, the federal government has no role in determining how Alaska certifies its Senate election.”

    Source: CyberScoop · 2026-11-01
  • China-backed threat group used agentic AI pentesting tool to compromise 140 sensitive targets in 11 days

    A China state-backed threat group is using ARTEX, the automated agentic AI penetration testing framework, to achieve remarkable speed, scale and success in a campaign that already compromised about 140 sensitive targets in 11 days, according to CrowdStrike. 

    The threat group, which CrowdStrike tracks as Vapor Panda, targeted more than 200 organizations in at least 14 countries since Oct. 17, the security company said in a threat report Thursday. Targets and confirmed victims include foreign ministries, a European country’s presidency and prime minister’s office, defense and intelligence agencies; 19 U.S.-based organizations in the pharmaceutical, semiconductor, defense, nuclear and financial sectors; and telecom providers in the United States, Belgium and the Philippines. 

    CrowdStrike told CyberScoop about 70% of Vapor Panda’s targets were confirmed compromised or had evidence indicating moderate confidence of a successful intrusion. 

    Vapor Panda’s use of ARTEX, paired with DeepSeek, allowed it to accomplish more tasks with shocking speed — requests occurring as often as every 10 seconds — and pursue multiple attack paths concurrently. 

    “This is the first time that we’re seeing an agentic adversary nation-state threat actor at this scale, and I think that this is probably, unfortunately, something we’ll see more of,” Adam Meyers, senior vice president of counter adversary operations at CrowdStrike, told CyberScoop.

    Hands-on-keyboard activity tracked by CrowdStrike for the past 15 years typically involved up to 40 commands per hour. “Now, with ARTEX, we could see it exceed 1,500 commands an hour,” Meyers said.

    “If you diversify that across 200 targets, it costs them very little to run a mass-exploitation campaign and drop a websell,” he added. “They can hit more targets in a faster period of time.”

    Vapor Panda’s broad-access campaign, which remains active, has targeted think tanks and government agencies spanning defense, justice, finance and diplomacy.

    “I would characterize it as a diverse operational mission that tends to focus on sectors and geographies that Beijing considers economically or politically important,” Meyers said.

    The active campaign attributed to Vapor Panda is separate from the ARTEX activity Microsoft Threat Intelligence attributed to Storm-0940 earlier this month, including a supply-chain attack targeting ConnectWise customers. 

    Adversarial use of AI is relatively new, yet also quickly becoming the new normal, Meyers said. “We’re scrambling because we’re seeing so many of these agentic adversaries.”

    Agentic AI use for malicious purposes is growing month-over-month at a rate of almost threefold. CrowdStrike observed roughly 45 agentic adversary attacks in September and it’s already at 126 for October, and climbing.

    Adversarial use of agentic AI isn’t an intractable problem, but rather another reminder that organizations need visibility into their endpoints, identities and cross-domain capabilities, Meyers said. 

    These attacks aren’t showcasing anything new, “it’s just doing it at a speed and scale that we’re unaccustomed to,” he said. “It’s not hopeless, but you’ve got to take action. You can’t put your head in the sand.”

    Source: CyberScoop · 2026-10-30

  • DOJ raises privacy concerns over potential sale of Character.AI chats

    DOJ raises privacy concerns over potential sale of Character.AI chats

    The DOJ’s Executive Office for U.S. Trustees said a consumer privacy ombudsman is needed to advise the court on how to regulate what data from Character.AI can be sold and under what terms.

    Source: The Record · 2026-10-30

  • Florida warns that 4.9 million people had Social Security numbers leaked in financial aid site breach

    Florida warns that 4.9 million people had Social Security numbers leaked in financial aid site breach

    The state’s Department of Education (FLDOE) said on Thursday it became aware of a data breach involving the Florida Student Financial Aid website on October 19.

    Source: The Record · 2026-10-30

  • Defense contractor pleads guilty to aiding North Korean remote worker scheme

    A defense contractor with top secret security clearance pleaded guilty to aiding North Korea’s remote worker scheme by allowing co-conspirators to use his identity to apply for jobs, including positions with national security implications, the Justice Department said Wednesday. 

    John Allen Kurrle Jr. participated in a short-lived but prolific conspiracy that spanned at least 88 job applications at U.S.-based companies, resulting in nine job offers, according to court records.

    The 62-year-old allowed co-conspirators to use his identity and government clearance for prospective sensitive work, often with U.S. government contractors. The nine job offers Kurrle’s co-conspirators received between June and October 2025 had annual salary ranges of $120,000 to $190,000.

    The scheme had a limited success rate. The longest and most lucrative job a co-conspirator landed under Kurrle’s identity lasted about three weeks, netting a total pay of $4,800.

    His identity was also used to gain employment as a software engineer at a Ventura, California-based company to work on a generative AI project for a component of the U.S. military. The company sent a laptop to Kurrle’s residence in Gainesville, Virginia, where he received and hosted laptops shipped by multiple victim companies, enabling co-conspirators to remotely access the devices from outside the United States.

    Yet, during a video call to verify employment eligibility, the company noticed that the person who appeared on the video call did not match Kurrle’s age or physical characteristics, according to court records. The unnamed company terminated the employment of Kurrle’s co-conspirator before he did any work on the military contract and Kurrle shipped the laptop back to the company. 

    The company paid Kurrle’s co-conspirator almost $2,200 for 32 hours of onboarding, which Kurrle is now ordered to pay in restitution along with the $4,800 received from the other company. 

    Kurrle also, as part of his plea agreement, admitted to using the identity of a third person, without their consent, to apply for some remote work positions. He doesn’t dispute that the scheme likely benefitted North Korea, but claims he wasn’t aware of the connections to North Korea during the duration of his involvement in the conspiracy.

    Michael Barnhart, nation state investigator at DTEX, said researchers previously identified Kurrle as a facilitator for North Korea’s remote worker scheme. Yet, until recently, he wasn’t sure if Kurrle was a victim or impersonated. 

    The case underscores North Korea’s efforts to gain access to roles with a strategic intelligence requirement, as it focuses on contractor roles because those present the path of least resistance.

    Kurrle joins a growing list of people who have been charged or jailed for supporting the North Korea regime’s scheme that generates hundreds of millions of dollars annually for the country’s military and organizations involved in its weapons programs.

    Authorities have been cracking down on the malicious insider activity by seizing cryptocurrency linked to the theft, and targeting U.S.-based facilitators who provided forged or stolen identities and hosted laptop farms for North Korean operatives. 

    Some of that money is also funneling through a web of front companies and intermediaries, including sanctioned entities, that partly fund Russia’s war effort against Ukraine, DTEX said in a report in July. This includes manufacturing weapons and supplying them to Russia’s military, according to the security firm.

    The countermeasures are stacking up, but the scheme is widespread and has infiltrated an undetermined number of businesses, including hundreds of Fortune 500 companies.

    Federal judges previously sentenced other people to prison for their involvement in the scheme, including Matthew Issac Knoot and Erick Ntekereze Prince; Keija Wang and Zhenxing Wang; Audricus Phagnasay, Jason Salazar and Alexander Paul Travis; Oleksandr Didenko and Christina Chapman. 

    Kurrle pleaded guilty to conspiracy to commit wire fraud and faces up to 20 years in prison upon sentencing, which is currently scheduled for Jan. 28, 2027.

    Source: CyberScoop · 2026-10-30

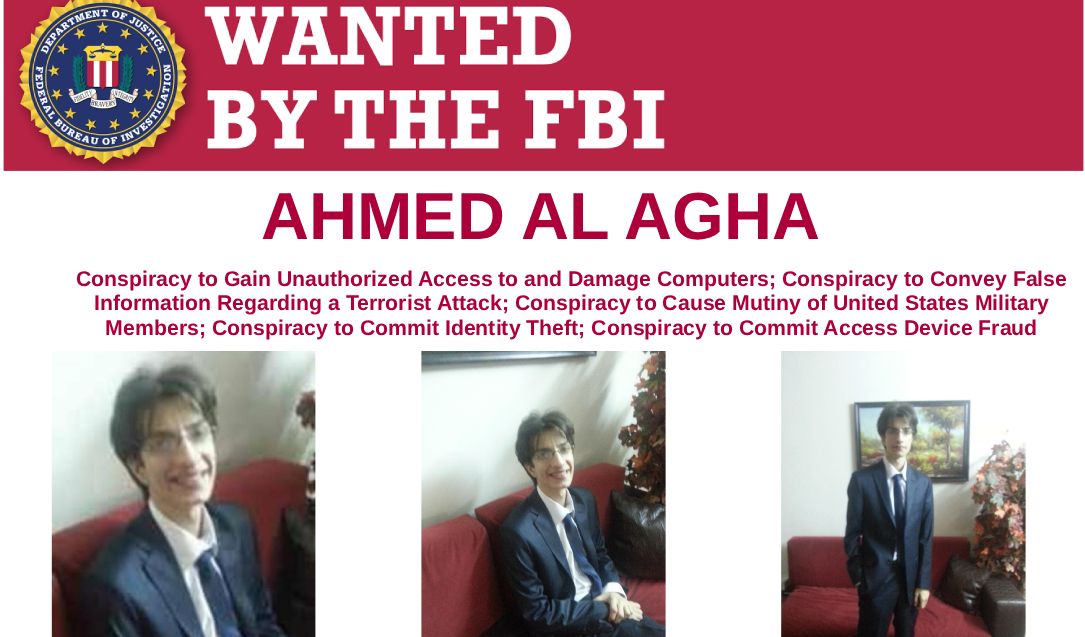
  • Syrian Electronic Army hacker gets prison time for attacks on Western targets

    Syrian Electronic Army hacker gets prison time for attacks on Western targets

    Ahmad Umar Agha, known online as “Th3Pr0,” was sentenced Thursday in federal court in Virginia to 42 months behind bars for his role in a conspiracy that was organized by former Syrian President Bashar al-Assad’s closest advisers.

    Source: The Record · 2026-10-30

  • British spy agency cannot account for thousands of data storage devices, watchdog says

    British spy agency cannot account for thousands of data storage devices, watchdog says

    The Investigatory Powers Commissioner’s Office (IPCO) in its annual report for 2025, published Thursday, said it was “very concerned” and “disappointed with the time it has taken GCHQ to investigate” the issue.

    Source: The Record · 2026-10-30

  • Leaked DHS employee archive, Icepick, faces challenges to stay online

    A company working on behalf of the Department of Homeland Security sought to cut off online access to information on more than 41,000 employees that hacktivists said they obtained from a database breached at DHS.

    A search tool for the database, named Icepick, went offline for a spell before coming online again Thursday under a different registrar.

    Icelandic hosting company FlokiNET said Thursday that it received a request from DHS contractor ZeroFox to remove the data, which it refused.

    “By mid-morning, icepi.cx no longer resolved. Its registrar, CentralNic, had placed the domain on serverHold,” FlokiNET said in a blog post. “Our refusal kept nothing online. The request that decided the outcome to take the site down was not the one sent to us. A registrar reached the opposite conclusion the same morning, published nothing, and a global audience lost access to the site. In the meantime the site is online again under a domain from a different registrar.”

    CentralNic and ZeroFox did not immediately respond to requests for comment Thursday.

    DHS said late Wednesday that it was working to protect its employees against any breach.

    “DHS is aware of a potential breach and is actively working to address the situation swiftly and effectively,” a spokesperson said. “We take all security threats against our employees and officers seriously and will work to ensure all are properly protected. We will update the public when more information is available.”

    The social media site Bluesky was also blocking links to the archive because it shared people’s contact information without their permission, although a company official said changes were coming because the wording had identified it as a malicious link.

    FlokiNET said it refused the ZeroFox request that mislabeled the archive as part of a doxxing campaign.

    “Doxxing publishes private details about private people so that others can find them at home. Icepick publishes work identities of government employees,” it wrote. “Who they work for. What their role is. How they can be reached in that role. The information describes people in the exercise of public authority, not in their private lives. Federal officers carrying out an enforcement programme are not private individuals while they are carrying it out.”

    “The public has a legitimate interest in knowing who is doing that work, under whose authority, and in which office,” it continued. “Journalists cannot report on an agency whose personnel are structurally unknowable.”

    ZeroFox said that regardless of that, the data made it possible to locate people whose information was in the database.

    “The request does not depend on who the listed individuals are or what their duties are,” ZeroFox wrote to FlokiNET. “It rests on two facts: the data was stolen, and it is personal data that identifies and locates real people.”

    Source: CyberScoop · 2026-10-29

  • Leak site publishes data on more than 41,000 DHS employees obtained by hacktivists

    A leak website was published Wednesday, showcasing internal data on more than 41,000 Department of Homeland Security employees and contractors after it was obtained by hackers who claimed to have breached an identity service used by the agency.  

    The transparency nonprofit Distributed Denial of Secrets and the hacker maia arson crimew got the data from a hacktivist outfit known as the Department of Peace.

    ”The leak is extraordinary but deceptive in [its] simplicity as it identifies the officials responsible for overseeing covert and undercover operations, the government’s hunt for leakers and the failed BlueLeaks investigation — along with key personnel in DHS’s ever-escalating rendition and deportation programs,” said Emma Best, founder of DDoSecrets.

    CyberScoop was able to verify numerous current Cybersecurity and Infrastructure Agency employees are listed in the data, along with some former leadership members who left the agency years ago.

    The data goes back years, with various group names listed in the database making reference to COVID-19 planning and internal summits in 2023.

    As of Thursday morning, the website hosting a searchable form of the data has been taken offline.

    The hacktivists said the breach was a response to the promise of stepped-up operations from Immigrations and Customs Enforcement by DHS Secretary Markwayne Mullin.

    ”On July 17th, Markwayne Mullin said he was ’turning up the heat.’ This is what happens to ICE when you do that,” said a spokesperson for the Department of Peace.

    The spokesperson said they obtained the database from an Okta single sign-on service used at DHS. Okta said it was aware of the report.

    “Okta is secure, and we have no evidence our data or systems were compromised,” an Okta spokesperson said.

    DHS did not immediately respond to a request for comment.

    ”This dataset is massive in terms of both size and impact,” said crimew, a Swiss hacker and journalist who has been indicted in the United States over past leaks and who created a search tool for the DHS data. “It provides an unprecedented look into the Department of Homeland Security’s organizational structure, highlighting which people do what work across multiple DHS agencies, including ICE.”

    One researcher said the leak could prove valuable for Freedom of Information Act requests.

    “Email addresses and phone numbers are indispensable tools for FOIA researchers, often making the difference between a vague records request that gets stonewalled and one that gets results,” Ryan Shapiro, executive director of Property of the People, said. “Given the Trump administration’s contempt for even basic transparency, the need for such tools is urgent.”

    DHS has suffered notable breaches before, dating back to a 2014 breach that may have exposed the data of 390,000 then-current and former Homeland Security Department employees, job applicants and contractors. In 2018, DHS notified nearly 250,000 people of a breach at the department.

    Earlier this year, Security firm GitGuardian said it discovered a public GitHub repository that exposed credentials for privileged AWS GovCloud accounts and internal CISA systems dating back to November 2025.

    Greg Otto contributed to this story.

    UPDATE: 10/29/2026, 9:30 a.m.: This story has been updated with details about the web-based database being taken offline.

    Source: CyberScoop · 2026-10-28