A US court sentenced Syrian hacker Ahmad Umar Agha to 42 months for pro-Assad attacks on media, businesses, and government entities.
Source: SecurityWeek · 2026-10-31
A US court sentenced Syrian hacker Ahmad Umar Agha to 42 months for pro-Assad attacks on media, businesses, and government entities.
Source: SecurityWeek · 2026-10-31
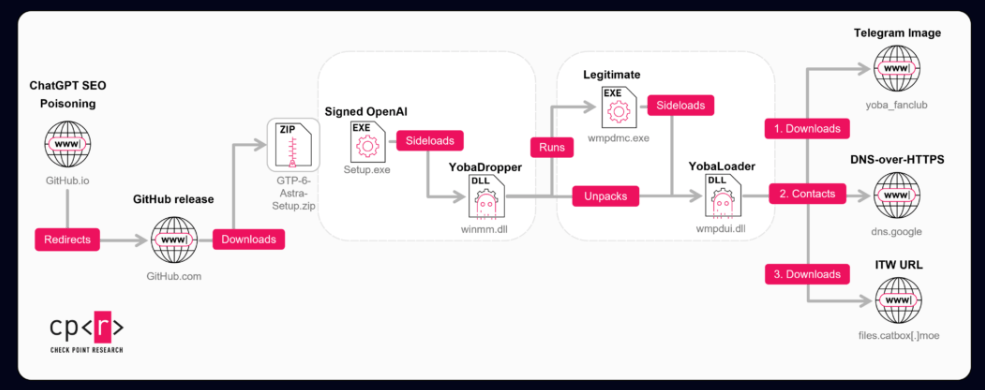
Check Point Research has spent two months tracking a campaign it calls Yoba, which uses the popularity of AI tools to spread a custom malware chain. The attackers build fake GitHub projects that pose as AI desktop applications such as GPT-5.6 Sol, GPT-6 Astra and Claude Opus. The projects look convincing and run on real GitHub infrastructure, which helps them seem legitimate to potential victims.
“These projects look convincing and use real GitHub infrastructure, which helps them appear legitimate to potential victims. The website exhibits search-targeted content and suspicious installer-delivery tactics consistent with an SEO-poisoning lure.
Inside the installers, there is a malicious component we refer to as the YobaDropper. This dropper includes another component, the YobaLoader, which is responsible for contacting attacker-controlled infrastructure and fetching the final payload.” reads the report. “In this report, we describe how victims are lured to these fake projects, how the YobaDropper and YobaLoader work together, and how the attackers ultimately use this chain to run unwanted software on infected systems.”
The lure is simple. Each project has a repository, a GitHub.io page describing the software, and a ZIP release with the malware. The repositories show no fake stars or forks, yet they still rank among the top Google results, most likely through SEO poisoning that optimizes titles, descriptions and hosting domains.
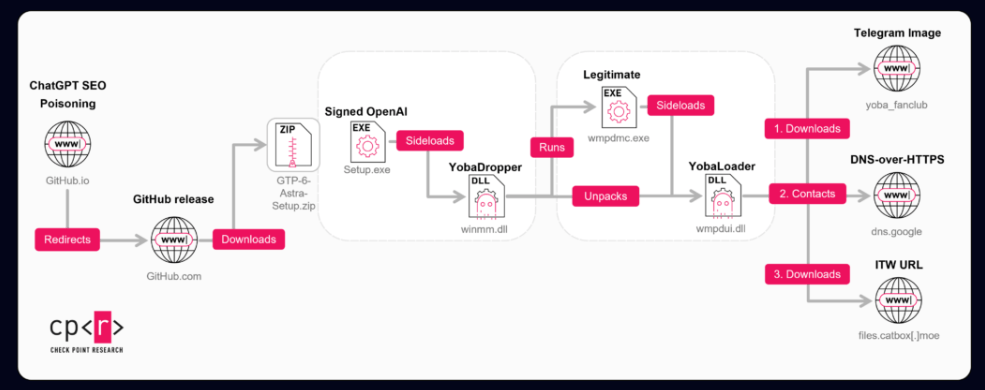
The first repository appeared around July 2026, but the first malicious releases landed only on August 30 and 31, and a third followed about five days later on September 4. Each repository uses a different Outlook address, and commit times point to UTC+4, UTC-4 and UTC+3, which Check Point reads as a deliberate attempt to hide the actor’s real time zone.
Here’s the trick that gives the report its title. Each ZIP holds a legitimate signed executable from OpenAI or Anthropic, named Setup.exe, next to a malicious winmm.dll. The signed program loads the DLL on its own, a technique known as DLL sideloading, which is often used to bypass security protections.
The ZIP files were not even password-protected. Attackers often use passwords to prevent security tools from automatically unpacking and scanning files. However, these binaries already had very low detection rates because they used anti-sandbox and other techniques to avoid analysis. The DLL’s compilation date is another clue: it was built on the same day it was added to the archive, unlike the legitimate files around it.
The dropper, called YobaDropper, checks the environment before running. It calculates a hash of the name of the program that launched it and continues only if the name is Setup.exe. This means that sandboxes that run the DLL on its own will fail this check. When that happens, the process does not exit. Instead, it sleeps 200,000 times for 5.5 seconds each, a total of about 12.73 days.
The malware also avoids victims in CIS countries by checking the keyboard layout. It excludes Russian, Belarusian, Tajik, Armenian, Azerbaijani, Georgian, Kazakh, Kyrgyz, Turkmen, Uzbek, and Tatar. Interestingly, Ukraine, which has often appeared in similar exclusion lists, is not included.
Next, the malware requests administrator privileges. If the user does not have them, it displays the message “Please run this program as Administrator.” and exits. The victim must then restart it with administrator rights.
Once it has the required privileges, the malware creates a folder called WMProcess under ProgramData. It copies the legitimate WMPDMC.exe file from System32 into this folder and places the second-stage payload there under the name wmpdui.dll.
The malicious code achieves persistence by using a scheduled task dressed up as Microsoft. The author is set to Microsoft Corporation, the description says it collects device metadata for Windows Media Player, and it starts three minutes after boot as Local System. The task launches the legitimate program, which sideloads the malicious DLL.
The second stage, YobaLoader, shares code with the dropper, which points to the same developer. It only runs under WMPDMC.exe and uses a different seed for its hashing than the dropper does, which separates the stages and weakens hash-based detection. Its job is to find its payload without a classic command server.
It goes to a Telegram channel, t[.]me/yoba_fanclub, and downloads the channel’s profile picture. The last 50 bytes of the image seed a domain generator that builds names from word lists in the form adjective-noun-verb-number on dedyn[.]io. Change the picture and the operator gets a new domain.
Then it asks Google’s DNS-over-HTTPS service for a TXT record on that domain. The reply is signed, and the loader checks the signature before decrypting it, which gives a link to a payload on Catbox. Check Point says this reliance on DoH and common hosting aims to bypass passive DNS monitoring and some gateway protections, and the campaign avoids dedicated command-and-control infrastructure, using Telegram, Tor, Catbox and DoH instead.
The operator can choose how the payload runs. It can inject it into svchost.exe, save it as an executable after removing the Zone.Identifier mark, or run it as a hidden PowerShell script while bypassing execution policies.
“Finally, the injected payload into svchost.exe is an XMRig 6.26.0 miner with a hidden command line targeting a TLS-enabled onion mining endpoint through a local Tor SOCKS5 proxy. It can unpack and start Tor 0.4.9.12 plus lyrebird 0.8.1, monitor user-input activity to pause mining, and conditionally load the WinRing0 driver service for MSR-based mining optimization.” continnues the report.
The miner uses Tor to connect to an encrypted mining server. It can start its own Tor components, use about 85% of CPU threads, and pause mining when the user is active. It resumes after 240 seconds of inactivity and can load the WinRing0 driver to optimize mining performance.
However, YobaLoader is not limited to cryptocurrency mining. Its DNS tasking system allows operators to deliver any PE executable or PowerShell payload, meaning future attacks could distribute other malware families.
Earlier versions appeared in June 2026. They used Cursor.exe for sideloading, a startup shortcut for persistence, and excluded only Russia. They also used .aber[.]ir instead of dedyn[.]io and included anti-debugging and anti-VM checks that later versions dropped.
Check Point believes the attackers may have Russian origins and mainly operate in the UTC-4 time zone, but this is an assessment, not a confirmed attribution.
Defenders should look for suspicious WMPDMC.exe copies under ProgramData, fake Microsoft scheduled tasks, Telegram-related traffic, DNS lookups for dedyn[.]io through dns.google, and unexplained high CPU usage.
“The Yoba campaign shows how attackers can use trusted platforms and the current interest in AI tools to distribute malware in a way that looks believable and harmless at first glance. By packaging their code together with well-known software names and hosting it on GitHub, they lower the chances that users or basic security checks will immediately flag the files as suspicious.” concludes the report. “Organizations should be cautious about installing “AI helpers” or similar tools from unverified repositories and should enforce policies that restrict running software from unknown sources. Combining user awareness with basic technical controls.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Yoba malware)
Source: Security Affairs · 2026-10-30
The company, billing itself as “the next-generation fashion retailer for Millennial and Generation Z consumers,” said a recent hack exposed customer payment card numbers.
Source: The Record · 2026-10-30
Binance was investigating suspicious transfers that early estimates put at up to $5.8 billion. A day later, multiple media outlets reported that the largest cryptocurrency exchange had linked the theft of about $6.3 billion to a DevOps engineer’s compromised laptop. Billions had moved out of wallets linked to the exchange.
According to The Block, blockchain analyst Spreek identified approximately $3.55 billion in incoming transfers to an initially unidentified wallet.
“Onchain data flagged by analyst Spreek shows about $3.55 billion in incoming transfers to the unlabeled wallet, with nearly $900 million subsequently moved across other wallets.” The Block reports. “Conor Grogan, a senior director and product leader at Coinbase, says the amount is up to $5.8 billion.”
Coinbase executive Conor Grogan initially estimated that the total value of the movements could reach $5.8 billion.
Those figures came from blockchain tracking and differing estimates, so they didn’t necessarily show the amount stolen.
Binance pointed out that customer funds were safe, while co-founder Changpeng Zhao, widely known as CZ, said the activity appeared to be a hack. Zhao no longer manages Binance’s platform, but said he expected customers’ funds to be fully covered.
The company said its user funds were “completely safe.”
“Our teams are aware of reports of a potential security issue and are actively investigating. User funds are completely safe. Our security teams are reviewing all relevant information with urgency, and we will provide updates through official Binance channels as soon as we have verified information.” the company states. “Users should remain cautious of scams and should not trust unofficial links, messages, or requests for account information.”
That assurance is important, but it doesn’t replace a technical explanation of how the transfers occurred or independent confirmation of the final impact.
“Our initial investigation suggests this security incident may have started with a compromised DevOps engineer’s laptop. That gave an attacker access to a service container, where they submitted unauthorized withdrawal transactions.” Binance Co-CEO Richard Teng explained.
“To be clear: the attacker did not simply use one engineer’s permissions, and this was not a single “one-click” action. It involved a more complex attack process. Our investigation has not attributed responsibility to any individual.”
Attackers used access from an engineer’s laptop to reach a service container and send unauthorized withdrawal requests. Binance says it has found no evidence that attackers stole any wallet private keys.
Binance also said it had found “additional points of breach” and was still investigating. Co-CEO Richard Teng said the investigation had not identified anyone responsible. After the attack, Binance suspended deposits and withdrawals to carry out security checks, cancelled the permissions linked to the affected address, and began working with blockchain analysis firms and law enforcement to track the stolen funds.
Binance says it will cover all losses using its SAFU fund and its own money, and that customer funds are safe. The company also plans to publish an updated Proof of Reserves once it has completed the recovery work. This commitment does not replace a detailed technical explanation or independent confirmation of the full impact of the attack.
Binance hasn’t named a culprit, but the blockchain analysis firm TRM has. It attributes the attack to TraderTraitor, a North Korean state-backed unit also tracked as Lazarus Group and APT38, and Chainalysis says it’s highly confident in that finding.
TRM says the attacker moved about $6.36 billion out of Binance wallets on ten blockchains on October 29, most of it in roughly 20 minutes starting at 20:05 UTC. That makes it the largest crypto theft on record, about four times the $1.5 billion Bybit hack of February 2025.
“On October 29, 2026, an attacker moved approximately USD 6.36 billion out of Binance wallets on ten blockchains, most of it in about 20 minutes starting at 20:05 UTC. That makes this the largest crypto theft on record, about four times the USD 1.5 billion Bybit hack of February 2025. Binance has confirmed a security incident and suspended withdrawals on several networks.” TRM said. “TRM attributes the attack to TraderTraitor, North Korea’s elite hacking unit, based on robust on and off-chain intelligence. We make this judgment with high confidence. TRM is tracking the funds and alerting partners through the Beacon Network.”
Freezing the money only went partway. Tether, Circle, Ripple and World Liberty Financial froze about $2.67 billion in stablecoins, and Arbitrum’s Security Council froze 8,426 ETH and 74.6 million ARB, for roughly $2.7 billion in all. But the attacker raced the freezes by selling USDT to market makers and borrowing ETH against USDT on Aave. It now holds more than 420,000 ETH and 18,270 BTC, about $2.4 billion beyond any issuer’s reach.
The early freeze numbers were messy too, Tether and Circle froze approximately $1.79 billion in stablecoins associated with the suspicious transfers in the initial reports. Those amounts describe different moments, and you shouldn’t add them without checking whether they cover distinct assets. A freeze works on tokens that have an issuer to call, and Ether and Bitcoin don’t.
Hot wallets help explain how this type of theft can happen. They store cryptocurrency in systems connected to the internet, allowing exchanges to process withdrawals quickly. But this also makes strong security controls essential. Investigators still need to determine who initiated the transfers, whether they were authorized, whether attackers gained control of the wallets, and whose funds were stolen.
Binance co-founder Changpeng Zhao, who no longer runs the company, said the activity looked like a hack and expected customers to be fully compensated. Large transfers alone do not prove a cyberattack, but the findings that emerged later provided strong evidence of a breach.
Customers also need to be careful. Attackers often exploit the confusion after a major incident by spreading fake announcements, pretending to be support staff, and directing users to fraudulent websites. Use only Binance’s official channels, avoid unexpected links, and never share passwords, authentication codes, or wallet recovery phrases in response to unsolicited messages. Security teams should also watch for phishing emails that use the incident to pressure employees into verifying their accounts.
The lesson goes beyond Binance. A public blockchain records every transaction, but it cannot show who authorized it or how attackers gained access. Blockchain transparency does not guarantee operational security.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Binance)
Source: Security Affairs · 2026-10-30
The state’s Department of Education (FLDOE) said on Thursday it became aware of a data breach involving the Florida Student Financial Aid website on October 19.
Source: The Record · 2026-10-30
A Syrian man who prosecutors say was a central figure in a hacking operation run from former President Bashar Assad’s inner circle was sentenced Thursday to 42 months in federal prison.
Ahmad Umar Agha, 42, carried out the conspiracy from as early as Aug. 24, 2011, until Jan. 31, 2024, according to the Justice Department. The operation was organized and led by members of Assad’s circle, including the commander of Syria’s General Intelligence Directorate.
Agha hacked approximately 47 media entities, businesses, nongovernmental organizations and U.S. and allied government bodies, prosecutors said. The motives included punishing news organizations for reporting on Syrian government atrocities during the Arab Spring and the civil war that followed, spreading fear and confusion among the regime’s opponents, collecting intelligence and trying to persuade members of the U.S. military to refuse their orders.
“Agha deployed his hacking skills in the service of Assad’s regime to silence reporting on the regime’s atrocities, intimidate its opponents, and incite U.S. servicemembers to refuse their orders,” said Assistant Attorney General for National Security John A. Eisenberg.
The most damaging intrusion came April 23, 2013. Prosecutors said Agha accessed the Twitter account belonging to the Associated Press to post a false claim that President Barack Obama had been injured in two explosions at the White House. The post triggered a flash crash, briefly erasing $136 billion in value from the stock market.
In another intrusion, Agha, who used the hacker handle, “Th3 Pr0,” compromised the company hosting the U.S. Marine Corps’ recruitment website and redirected about 3,500 visitors to an image urging Marines to refuse their orders and fight alongside the Syrian Army. On two occasions, he stole usernames and passwords for White House staff email accounts in attempts to take control of the White House’s social media accounts. In one instance he succeeded, prosecutors said.
The costs to victims were significant. One company that works with online publishers lost about $35,000 a day for roughly six months. A global nongovernmental organization spent about $250,000 on new network monitoring products, retrained more than 800 staff members and suffered $480,000 in total losses.
“This case emphasizes the grave threat posed by cyber criminals and especially those serving regimes hostile to the United States,” said First Assistant U.S. Attorney Theophani K. Stamos for the Eastern District of Virginia.
Agha and coconspirator Firas Dardar were first charged by criminal complaint June 12, 2014, and indicted May 17, 2018. Dardar remains a fugitive. He was also charged in 2015 in a separate conspiracy alongside Peter Romar, a Syrian national then living in Germany, that involved computer intrusion, extortion, money laundering and violations of the Syrian Sanctions Regulations. Romar was extradited from Germany and pleaded guilty in 2016.
Assad’s regime collapsed in December 2024, and the former president fled the country.
Source: CyberScoop · 2026-10-30
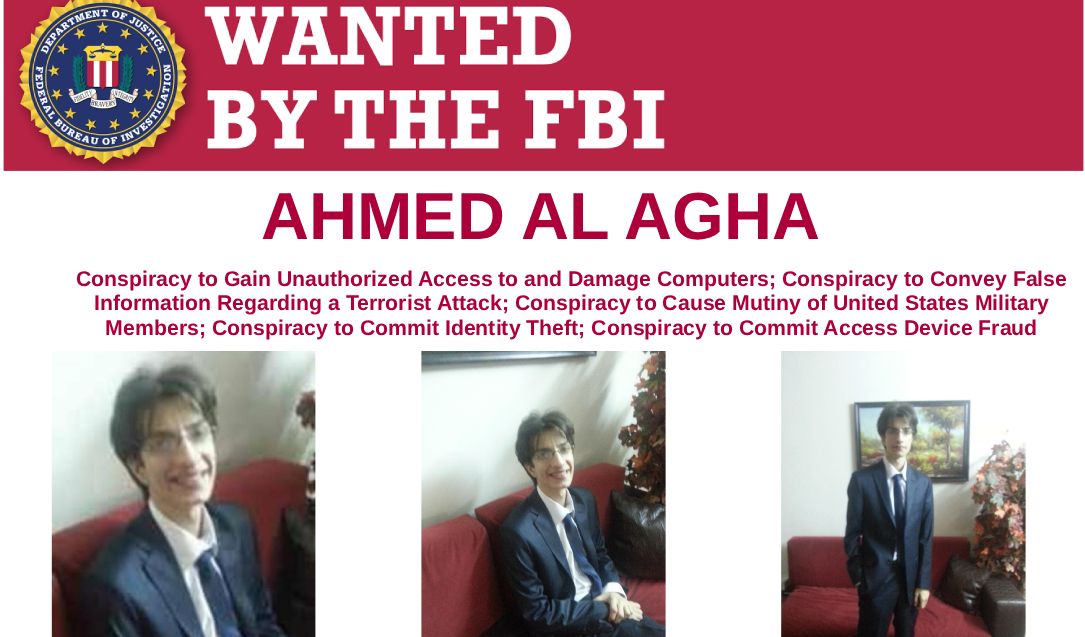
Ahmad Umar Agha, known online as “Th3Pr0,” was sentenced Thursday in federal court in Virginia to 42 months behind bars for his role in a conspiracy that was organized by former Syrian President Bashar al-Assad’s closest advisers.
Source: The Record · 2026-10-30
It allowed customers to host hack-for-hire services, supported ransomware and infostealer operators, and accepted crypto payments.
Source: SecurityWeek · 2026-10-30
A tampered build of Anthropic’s Claude Code extension for VS Code-compatible editors planted an SSH backdoor on developers’ machines, researchers at macOS security firm Phorion have found. The company spotted the malicious package, version 2.1.313, on Open VSX, an open-source marketplace for VS Code extensions run by the Eclipse Foundation. VS Code’s default extension store is Microsoft’s Visual Studio Marketplace, where no malicious version has been reported. Its terms of use limit it to Microsoft’s … More
Source: Help Net Security · 2026-10-30
Malicious code linked to a website monitoring tool was designed to hijack logged-in Polymarket sessions and siphon user funds.
Source: SecurityWeek · 2026-10-30