ARCHIVE
cyber espionage
-
Russian hackers target iOS and Android users with n-day exploits
Russia’s APT29 has been using compromised websites, lookalike domains and a hijacked web analytics service to target iOS and Android users with exploits for patched flaws and steal their cookies,…
SRC // Help Net Security -
AI agents scale and speed up Chinese-linked attacks
A China-nexus espionage group used AI agents to attack more than 200 organizations in 11 days, CrowdStrike said last week. On Monday, Kaspersky published details of a separate campaign against…
SRC // Help Net Security -
Unit 42 Threat Intelligence Highlights – Nov. 2, 2026
Unit 42 details recent threat intelligence, highlighting cyberespionage, financial extortion, and the rapid adoption of AI across offensive workflows. The post Unit 42 Threat Intelligence Highlights - Nov. 2, 2026…
SRC // Palo Alto Networks Unit 42 -
CyberStrikeAI in the wild: the use of AI in real-world attacks on organizations
We analyze a series of attacks on educational institutions that were fully automated during the post-exploitation phase using the CyberStrikeAI penetration testing framework.
SRC // Securelist (Kaspersky GReAT) -
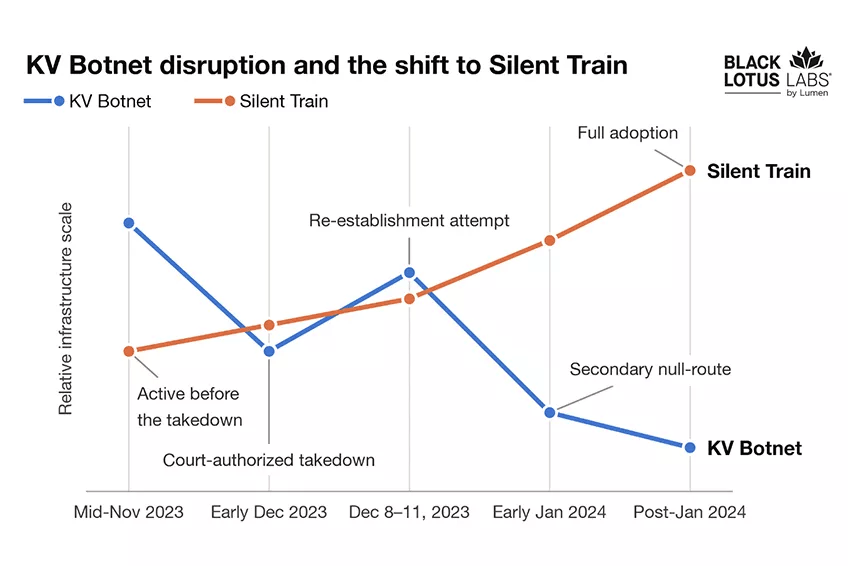
Volt Typhoon Used Silent Train to Hide Zero-Day Attacks
Volt Typhoon used disposable relay chains to hide zero-day attacks on critical systems. Lumen linked Silent Train to at least four zero-days. Lumen’s Black Lotus Labs has spent three years…
SRC // Security Affairs