ARCHIVE
The Hacker News
-
Anthropic’s Claude Fable 5.2 Beats GPT-6 Cyber in Multi-Stage Cyberattack Benchmark
Anthropic on Monday released Claude Fable 5.2 and Claude Mythos 5.2 models, which it said exhibit improvements in coding, reasoning, and vision. During pre-release training, the large language models (LLMs)…
SRC // The Hacker News -
Google Issues Chrome Security Update for Eighth Actively Exploited Zero-Day of 2026
Google on Monday released updates to patch nine security vulnerabilities, including one that has come under active exploitation in the wild. The high-severity vulnerability, assigned the CVE identifier CVE-2026-125350 (CVSS…
SRC // The Hacker News -
N-able Takes N-central Cloud Offline After Researcher Discloses 33 Zero-Days with PoC Exploits
N-able said it has taken N-central Hosted Environments offline and is urging on-premises customers to shut down their servers until further notice following the public disclosure of over 30 vulnerabilities…
SRC // The Hacker News -
CISA Warns of Active Exploitation of OpenSSH, GPUStack, FreeSWITCH, and IBM Flaws
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added four security flaws impacting GPUStack, SignalWire FreeSwitch, OpenBSD OpenSSH, and IBM Aspera Faspex to its Known Exploited Vulnerabilities (KEV)…
SRC // The Hacker News -
Hackers Exploit Qubole’s Trusted AWS Access to Breach Customer Accounts and Steal Data
An attacker broke into AWS accounts belonging to multiple Qubole customers between October 14 and October 26 and stole stored secrets and data, cloud security company Wiz said today. The…
SRC // The Hacker News -
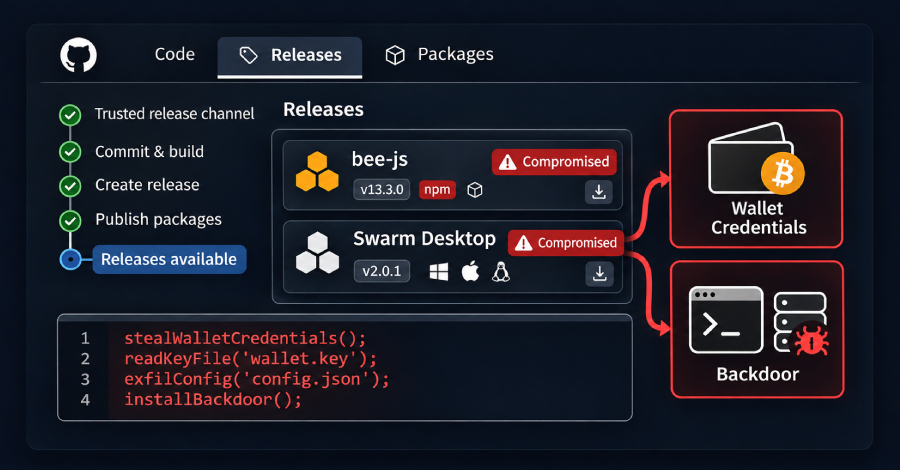
Hackers Compromise Ethersphere’s bee-js and Swarm Desktop to Deliver Wallet-Stealing Malware
Attackers used the Ethersphere project’s own release automation to publish malicious versions of two of its tools for the Swarm decentralized storage network: bee-js 13.3.0 and Swarm Desktop 0.56.2. Both…
SRC // The Hacker News -
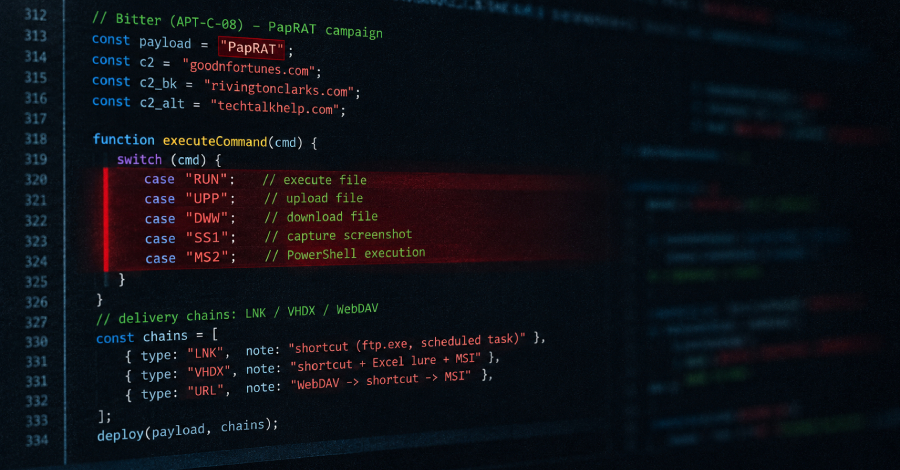
Bitter Hackers Deploy New PapRAT Backdoor in Cyberespionage Campaign Targeting South Asia
The South Asian cyber espionage group known as Bitter (aka APT-C-08, APT-Q-37, Hazy Tiger, Orange Yali, T-APT-17, and TA397) has been observed targeting South Asian organizations with a previously unreported…
SRC // The Hacker News -
⚡ Weekly Recap: SSHole Exploited, APT Root RCE, Robot Takeovers, 15K Hacked Sites, and More
A system doesn’t always need a complicated bug to let someone in. Sometimes, a blank password is enough. That’s one of the bigger stories this week. And it gets worse…
SRC // The Hacker News -
Default ‘admin:admin’ Server Password Helps Researchers Hack Two Automakers, Unlock and Start Cars
The login systems behind two car brands’ mobile apps could be taken over completely, two security researchers found, allowing them to access any customer’s account and, for an owner with…
SRC // The Hacker News -
Web3Auth Flaw Exploited to Steal Keplr Crypto, Provider Empties Other Wallets for Safety
Some people who set up a Keplr crypto wallet with their Google or Apple account have had money stolen by an attacker. Keplr uses a company called Web3Auth to run…
SRC // The Hacker News