ARCHIVE
The Hacker News
-
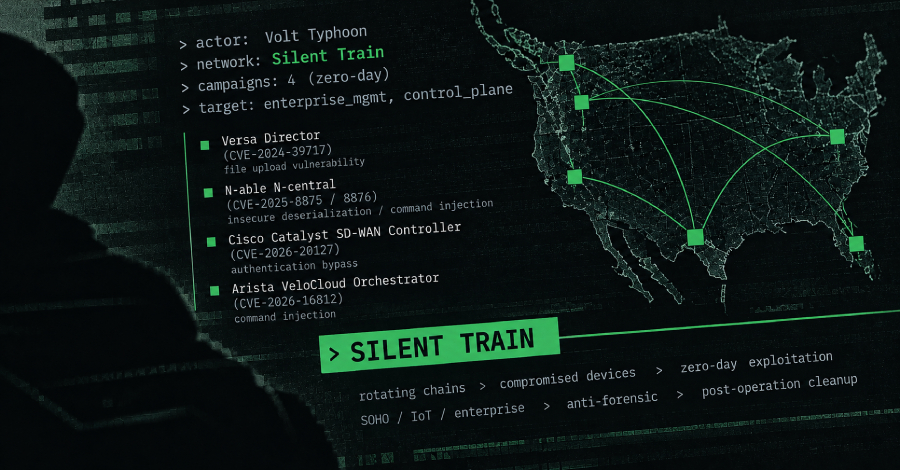
Volt Typhoon Used Covert Silent Train Network in Four Zero-Day Exploitation Campaigns
The China-nexus cyber espionage group known as Volt Typhoon has been attributed to a now-disrupted covert access network dubbed Silent Train that has been put to use for zero-day exploitation…
SRC // The Hacker News -
Google to Allow One-Tap Android App Installs From Approved Third-Party Stores Outside U.S.
Third-party Android app stores can now apply to Google for permission to install apps with one tap, without Android’s usual confirmation screens, and to update them in the background. To…
SRC // The Hacker News -
Researcher Reveals How Logic Bugs Alone Cracked Microsoft Edge in $175,000 Pwn2Own Win
A chain of logic flaws, with no memory corruption, can turn a malicious web page into code running on a Windows computer outside Microsoft Edge’s sandbox, a security researcher has…
SRC // The Hacker News -
PHP2Shell Attack Roots 25 Servers, Breaches U.S. Government-Affiliated Network
Cybersecurity researchers have disclosed details of what appears to be an artificial intelligence (AI)-assisted attack orchestrated by a suspected China-nexus threat actor that has leveraged the PHP2Shell vulnerabilities to breach…
SRC // The Hacker News -
Hackers Target Critical Oracle E-Business Suite RCE Flaw Days After Security Patch
Threat actors are beginning to probe for a newly patched critical vulnerability in Oracle E-Business Suite (EBS), according to threat intelligence firm Defused Cyber. The vulnerability in question is CVE-2026-101767…
SRC // The Hacker News -
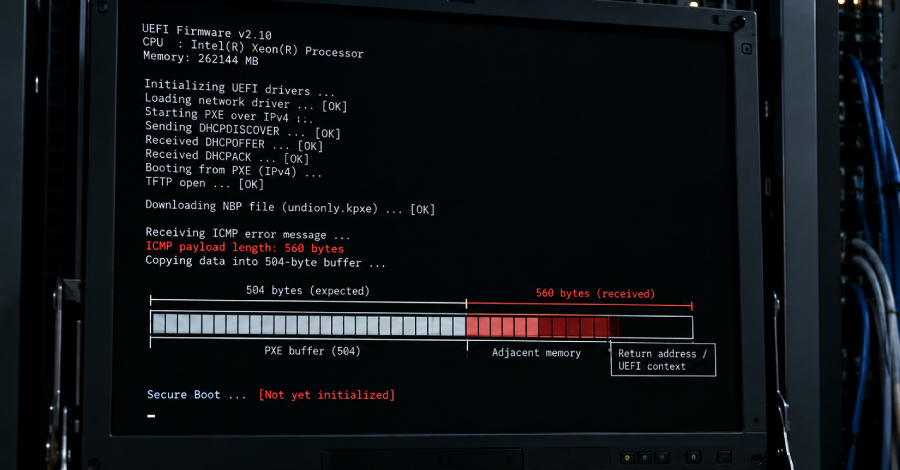
Critical 16-Year-Old UEFI Flaw Can Run Code Before Secure Boot on Network-Booting Servers
A critical 16-year-old flaw in EDK II, the open-source code that most hardware makers use to build UEFI firmware, can allow an attacker to run code on a machine before…
SRC // The Hacker News -
Wazuh and AI for Enhanced SOC Workflows
Artificial Intelligence (AI) has become one of this decade’s defining technologies. From healthcare and finance to manufacturing and education, organizations increasingly rely on AI to automate repetitive tasks, uncover patterns…
SRC // The Hacker News -
Adobe Fixes 8 Critical Campaign Classic Flaws Allowing Code Execution and Security Bypass
Adobe has released patches to address multiple critical security flaws in Campaign Classic that, if successfully exploited, could result in arbitrary code execution, security feature bypass, and privilege escalation. The…
SRC // The Hacker News -
American Organizations Under Attack: Skyw4lker Device Code Phishing Campaign Exposed
Modern phishing campaigns can compromise American businesses without relying on traditional credential theft. Attackers can abuse legitimate cloud services, authentication mechanisms, and trusted business workflows to gain access to corporate…
SRC // The Hacker News -
Anthropic’s Unreleased AI Model Chains Flaws Into Working Chrome, Safari, Windows and Linux Exploits
An unreleased Anthropic AI model found security flaws in Chrome, Safari, Android, Windows, and Linux and chained them into working proof-of-concept exploits, the company said in its latest report. The…
SRC // The Hacker News