ARCHIVE
The Hacker News
-
⚡ Weekly Recap: Critical CVEs, Linux DDoS Botnet, Device-Code Phishing, Android Spyware and More
Some attacks this week didn’t need much of a trick. A fake support call, a trusted extension, a shared link, or a device with no password. Small things that people…
SRC // The Hacker News -
Google Disrupts 1.3 Million-Device Android Botnet, Says TV Box Maker Sold Criminal Access
A botnet of more than 1.3 million Android devices, mostly TV set-top boxes, lost control of its servers in late October in a takedown led by Google. Google says it is…
SRC // The Hacker News -
DarkBlinders Compromises Israeli Target and Iraqi Kurdish Government Cloud Environment
Cybersecurity researchers have disclosed details of a cyber espionage campaign targeting Israel and the Kurdistan Region of Iraq by an Iran state-aligned threat actor between August and October 2026. According…
SRC // The Hacker News -
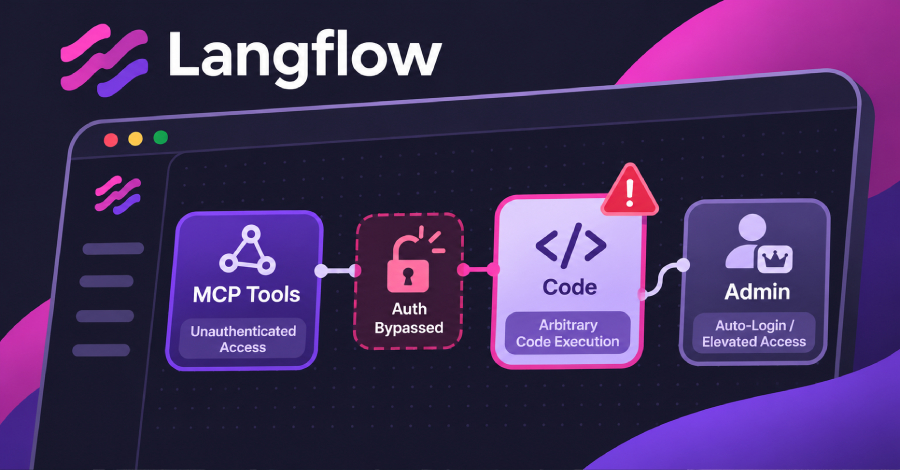
Critical Langflow Flaws Could Let Unauthenticated Attackers Run Code on Servers
Two critical flaws in Langflow could let a remote attacker with no account bypass authentication or run arbitrary code, IBM said last week. Langflow is an open-source tool for building AI…
SRC // The Hacker News -
Is Your SOC Ready for AI Agents? A Maturity Check Before You Deploy
Forty percent of security teams now use AI every day, and another 56% are testing it. Only 4% have no plans to adopt it, according to Prophet Security’s State of…
SRC // The Hacker News -
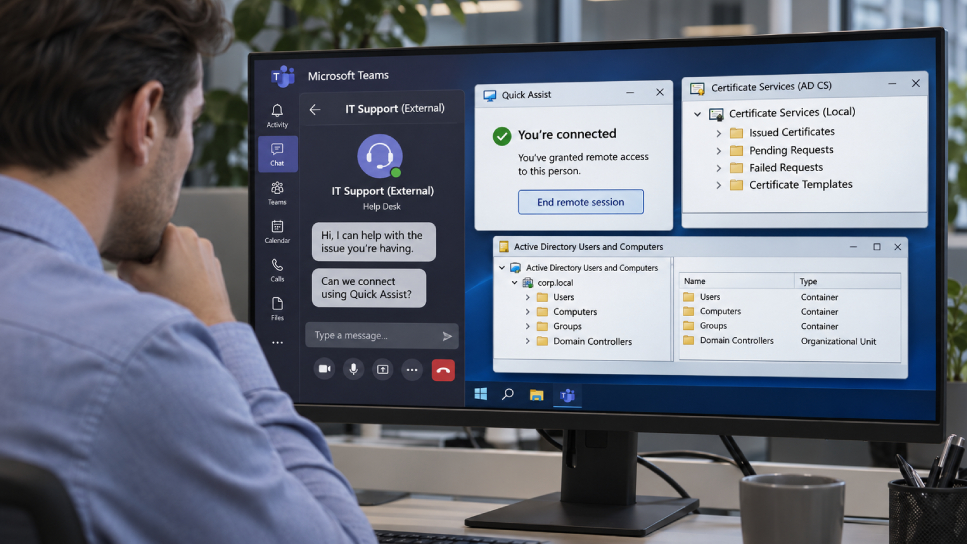
Attackers Pose as IT Support on Microsoft Teams, Abuse AD CS to Steal Company Data
Attackers posing as IT support on Microsoft Teams talked employees into giving them remote control of their PCs. They then used insecure Active Directory Certificate Services (AD CS) settings to…
SRC // The Hacker News -
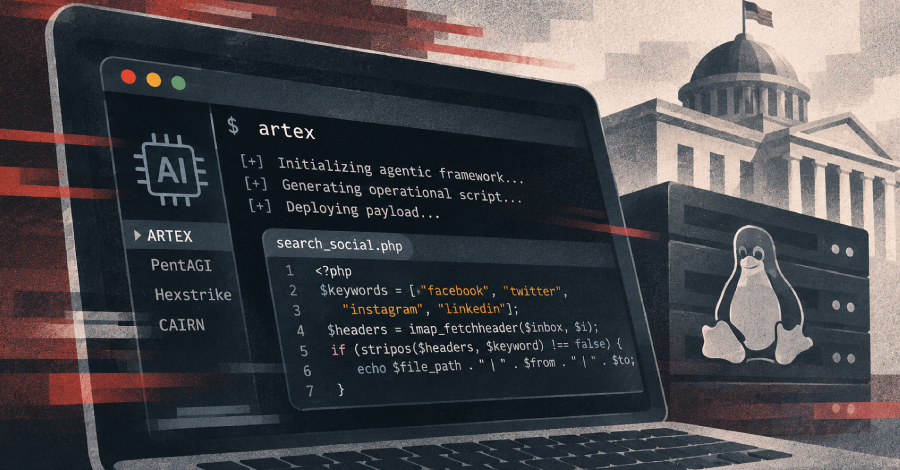
Government Linux Servers Targeted With SysGoRAT and Suspected AI-Generated Scripts
Cybersecurity researchers have disclosed details of a cyber espionage campaign specifically targeting Linux infrastructure associated with government entities and state-affiliated infrastructure. The activity, observed by Palo Alto Networks Unit 42…
SRC // The Hacker News -
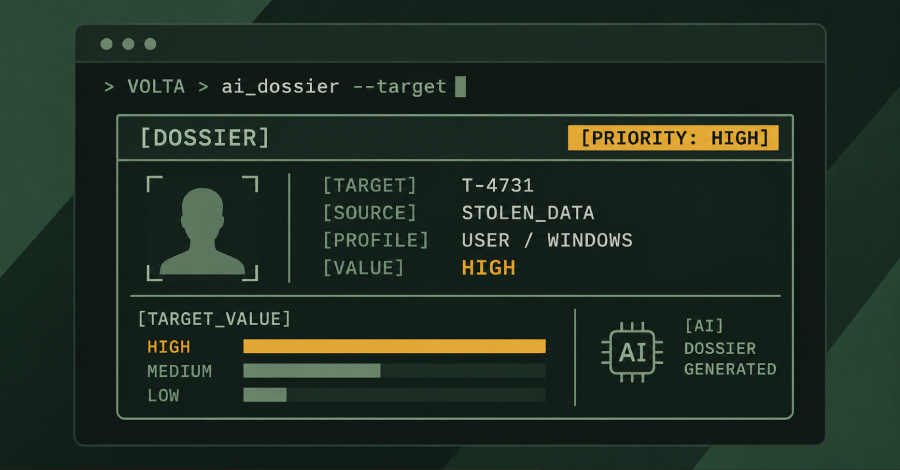
New VOLTA Infostealer Uses Claude, Gemini, and Kimi AI to Rank Victims by Financial Value
Cybersecurity researchers have discovered a new Windows infostealer malware called VOLTA-AUTODOXER (aka VOLTA) that makes use of a large language model (LLM) to rank a victim’s stolen data by their…
SRC // The Hacker News -
CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key
A critical flaw in Canonical’s LXD and MicroCloud let an attacker log in as a trusted client without holding that client’s private key. To do it, the attacker had to…
SRC // The Hacker News -
Hackers Steal About $2.7 Million From Polymarket Traders via Hijacked DebugBear Script
Malicious code on the website of prediction market Polymarket sold some signed-in traders’ positions and moved their funds to the hackers on October 29. The code had replaced a page-speed…
SRC // The Hacker News