ARCHIVE
Security News
-
Active Exploitation of May 2026 PAN-OS CVE-2026-0257 (Updated October 20)
Ransomware operators including Spikey Scorpius (aka Qilin) and Tarnished Scorpius (aka Inc) are exploiting PAN-OS vulnerability CVE-2026-0257. The post Active Exploitation of May 2026 PAN-OS CVE-2026-0257 (Updated October 20) appeared…
SRC // Palo Alto Networks Unit 42 -
Ex-OpenAI Engineer Detained After Planting Secret Recorder at HQ
The perp, who has Saudi ties, was arrested for allegedly bugging an OpenAI conference room, highlighting a preventable insider threat vector.
SRC // Dark Reading -
Close Identity Gaps in Software Development Before Unleashing AI
Artificial intelligence is complicating security in the software development life cycle, but a Dark Reading roundtable found collaboration, better identity visibility, and reduced testing costs offer CISOs a way ahead.
SRC // Dark Reading -
There’s only so much code: the rise in vulnerability numbers
The September Microsoft Patch Tuesday release included 975 vulnerability advisories. This month, 1,415 vulnerabilities were just dropped. Compared to a pre-June average of 100 a month, that increase is staggering.…
SRC // Cisco Talos Intelligence -
Head of AI Security Roles Surge in Large Organizations
A new IANS report has found that despite the growth of the head of AI security role, accountability for AI governance in firms remains unsettled
SRC // Infosecurity Magazine -
Hackers Abuse AI Pen-Test Tool Cairn to Automate Massive Attack Spree
A Chinese-speaking attacker has compromised hundreds of websites across the globe, looting from big fish like John Deere, SharkNinja, and engine manufacturer Cummins.
SRC // Dark Reading -
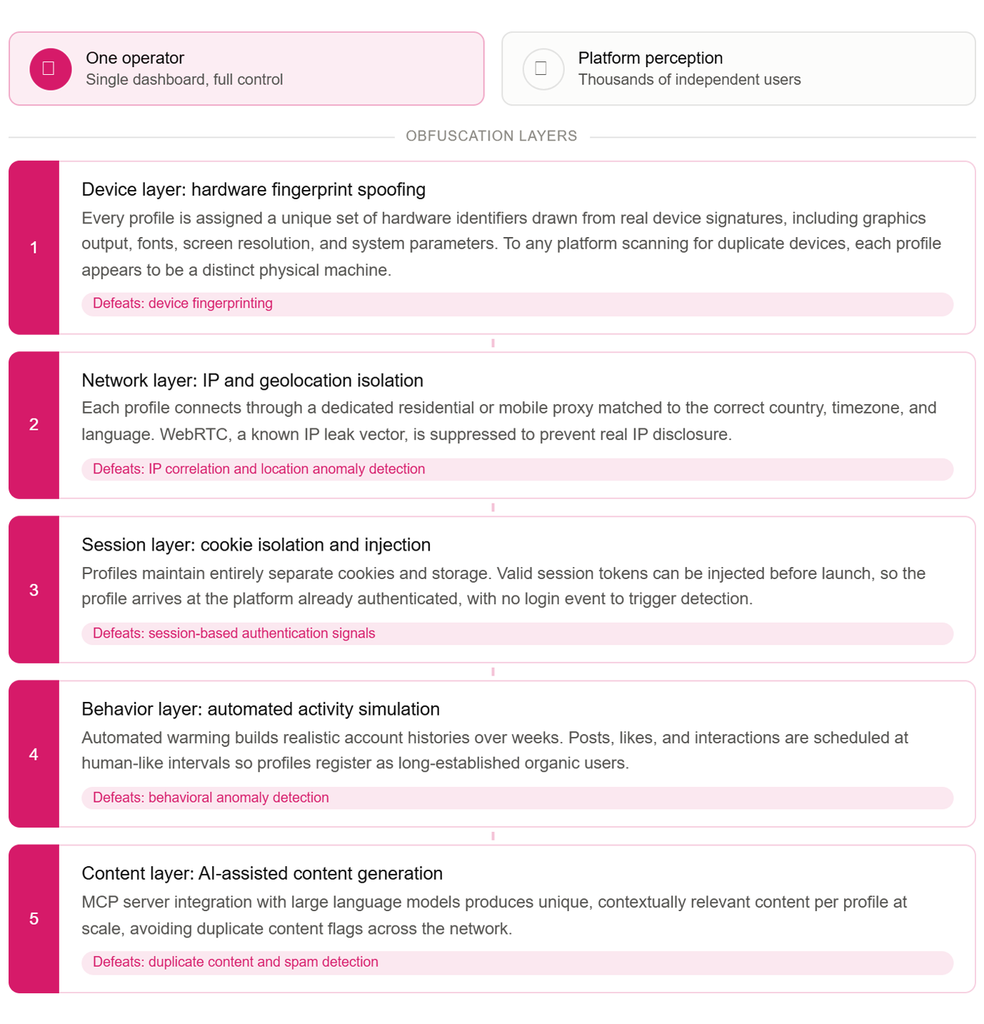
The Risk of AI-Powered Antidetect Browsers in Online Fraud and Influence Operations
Key Findings Introduction Antidetect browsers conceal their users’ digital identities, enabling a single operator or small team to simultaneously run thousands of isolated accounts across multiple platforms such as Facebook,…
SRC // Check Point Research -
Researchers Warn OpenCode Quietly Patched Critical RCE Flaw, Leaving Users At Risk
OpenCode silently patched a critical RCE flaw, leaving vulnerable users unaware of the security risk, researchers at Pillar Security warned
SRC // Infosecurity Magazine -
AI Agent Adoption Creates Risk as Oversight Struggles to Keep Pace, Splunk Finds
Rapid adoption of agentic AI comes with potential business benefits. But if done incorrectly it also carries risks around AI activity management and security
SRC // Infosecurity Magazine -
Possible new Cellebrite iPhone Radio Zero-Day
Justin.sh is reporting on a confidential Cellebrite document that has been leaked to him: Cellebrite calls it Advanced Unlocks (AU from here on), not to be confused with the “advanced…
SRC // Schneier on Security