ARCHIVE
Security News
-
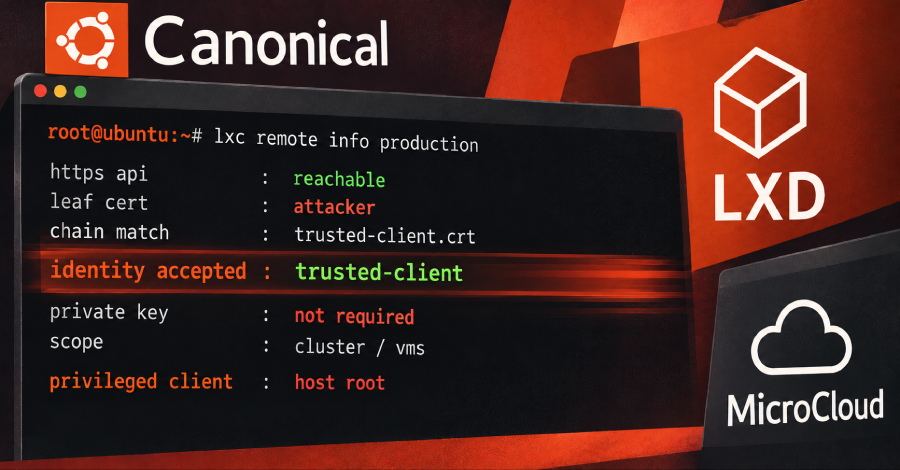
CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key
A critical flaw in Canonical's LXD and MicroCloud let an attacker log in as a trusted client without holding that client's private key. To do it, the attacker had to…
SRC // The Hacker News -
Hackers Steal About $2.7 Million From Polymarket Traders via Hijacked DebugBear Script
Malicious code on the website of prediction market Polymarket sold some signed-in traders' positions and moved their funds to the hackers on October 29. The code had replaced a page-speed…
SRC // The Hacker News -
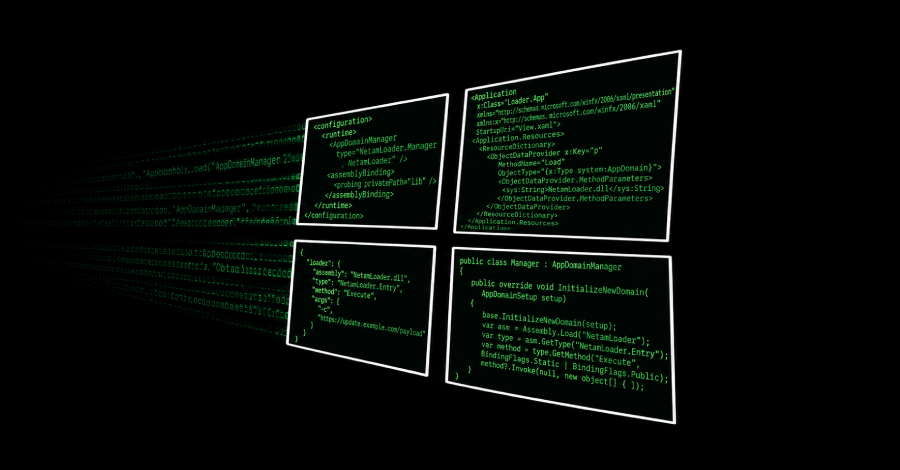
NetamLoader Malware Targets Government Windows 10 Systems in Asia via .NET Injection
Cybersecurity researchers have disclosed details of what has been described as a "highly sophisticated infection chain" targeting government organizations in Asia. The activity, detailed by Kaspersky this week, targeted a…
SRC // The Hacker News -
FBI Links North Korea’s TraderTraitor to Record $6.43 Billion Binance Crypto Heist
The U.S. Federal Bureau of Investigation (FBI) has officially attributed the theft of more than $6 billion in virtual assets to TraderTraitor, a North Korea-aligned elite hacking group also tracked…
SRC // The Hacker News -
U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following Ivanti Connect…
SRC // Security Affairs -
Northflank security breach leads to abuse of customers’ AI API keys
Cloud application hosting platform Northflank is warning customers to rotate all credentials and secrets stored on its platform after a security breach led to unauthorized use of customers' AI API…
SRC // BleepingComputer -
New Android SMS of Death exploit can remotely crash unpatched phones
A security researcher has released a proof-of-concept exploit for a recently patched Android vulnerability, dubbed "SMS of Death" and tracked as CVE-2026-58882, that lets attackers remotely disrupt cellular service or…
SRC // BleepingComputer -
Reddit to lock content behind logins to fight scrapers
Reddit announced in a post by co-founder Steve Huffman that the site will gradually become a "logged-in service," offering limited access to visitors without accounts. [...]
SRC // BleepingComputer -
Chainalysis discloses data breach from “offensive agentic techniques”
Blockchain analytics firm Chainalysis disclosed a data breach after attackers used "offensive agentic techniques" to access internal systems and tools, exposing customer names, email addresses, user IDs, and organizational roles.…
SRC // BleepingComputer