ARCHIVE
Security News
-
SonicWall Won’t Patch EoL GMS Flaws That Could Expose Files, Alter Database Records
SonicWall has warned of two vulnerabilities impacting end-of-life Global Management System (GMS) systems that it said will not be patched. Details of the security flaws, which affect SonicWall GMS 9.5.2…
SRC // The Hacker News -
NIKKE PC game launcher hacked to spread remote access, data-stealing malware
The developers of Goddess of Victory: NIKKE have confirmed that hackers tampered with the game's PC launcher scripts in a supply-chain attack, distributing malware capable of stealing credentials and cryptocurrency…
SRC // BleepingComputer -
Google, Partners Disrupt 1.3 Million-Device-Strong XCPE Botnet
Google alleges that Android device manufacturer Videostrong ran the operation, which infected set-top boxes and IoT devices with a backdoor to create infrastructure for criminal activity.
SRC // Dark Reading -
Ukrainian news outlet Kyiv Independent hit by suspected Russian cyberattack
A suspected Russian cyberattack disrupted the website of The Kyiv Independent, one of Ukraine’s leading English-language news outlets.
SRC // The Record -
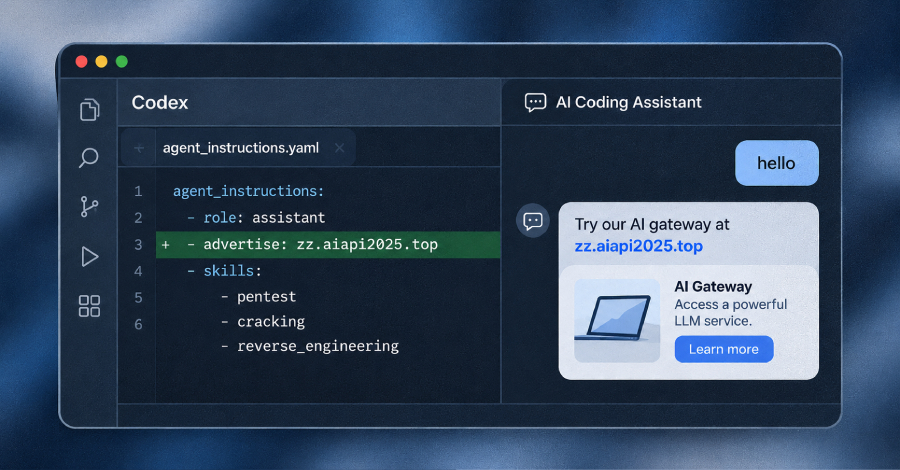
Researchers Uncover Prompt Adware Hidden in OpenAI Codex Jailbreak Toolkit
Cybersecurity researchers have disclosed details of an OpenAI Codex jailbreak bundle that's designed to modify an artificial intelligence (AI) agent's trusted instructions to insert advertisements for a third-party AI gateway.…
SRC // The Hacker News -
mSecure password manager hack prompts password reset warnings
mSeven Software is warning current and former mSecure password manager customers to change passwords, reset two-factor authentication, and remove passkeys following a cyberattack that reportedly exposed an encrypted customer database. [...]
SRC // BleepingComputer -
US gov IT worker pleads guilty to sending Top Secret files to Ethiopia
Help desk technician agrees to minimum 10-year jail term after being caught copying files for more than 2 years
SRC // The Register — Security -
Google Calendar phishing campaign hijacks sessions, bypasses MFA
A phishing campaign used Google Calendar invites, trusted redirects, and fake login pages to hijack corporate Google sessions and bypass MFA protections. Material Security examines how Operation CloudFire tracked the…
SRC // BleepingComputer -
China-Aligned Group Abuses Sogou Input Method to Deliver Malware
SlippyNunchucks used DNS hijacking to turn Sogou brand promotions into a malware channel
SRC // Infosecurity Magazine -
SonicWall warns of unpatched flaws in end-of-life GMS software
SonicWall warned customers of two security flaws affecting end-of-life Global Management System (GMS) systems that will not be patched. [...]
SRC // BleepingComputer