ARCHIVE
Security News
-
Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa
French Bank Crédit Mutuel Arkéa says hackers exploited a service provider to steal up to $133 million using the bank’s own account. French cooperative bank Crédit Mutuel Arkéa was hit…
SRC // Security Affairs -
Week in review: Refrigeration cyberattacks hit European retailers again, Patch Tuesday forecast
Here’s an overview of some of last week’s most interesting news, articles, interviews and videos: The first ten lines of a command policy for AI coding agents In this Help…
SRC // Help Net Security -
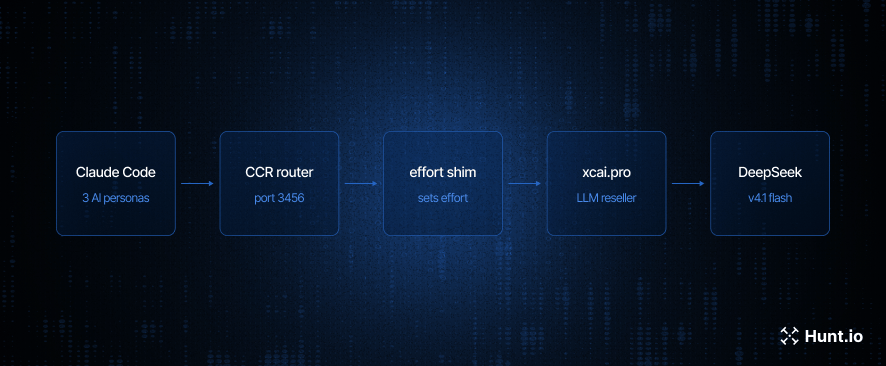
Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches
Hunt.io traced ARTEX servers and AI-powered hacking tools used in breaches affecting seven South Korean financial institutions. Between late September and early October 2026, seven South Korean financial institutions had…
SRC // Security Affairs -
One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers
Software vendors can boost revenue by tracking customer usage across products, while AI accelerates pricing and consumption decisions. It is hard to find any software vendor that sells just one…
SRC // Security Affairs -
Hackers pull off $133 million French bank heist via service provider
French cooperative bank Crédit Mutuel Arkéa was targeted in a cyberattack that enabled fraudulent transactions of up to $133 million, forcing it to respond by suspending certain systems.v [...]
SRC // BleepingComputer -
CTM360 Exposes Fake Gift Card Scams Exploiting Trusted Brands
Scammers are impersonating major brands and celebrities to lure consumers into fake gift card giveaways that collect personal information and trigger unwanted subscriptions. CTM360 reveals how these campaigns use deceptive…
SRC // BleepingComputer -
The Fridge-Hacking Spree Is an Internet-of-Things Wake-Up Call
Escalating hacks affecting blood labs and grocery stores show the very real risks to critical infrastructure that come from basic security lapses involving internet-connected devices.
SRC // WIRED Security -
NHS breach helpline left staff carrying a ‘significant emotional burden’
Team given a day's notice faced distressed callers, safeguarding decisions during project that stretched from 2 weeks to 11
SRC // The Register — Security -
SonicWall Patches Exploited SonicOS Vulnerability That Weakens VPN Logins
CVE-2026-19868 can let attackers holding credentials for a different login method get past SAML checks, including SAML-enforced MFA. The post SonicWall Patches Exploited SonicOS Vulnerability That Weakens VPN Logins appeared…
SRC // SecurityWeek -
U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog
U.S. CISA adds SonicWall SonicOS SSLVPN vulnerability CVE-2026-19868 to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a SonicWall SonicOS SSLVPN flaw, tracked as CVE-2026-19868…
SRC // Security Affairs