Day: October 29, 2026

  • BYOD cyberattack diverts ambulances and cancels classes at University of New Mexico health center

    Ambulances were diverted, surgeries cancelled, and medical students sent home from classes after a ransomware group attacked the University of New Mexico’s Health Sciences Center (HSC) this week.

    Read more in my article on the Fortra blog.

    Source: Graham Cluley · 2026-10-29

  • Firefox and Chrome patch 200+ security flaws combined – update both ASAP

    Firefox and Chrome patch 200+ security flaws combined – update both ASAP

    The latest version of Firefox fixes 167 security vulnerabilities, most of which are of high severity, while the newest version of Chrome patches 52 flaws, four of which are critical.

    Source: ZDNet Security · 2026-10-29

  • U.S. CISA adds Linux Kernel and Broadcom VMWare ESX  flaws to its Known Exploited Vulnerabilities catalog

    U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Linux Kernel and Broadcom VMWare ESX flaws to its Known Exploited Vulnerabilities catalog.

    The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Linux Kernel and Broadcom VMWare ESX vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog:

    Below are the flaws added to the catalog:

    • CVE-2026-41709 (CVSS score of 7.6) Broadcom VMWare ESX Insufficient Logging Vulnerability
    • CVE-2026-46300 (CVSS score of 2.7) Linux Kernel Missing Initialization of a Variable Vulnerability

    In July, Broadcom released patches to address five vulnerabilities affecting VMware ESXi, vCenter, Workstation, and Fusion, including CVE-2026-41709. The vulnerability in VMware ESX is caused by insufficient logging. A malicious user with administrator privileges could perform certain operations on the affected system without those actions being recorded in the logs.

    This could allow an attacker to hide specific activities and make it harder for security teams to detect suspicious behavior, investigate incidents, and determine what happened. The flaw does not itself grant administrator privileges; the attacker must already have them.

    According to CrowdStrike’s 2026 Legal Threat Landscape Report, which said the China-linked threat actor Warp Panda (aka Armory Castle, UNC5221, Clay Typhoon and VerdantBamboo) exploited CVE-2026-41709 as a zero-day in early 2026 to reduce the visibility of its activities in audit logs.

    Warp Panda targets internet-facing edge devices by exploiting zero-day vulnerabilities and deploying custom malware to maintain persistent, covert access. The group also attempts to evade detection by bypassing audit logging, stealing cloud session tokens and registering unauthorized multi-factor authentication (MFA) devices.

    The second flaw added to the catalog is CVE-2026-46300, also known as Fragnesia, could let local attackers gain root access through page cache corruption.

    The flaw affects the XFRM ESP-in-TCP subsystem and could allow local attackers to gain full root access by corrupting the kernel page cache.

    Security experts warn that the issue is dangerous because attackers with low privileges can modify read-only files in memory and take complete control of vulnerable systems. The vulnerability was discovered by William Bowling of the V12 security team, while Wiz published a detailed technical analysis.

    “The vulnerability allows unprivileged local attackers to modify read-only file contents in the kernel page cache.” reads the report published by Wiz. “Attackers can then achieve root privileges through deterministic page-cache corruption.”

    Fragnesia shares similarities with earlier Linux privilege escalation flaws, such as Dirty Frag and Copy Fail. According to researchers, the bug can reliably provide root access on major Linux distributions without requiring race conditions or complicated timing attacks.

    According to Binding Operational Directive (BOD) 22-01: Reducing the Significant Risk of Known Exploited Vulnerabilities, FCEB agencies have to address the identified vulnerabilities by the due date to protect their networks against attacks exploiting the flaws in the catalog.

    Experts also recommend that private organizations review the Catalog and address the vulnerabilities in their infrastructure.

    CISA orders federal agencies to fix CVE-2026-41709 by November 11, 2026, while CVE-2026-46300, must be fixed by October 31, 2026.

    Follow me on Twitter: @securityaffairs and Facebook and Mastodon

    Pierluigi Paganini

    (SecurityAffairs – hacking, CISA)

    CVE-2026-41709

    Source: Security Affairs · 2026-10-29
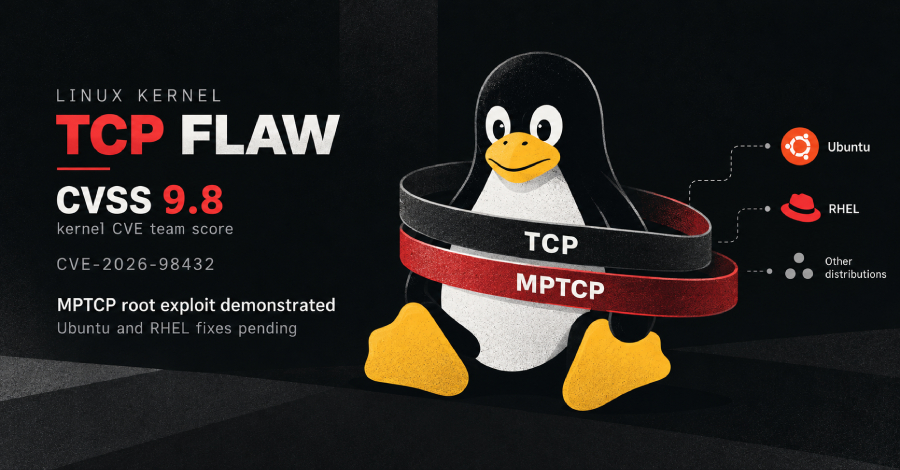
  • Linux Kernel TCP Flaw With 9.8 CVSS Score Affects Ubuntu, Red Hat and Other Distributions

    Linux Kernel TCP Flaw With 9.8 CVSS Score Affects Ubuntu, Red Hat and Other Distributions

    A flaw in the Linux kernel’s TCP code, tracked as CVE-2026-98432, affects Ubuntu, Red Hat Enterprise Linux (RHEL), and other Linux distributions. The kernel’s own CVE team rates it 9.8 out of 10 on the CVSS scale.

    Anthropic said on October 27 that its AI model wrote an exploit that uses the flaw to let a remote attacker with no credentials run commands as root on Linux servers with a

    Source: The Hacker News · 2026-10-29

  • Threat Modeling With 4 Simple Questions on a White Board

    Threat Modeling With 4 Simple Questions on a White Board

    A four-question exercise that CISOs can use to create a threat model that promises results, without a big spend.

    Source: Dark Reading · 2026-10-29

  • Stop sharing your passwords with AI agents, Bank of America warns customers

    Stop sharing your passwords with AI agents, Bank of America warns customers

    The bank’s message follows a trend among financial institutions that are restricting third-party AI agent access.

    Source: ZDNet Security · 2026-10-29

  • EMBRACE Flaws in 5 AI Coding Tools Enable Code Execution and File Theft

    EMBRACE affects AI coding tools Cursor, GitHub Copilot, Codex, VS Code and Claude Desktop, enabling code execution, file theft and browser address-bar spoofing.

    Source: HackRead · 2026-10-29

  • Fake ChatGPT and Claude Apps Abuse Signed Executables to Deploy Crypto Miners

    Fake ChatGPT and Claude Apps Abuse Signed Executables to Deploy Crypto Miners

    Threat actors are delivering malicious loaders and cryptocurrency miners under the guise of artificial intelligence (AI) desktop applications for Anthropic Claude and OpenAI ChatGPT as part of a campaign dubbed Yoba.

    The activity involves creating fake GitHub projects that claim to be desktop applications like GPT-5.6 Sol, GPT-6 Astra, and Claude Opus, only to deliver a malware family called

    Source: The Hacker News · 2026-10-29

  • NIK C2 Malware Can Use Victims’ OpenAI Keys for AI Queries

    NIK C2 malware can fall back on victims’ OpenAI API keys to run AI queries

    Source: Infosecurity Magazine · 2026-10-29

  • Belgium’s tax agency confirms cyberattack, pulls services offline

    Belgium’s tax agency confirms cyberattack, pulls services offline

    Belgium’s finance and tax agency has pulled “several” digital services offline after a cyberattack on the organization. FOD Financiën confirmed the attack on Wednesday, saying that MyMinfin, the agency’s main online tax portal, as well as other online services, are temporarily unavailable while they start the initial investigations. “This measure helps limit the risks and makes it possible to carry out the necessary technical interventions to ensure the security of our systems,” it said in a public announcement. FOD Financiën added that “this has consequences for tax deadlines in the near future,” referring to the October 31 extended deadline to submit tax filings for specific types of income, such as sole traders and earnings from foreign companies. The agency confirmed the deadline will be extended to November 16, by which time MyMinfin, the platform through which such filings would normally be submitted, should be back up and running. The detail offered up in the public statement reflects the early stage of the investigation; not much is known, although there is nothing to suggest data was compromised. “Data protection is a top priority for the FOD Financiën,” it said. “At present, there are no indications that a data breach has occurred or that data has been compromised. This aspect is also being closely investigated and followed up. “In the meantime, a large part of our other applications remains available with full or partial functionality. We are closely monitoring the situation and doing everything we can to make the affected services available again as soon as possible.” Spokesperson Francis Adyns told local news outlets that the attack was thwarted within hours, and that it was unable to gain access to applications or data. “The attack could not be sufficiently expanded within our environment to take over applications or gain access to data,” he told Nieuwsblad. “Elements that were potentially infected were isolated. As a result, MyMinfin, Tax-on-web, and Biztax went offline, but the hacking was successfully stopped. “The various services must be restored in an isolated environment. This requires considerable time to realize, with the necessary caution to rule out new risks.” ®

    Source: The Register Security · 2026-10-29