Day: October 26, 2026

  • Cybersecurity CEO Indicted for Allegedly Scamming Millions From Ransomware Victims

    Cybersecurity CEO Indicted for Allegedly Scamming Millions From Ransomware Victims

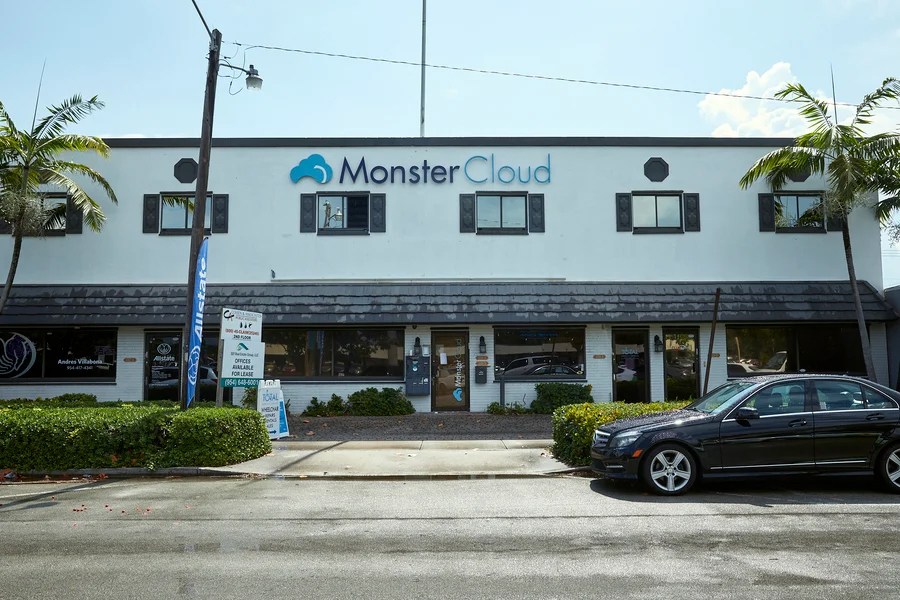
    Palm trees and green hedges grow in front of a white two-story building with a sign that reads MonsterCloud.
    A federal grand jury indicted Zohar Pinhasi last month for allegedly defrauding clients of his ransomware data recovery business, MonsterCloud. Jeffery Salter, special to ProPublica

    A Florida man who was the subject of a 2019 investigation by ProPublica was indicted last month on federal charges that he defrauded clients of his ransomware data recovery firm. 

    According to the Justice Department, the man, Zohar Pinhasi, told customers he could recover their encrypted files without having to pay hackers, when, in reality, he paid the ransom and charged victims a hefty fee on top.

    The indictment mirrors the findings from ProPublica’s 2019 article “The Trade Secret,” which centered on Pinhasi and his scheme. The outlet found that the ransomware victims were being harmed twice: once by the hackers, who locked their targets’ files and demanded ransom, and a second time by MonsterCloud, Pinhasi’s Florida-based data recovery firm, which misled its clients about not paying ransoms.

    “By falsely claiming to decrypt ransomware without paying off the ransomers, the defendant re-victimized his clients while extracting a hefty profit for himself,” U.S. Attorney Joseph Nocella said in an Oct. 7 press release. “Our Office will vigorously prosecute ransomware attackers who prey on Americans from across the world and those who cynically profit from their criminal activity.”

    When ProPublica published its story in 2019, ransomware was growing into one of the world’s most pervasive cyberthreats. Hackers locked the data of governments, schools and businesses, holding the decryption key for a ransom payment, which they usually demanded in bitcoin and other types of difficult-to-trace cryptocurrency. 

    ProPublica’s reporting focused on how U.S. industries, from data recovery firms like MonsterCloud to insurance giants that cover ransom payments, all fueled the extortion economy. Ransomware remains a widespread threat today, and the threat to national security has grown as hackers linked to hostile foreign governments are believed to use ransomware as a cover for espionage. The prevalence of AI tools is also making it easier for attackers to spread ransomware.

    Pinhasi, who went by the alias Zack Green, told ProPublica in 2019 that MonsterCloud never promised clients that their data will be recovered by any particular method. “How we do it, it’s our problem,” he told ProPublica. “You will get your data back. Sit back, relax and enjoy the ride.” He called MonsterCloud’s data recovery methods a “trade secret.”

    Pinhasi hung up when reached on his cellphone this month. A message left with a representative at MonsterCloud’s office phone number and a message left with his attorney were not returned. A spokesperson for the U.S. Attorney’s Office said Pinhasi pleaded not guilty to the federal charges.

    In its 2019 investigation, ProPublica interviewed MonsterCloud’s clients and ransomware experts and found that in certain cases the firm must have paid ransoms on behalf of clients. MonsterCloud’s services were particularly popular with local law enforcement agencies, who are loath to engage with or pay criminal hackers. Several interviewed by ProPublica at the time said they chose MonsterCloud to help them recover from ransomware because they believed the firm would never pay a ransom.

    Pinhasi, who described himself to ProPublica as a former IT security intelligence officer for the Israeli military, said in 2019 that MonsterCloud handled up to 30 calls a day and had about 20 employees in South Florida as well as extensive global contacts. 

    Federal investigators found that, over the course of the scheme, Pinhasi allegedly charged clients more than $19 million and paid more than $8 million in ransom payments. In one example, Pinhasi made a ransom payment of about $8,200 but charged the client about $150,000. If convicted, he faces up to 20 years in prison.

    In the Justice Department’s October press release, an FBI official said Pinhasi had “turned the victim’s crisis into his own profit center. This deception is unacceptable, and the FBI is committed to ensuring accountability for those who choose to victimize the very people who trusted them for help.”

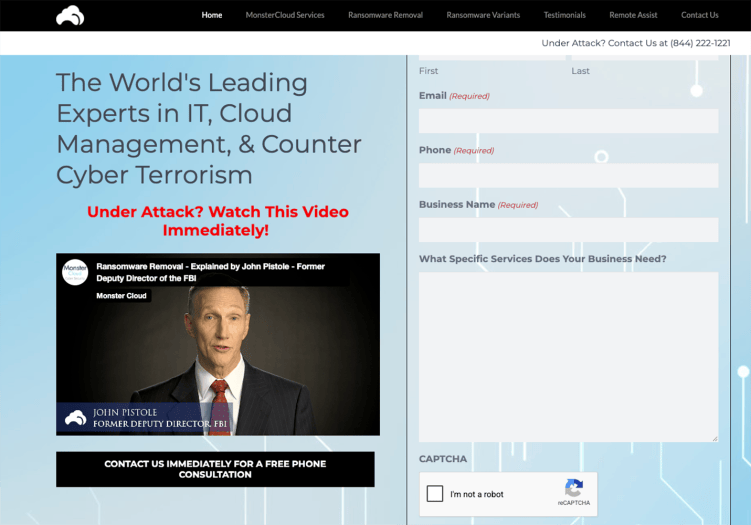
    The Justice Department did not address ProPublica’s 2019 finding that one of the FBI’s own was among Pinhasi’s associates at MonsterCloud. John Pistole, a former deputy director of the FBI under Robert Mueller, was prominently featured in a promotional video on MonsterCloud’s homepage. “Police departments, government agencies, hospitals, small business and Fortune 500 firms trust MonsterCloud to help recover from attacks and protect against new ones,” Pistole said in the video. “MonsterCloud’s proprietary technology and expertise protects their professional reputations and organizational integrity.”

    Pistole was not mentioned by name in the Pinhasi indictment.

    In 2019, Pinhasi touted MonsterCloud’s ties to law enforcement as evidence of its integrity. Pistole, who also headed the Transportation Security Administration under President Barack Obama, was listed on MonsterCloud’s website as the only member of its “Cyber Security Advisory Council.” 

    Pistole did not respond to a request for comment for this story. In a 2019 interview, he said he became acquainted with Pinhasi after MonsterCloud reached him through a speaker’s bureau and that MonsterCloud paid him indirectly through that group. He said Pinhasi scripted his testimonial and that he was well aware that in most cases — including MonsterCloud’s — the only way to decrypt data locked by ransomware is to pay the hackers. “That’s the business model as I understood it,” Pistole told ProPublica at the time. “Based on my experience and knowledge, ransom is paid and they facilitate the best practices moving forward.”

    A spokesperson for the U.S. Attorney’s Office declined to comment on Pistole’s connection to MonsterCloud.

    A webpage with the words: “The World’s Leading Experts in IT, Cloud Management, & Counter Cyber Terrorism. Under Attack? Watch This Video Immediately!” A video appears showing a man with short cropped hair wearing a suit and tie with the caption: John Pistole, Former Deputy Director, FBI.
    John Pistole, a former deputy director of the FBI under Robert Mueller, was prominently featured in a promotional video on MonsterCloud’s homepage. Screenshot by ProPublica

    Source: ProPublica · 2026-10-26

  • Hungarian Tycoon’s Firm Funded Pro-Orbán Advertising Agency, Records Show

    Hungarian Tycoon’s Firm Funded Pro-Orbán Advertising Agency, Records Show

    A firm owned by Hungarian construction mogul László Szíjj — who amassed a fortune under previous Prime Minister Viktor Orbán — donated about $863,000 to Megafon, a political advertising agency that promoted the former ruling party. 

    The donations are detailed in two years of annual financial statements from Szíjj’s firm, Vakond Via Kft., which were examined by OCCRP and Direkt36. The company made “cash grants” that totaled 300 million Hungarian forints to Megafon Digital Incubator Center, adding up to about $252,000 in 2024, and $611,000 the following year.

    Launched in 2020, Megafon became one of Hungary’s most influential political advertising agencies, mainly running social media campaigns in support of Orbán’s Fidesz party.

    But since Orbán’s stunning electoral defeat in April, after 16-years in power, Megafon has kept a low profile. The company’s website was taken offline in August, and its employees have fallen from 72 to three, according to information from a firm that provides commercial registry data.

    Neither Megafon nor Szíjj responded to requests for comment. 

    Megafon’s situation mirrors the condition of other media organizations that backed Fidesz, and received generous state advertising contracts or donations from government-friendly entrepreneurs. 

    Since coming to power, Hungary’s new prime minister, Péter Magyar, has taken steps to halt state advertising being funneled into pro-Fidesz media. Some outlets have stopped publishing, while others have downsized as their budgets dried up.

    OCCRP and Direkt36 recently reported that Megafon had received about $12 million between 2022 and 2024 from a firm owned by Lőrinc Mészáros, another wealthy pro-Orbán businessman. Mészáros, who is also a business partner of Szíjj, did not respond to questions at the time. 

    Magyar cited those findings in a Facebook post following publication, saying the reporting confirmed that Mészáros’ firm, while “funded by public money,” had supported Megafon’s “propaganda.” Magyar asked in the post how long the State Audit Office would “remain silent” about the funding.

    The State Audit Office has confirmed to Direkt36 it is investigating finances around this year’s election. 

    “The audit naturally includes an evaluation of news reports and conclusions published in the press, including an examination of Megafon’s activities,” the office said in an emailed response to questions.

    It is unknown if Szíjj’s firm, Vakond Via, made donations to Megafon this year. Vakond Via’s 2026 annual financial reports are not yet available, and the company did not respond to a request for comment. 

    Vakond Via is part of Szíjj’s sprawling Duna Group of companies. The conglomerate’s flagship firm, the road-building company Duna Aszfalt Út és Mélyépítő Ltd., “won the highest value of public contracts” in a ranking compiled by Transparency International. 

    The anti-corruption group’s Hungarian chapter calculated that Duna Aszfalt received around $2 billion worth of public contracts between 2018 and 2020.

    Source: OCCRP · 2026-10-26

  • PHP2Shell: No login, no app code, no warning. What next?

    PHP2Shell: No login, no app code, no warning. What next?

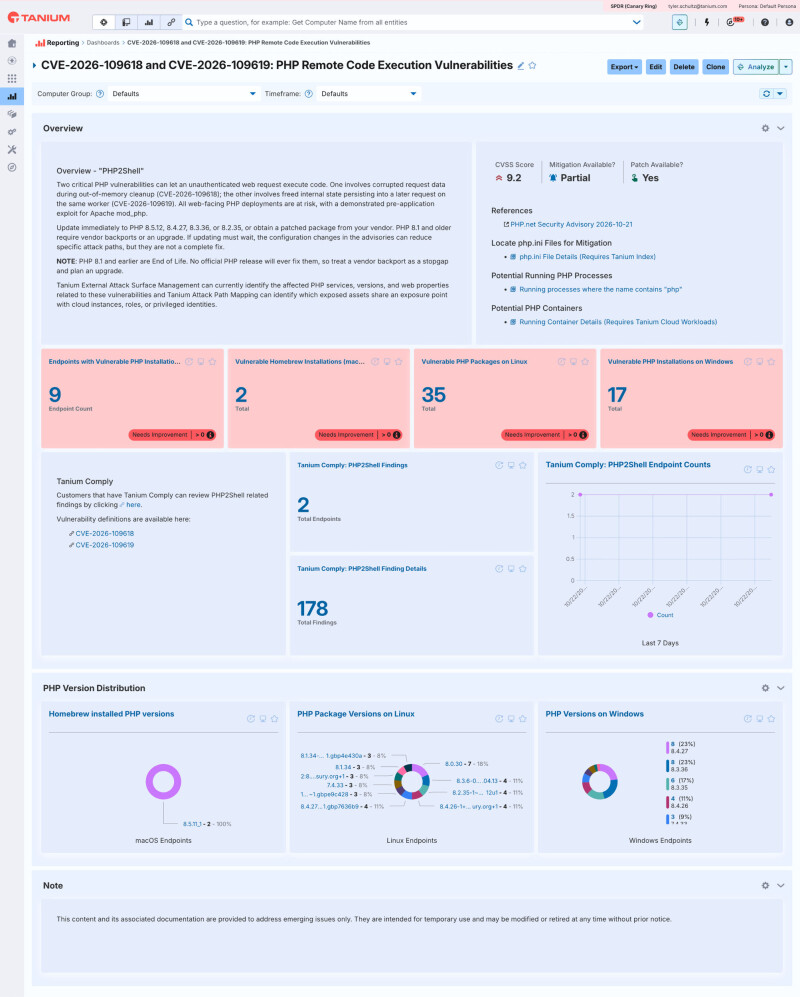
    If you run PHP anywhere in your environment, patch to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now. Two critical flaws disclosed last week, CVE-2026-109618 and CVE-2026-109619 (nicknamed “PHP2Shell”), let an unauthenticated attacker run code on a server with nothing more than a crafted web request. Both carry a CVSS v4.0 score of 9.2, every earlier release is affected, and exploitation in the wild has been reported. The patch is the easy part. The hard part is finding every copy of PHP you own, because PHP rarely shows up where you expect it. This post covers what the flaws are, how far exploitation has gone, and how to get to full coverage fast. What happened Details leaked before the planned embargo, so the PHP security team moved fast and shipped fixes within about a day of announcing them. The two vulnerabilities Both bugs live in PHP core, not in any framework or plugin, so they reach anything that runs PHP to serve web requests. Affected server setups include PHP-FPM, mod_php, php-cgi, FrankenPHP and LiteSpeed. PHP rates mod_php as the highest risk. No login is needed: the attacker only has to reach a PHP endpoint over HTTP. Fixed versions: 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Every earlier release is affected. PHP has also published minimal source backports for 7.4, 8.0 and 8.1, but there are no official releases for those branches. Treat a backport as a stopgap and plan the upgrade. Is it being exploited? Yes, though reliable public exploits are still scarce. watchTowr reports exploitation in its honeypot network as of October 21, and Tenable relays Cloudflare’s CTO saying Cloudflare is seeing early attacks. Other telemetry, such as Patchstack’s, shows mostly probing so far. Neither CVE is in CISA’s KEV catalog yet, and no public indicators of compromise have been released. How hard the bug is to weaponize depends on the platform. VulnCheck reproduced both flaws and found: Code execution works on ARM64, and on x86 systems where address space layout randomization (ASLR) is turned off. Dozens of public proof-of-concepts exist, but very few work and none bypass ASLR on x86-64. Red Hat likewise rates RCE as hard in practice on default PHP-FPM deployments. Don’t read that as permission to wait. Exploits mature quickly once a patch diff is public, and fake PoC repositories for headline CVEs often carry malware, so treat any you find with caution. Tanium’s research on exploitability is in Why PHP2Shell is real(opens in a new tab). Most at risk: internet-facing PHP applications, especially those running mod_php or on ARM64 hosts. It’s also worth retro-hunting recent web server and PHP-FPM logs for unexplained worker crashes and unusual multipart requests. Why finding PHP is harder than it looks No one has a complete list of PHP-based applications, and anything custom-built won’t be on any list. PHP hides in several places at once: OS packages on Linux (php, php-fpm, php8.x), which package managers and most inventory tools see. Homebrew and similar on macOS, outside the system’s own package list. Bundled copies on Windows. PHP on Windows usually arrives as a zip extracted to a folder or inside a stack like XAMPP, WampServer, Laragon or a vendor product. It often never registers as an installed application at all. Applications that ship their own PHP, where the fix depends on the application vendor rather than the OS. Containers, where the version is baked into the image tag. PHP is often more widespread than teams expect, and it doesn’t only run on servers. Developer tools, local web stacks and bundled applications put it on workstations too, often without registering as an installed application. The reliable answer is to look at the binaries themselves. In testing, PHP builds from version 5 through 8 all embed their version string (X-Powered-By: PHP/x.y.z), so you can read the exact version straight from the file without running it. How Tanium helps Tanium itself is not affected. Tanium does not use PHP, so there is no impact to Tanium software or Tanium Cloud services. Tanium Guardian content for PHP2Shell is available now in Tanium Cloud. The dashboard shows where PHP is installed and running so you can prioritize patching, with a single fleet-wide count of endpoints with vulnerable PHP across Linux, Windows and macOS. It combines: The existing Installed Applications and Homebrew Applications sensors, which find PHP installed through package managers on macOS and Linux. A Windows PHP Installations sensor that finds PHP where Installed Applications can’t see it, including IIS, XAMPP, WampServer, Laragon, package managers and manually extracted copies, and reports version, install type, install path and owning user. The version is read from the binary’s file metadata without executing it. A pre-built Saved Question that lists running PHP processes so you can prioritize systems that may be serving traffic. A pre-built Saved Question that identifies PHP containers, matching running containers against php, FrankenPHP and about 25 common PHP-based images such as WordPress, Drupal, Joomla, Nextcloud and Magento. Requires Tanium Cloud Workloads. Tanium Comply finds PHP on disk. For customers licensed for Comply, the dashboard includes PHP2Shell findings by endpoint, full finding details and a 7-day trend, with a pivot to the Comply findings page filtered to the two CVEs. The finding details report shows the specific on-disk locations where PHP was found, which catches copies that package and registry inventories miss. Vulnerability Library definitions for Windows, Linux and macOS are live now — sync the TVL and run an assessment to pick them up. On-premises customers can import the Guardian content manually today. Steps and downloads are in Guardian content for on-premises customers(opens in a new tab) on the Tanium Help Center. Know what’s exposed to the internet. More than 13 million internet-facing assets run PHP versions that may be affected, according to Censys Internet Intelligence. Tanium External Attack Surface Management (EASM) discovers the internet-facing assets tied to your organization and identifies the PHP services, versions and web properties among them, with these CVEs surfaced through its coverage of exploitable and weaponized vulnerabilities. Tanium Attack Path Mapping then shows which of those exposed assets share an exposure point with a cloud instance, role or privileged identity: the places where one exploited PHP server becomes a route deeper into your environment. Already using Tanium SBOM? Inventorying PHP versions there is a sound early step. It shows which applications carry a vulnerable PHP and need a vendor update. What to do now Work through these in order; the first three matter most today. Find every PHP install, including Windows copies that never registered as applications. Record the exact version of each. Rank by exposure. Internet-facing servers, mod_php setups and ARM64 hosts come first. Patch to 8.5.12, 8.4.27, 8.3.36 or 8.2.35 through your OS vendor, a php.net build or your application vendor. Restart PHP-FPM and web server workers so the new binary is loaded. If you can’t patch yet, isolate internet-facing PHP apps where you can, as CERT-EU advises, and put WAF or IDS rules in front of them (Cloudflare and VulnCheck have both shipped rules for the known vectors). Apply the partial setting with care. session.upload_progress.enabled=0 blocks one demonstrated path for CVE-2026-109619 only and does nothing for CVE-2026-109618. It must be set in php.ini, an FPM pool or server config, followed by a worker restart; ini_set() and .user.ini won’t apply it. Hunt. Review recent web server and PHP-FPM logs for worker crashes and malformed multipart uploads. Plan off end-of-life PHP. Anything on 8.1 or older has no official fixed release. Where fixed packages stand (as of Oct 21, 16:30 UTC) Distro packages are still rolling out, so check your vendor before assuming a fix is available. The Remi repository won’t ship updates today, so PHP advises switching to distro packages or building from source if you depend on it. Read more here. Supplied by Tanium

    Source: The Register — Security · 2026-10-26

  • Work to protect DNS from quantum decryption attacks is speeding up

    Work to protect DNS from quantum decryption attacks is speeding up

    Internet governance bodies are likely to accelerate work to prepare the domain name system (DNS) so it can remain secure once quantum computers can challenge conventional encryption. John Crain, ICANN’s chief technology officer, last week told The Register that he is aware of efforts within the organization, and at other internet governance bodies, to consider what happens once commercially available quantum computers become capable of easily deciphering encrypted information. Those machines theoretically pose a risk to DNSSEC, the Domain Name System Security Extensions that adapt PKI to the job of verifying the veracity of DNS records. The CTO said he’s aware of predictions that such computers could come online “at the turn of the decade” and that he has therefore changed his view of when the DNS needs to be made quantum safe. “If you asked me years ago, I would have said we probably need to be ready in ten years,” Crain said. “Now, maybe it’s less than that. I don’t know if it’s three years or five, but it’s probably not ten”. One way to quantum-proof DNSSEC is to use larger keys that even a quantum computer will struggle to crack. Doing so, however, runs into message size limits in the DNS. “If we go for larger key sizes, that means larger zones, larger packets, larger responses,” Crain said. It can also mean traffic being carried by multiple TCP packets, instead of the single UDP messages DNS prefers. Crain said ICANN, the IETF, and other internet governance bodies are aware of this challenge and have begun preliminary work to address it. “Being prepared to go from UDP to TCP is going to take a few years,” he told The Register at ICANN’s annual meeting in Bali last week. “We’re probably a few years away from being able to deploy in a predictable manner.” The internet community has, however, seen that the problem is becoming more acute. “We’re going to ramp up the speed of development,” Crain said. Internet registry reform nears At ICANN’s Bali conference, The Register also met Jia-Rong Low, in his capacity as chair of the Number Resource Organization, the peak body for the world’s five regional internet registries (RIRs), AFRINIC, APNIC, ARIN, LACNIC, and RIPE NCC. The topic of that conversation was Internet Coordination Policy 2 (ICP-2), the document that governs RIRs. In its current form, ICP-2 describes the formation of a new RIR but no other part of its operations. After strife at AFRINIC raised the possibility of the African registry failing, the NRO decided to update ICP-2 so it covered the entire lifecycle of an RIR, from formation through to possible derecognition. Work on ICP-2 has moved through several rounds of public consultation. It has reached the status of a recommended draft. Low told The Register work on the document has proven “very challenging” to develop entirely with remote work. Last week’s ICANN meeting, he said, offered a venue for in-person collaboration that he hopes will result in work accelerating. The revised document defines four stages in the life of an RIR: recognition, audit, emergency continuity operations, and derecognition. The last three are additions to ICP-2 and give ICANN a major role as an independent overseer of RIRs. Low is hopeful a final document will be ready for review by the end of 2026, and ready for implementation not long afterwards. Scammers target trustworthy-sounding domains like .bank or .pharmacy Phisherfolk and other scammy scum strive to register authoritative-sounding domains as part of their efforts to trick victims. ICANN defines some global top level domains (GTLDs) as “Category 1” strings, because they pertain to regulated sectors – such as .bank, .doctor, and .university – or are felt to need special safeguards because like .sucks they create the potential for bullying. In a session at the ICANN meeting, Siôn Lloyd, ICANN’s principal security, stability and resiliency scientist, said the organization has investigated whether certain top level domains attract more abuse. He found that Category 1 GTLDs are more likely to be targeted by DNS abusers and therefore have a 45 percent higher chance of abuse than other domains. Happily, Category 1 domains are also less likely to have high abuse volumes. ICANN is currently working on a policy (PDP1) that will require domain registrars to take extra action against owners of domains that facilitate abuse, and another (PDP2) that will regulate automated domain registration. More GTLDs, more often? The Register heard plenty of chat at the meeting about ICANN’s new round of applications for GTLDs, which seems to be progressing well. Across various panels and sessions, we also heard references to ICANN’s past statements that new GTLD application rounds should be more frequent and take place at a predictable cadence, along with some suggestions that this round of applications is the template for future rounds. ®

    Source: The Register — Security · 2026-10-26

  • How Beijing’s Africa ambitions, financed by China’s mega banks, triggered a crisis in Zambia

    How Beijing’s Africa ambitions, financed by China’s mega banks, triggered a crisis in Zambia

    As Kanangwa Newlove walked through her 10-acre farm just outside Lusaka, Zambia, one day in October 2025, she felt as if her dreams were withering away in front of her. The spinach, lettuce and mustard wilted in the heat. Tomatoes shriveled on their vines. She uprooted entire rows of organic vegetables — once sought-after by discerning customers, now rotting in the sun — and fed them to her pigs. “The crops that suffered the most without water were our mainstay,” she told a reporter for the International Consortium of Investigative Journalists. “There was nothing we could do. There was no water for the crops because there was no electricity.”

    Every few days, she needed nearly 8,000 gallons of water from borehole pumps to keep her farm going. The pumps required a reliable supply of electricity, but since March 2024, Zambia’s rolling blackouts had left swathes of the country without power, turning everyday tasks into Herculean struggles. Sometimes she had only four hours of power a day.

    The blackouts had a “cascading effect,” Newlove said. Without electricity she couldn’t refrigerate the few meager vegetables she could harvest. She stopped breeding and slaughtering animals. She was unable to sell to many of her regular customers, like local “mom and pop shops.” She had to drastically reduce the area she farmed and cut back on planting, and she couldn’t hire seasonal workers.

    The rolling blackouts affecting Newlove’s farm were a result of “load shedding,” scheduled power cuts meant to reduce demand on the grid. ZESCO, the state-owned power company supplying almost all of Zambia’s energy needs, alerted its customers to the load shedding schedule, but these schedules weren’t consistent or reliable, Newlove told ICIJ, making it hard to plan how to maintain — or save — her crops. “One week you’d get a schedule from, say, morning to midday and you’d make a plan based on that,” she said. “Then, without prior notice, it would change.”

    She couldn’t run a farm on four hours of electricity. For the first time since she’d started the farm over a decade earlier — a labor of love she launched while working for a social enterprise — she began to wonder if she’d need to shut it down. “Farmers are optimistic people until that is obliterated entirely by reality. …  It’s a mammoth thing to fathom, that you’re going to kill a business that you’ve worked so hard for for so many years,” she said.
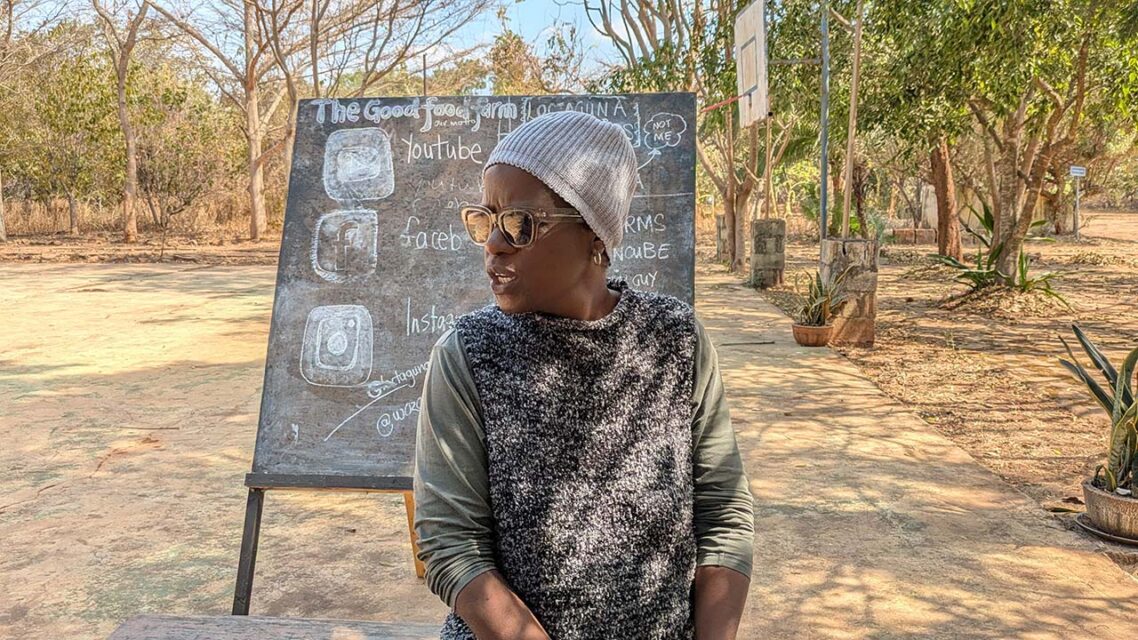
    Photo of a woman sitting in front of a chalkboard in an open field on a farm in Zambia.

    Kanangwa Newlove started farming just outside Lusaka in 2012, selling organic produce to local businesses. Image: Micah Reddy / ICIJ

    Newlove and other small-business owners across Zambia faced collapse amid a perfect storm in which environmental and economic shocks were exacerbated by the country’s deep-seated financial problems. Zambia — where roughly 60% of the population lives in poverty — is overwhelmingly dependent on hydropower, but a severe drought in 2024 left dams empty and forced ZESCO to ration electricity usage. While Zambia is drought-prone, ZESCO’s financial woes left it uniquely ill-prepared for the drought, the worst in decades.

    The company was sinking financially. Among its biggest expenses was a long-term loan of nearly $285 million from the Industrial and Commercial Bank of China (ICBC) with tough repayment terms. The loan was signed more than a decade before, in 2011, and in the following years, ZESCO had taken on more and more debt from ICBC and other Chinese lenders. Beholden to Chinese creditors, the power utility mirrored Zambia, one of the world’s most indebted countries and the first in Africa to default on its sovereign debt during the COVID-19 pandemic. As the country’s largest state-owned company, ZESCO was a significant contributor to Zambia’s overall debt.

    Now, newly revealed documents show how Chinese lenders, working with Chinese contractors in Zambia, piled loans onto the country and its ailing state-owned enterprises. When it came time for ZESCO to pay, ICBC adopted what analysts see as a hardball stance to recover debt from a struggling borrower.

    These documents form part of China Capital, an ICIJ-led investigative collaboration with 23 media partners. Based on a trove of 4.8 million documents, including client dossiers, due diligence reports, loan agreements, meeting minutes and internal emails in English and Chinese, China Capital exposes the inner workings of ICBC’s U.K. subsidiary and London branch, and the crucial role ICBC London has played in advancing Chinese interests in Africa.

    China Capital lays bare what experts describe as the bank’s muscular lending tactics, which burdened some of Africa’s most economically vulnerable states — claims the Chinese Embassy in Zambia denied. The project reveals the complex picture of Zambian debt arrangements and the role played by lenders such as ICBC, which presents itself as a commercial bank but acts as a foreign policy tool of the Chinese state, advancing Chinese strategic interests in resource-rich countries like Zambia.

    Although China became a vital lender for Zambia and helped the country fill an enormous infrastructure gap, Chinese objectives were not always aligned with Zambia’s best interests. Chinese lenders like ICBC were willing to make onerous and high-risk loans to a country that could not afford them. Meanwhile, Chinese companies seeking infrastructure contracts urged Zambian state entities to take on new debt to fund those projects. Zambia’s government, eager for easily accessible credit to fund its infrastructure plans, needed little encouragement. These factors combined to push Zambia into a disastrous debt spiral in which it was unable to service its debt, followed by years of sluggish recovery.
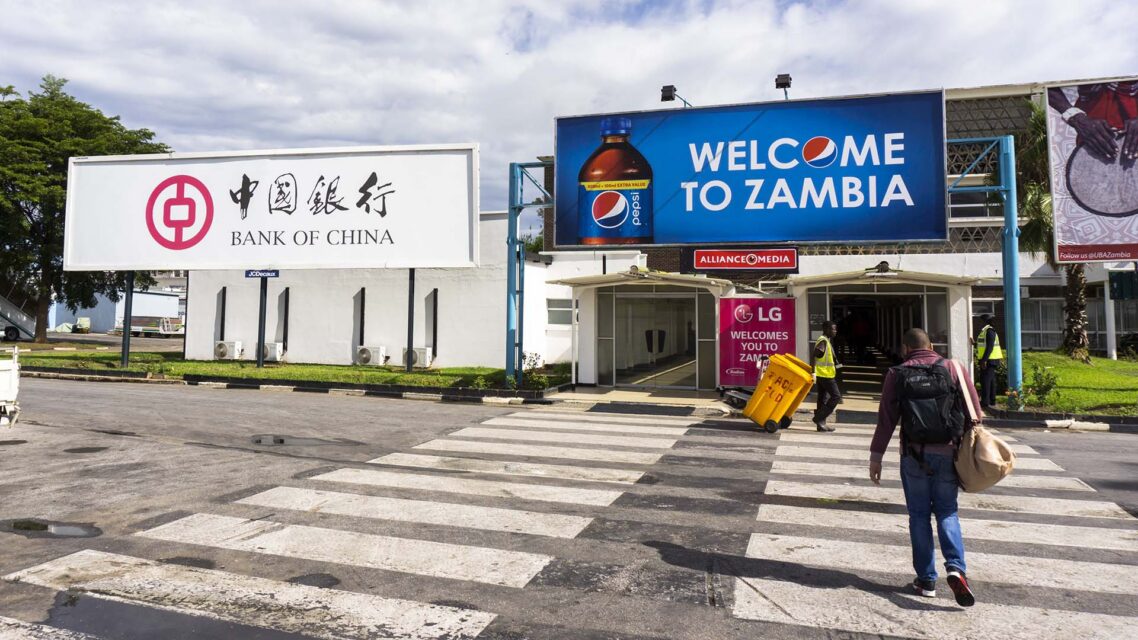
    Photo of a man walking past a sign at the airport in Lusaka that reads Welcome to Zambia beside an advertisement for the Bank of China

    A Bank of China billboard, left, and a PepsiCo Inc. advertisement stand outside the arrivals area at Kenneth Kaunda International Airport in Lusaka, Zambia, on Tuesday, Dec. 11, 2018. Chinese funding was behind many major infrastructure projects, including parts of the airport. Image: Waldo Swiegers/Bloomberg via Getty Images

    A $285 million loan

    Zambia’s economic outlook was positive in 2011, the year ZESCO signed its $285 million loan agreement with ICBC.

    The country had emerged from successful debt relief programs involving the World Bank, the International Monetary Fund and other international lenders years before. Relatively debt-free, it began to focus on funding new infrastructure projects, such as power lines, highways, stadiums and airports. To do so, it turned to the international financial market. Between 2012 and 2015, Zambia issued three international bonds worth $3 billion to foreign investors chasing high yields in the developing world.

    At the same time that Zambia was eagerly courting foreign infrastructure investment, China was rapidly expanding its interests in Africa. In 2013, Chinese President Xi Jinping announced China’s Belt and Road Initiative, a strategy to bolster the country’s connectivity with the rest of the world through infrastructure and development. Chinese companies were encouraged to invest abroad, accompanied by a surge in Chinese foreign lending. To poor, landlocked countries like Zambia, China portrayed itself as an alternative to Western funders, untainted by accusations of paternalism and willing to engage developing nations as equals. It offered fewer economic policy conditions on its loans than its Western counterparts, whose legacies were associated with painful economic reforms forced onto indebted African countries.

    Chinese investors were also willing to go where others were not. For Western companies, Zambia came with a risk premium that drove up the cost of capital and meant that they would invest only if high returns made up for the perceived risk. Barbara Dutzler, an economist with Germany’s main development agency and head of the agency’s Good Financial Governance in Zambia program, told ICIJ that, with China, there was “an alignment between state and industry” and an overarching geostrategic plan. That meant China could direct investment where it wanted and fund projects that would not hold up in purely commercial terms.

    Although it presents itself as a commercial bank, ICBC remains majority state-owned and is driven not only by the profit-maximizing interests of shareholders but also the political prerogatives of the party-state. Documents from China Capital show that ICBC bankers routinely weighed Chinese strategic policies like the Belt and Road Initiative when considering loan decisions around the world.
    Illustration showing ICBC logo, portions of leaked documents, and a Norilsk Nickel sign

    Illustration with photo of Zhang Hongli overlaid with ICBC logo details and images of ICBC bank and boardroom.

    https://www.icij.org/investigations/china-capital/china-banking-icbc-oligarchs-sanctions-london/

    OVERVIEW Chinese banking giant serves firms linked to oligarchs and autocrats to push Beijing’s agenda Sep 14, 2026

    https://www.icij.org/investigations/china-capital/zhang-hongli-icbc-executive-corruption-employee-misconduct/

    CORRUPTION ICBC promoted corrupt executive, ignored employee misconduct as it pursued global expansion Sep 14, 2026

    https://www.icij.org/investigations/china-capital/huawei-icbc-banking-us-court-beijing-london/

    HUAWEI Chinese bank helped Huawei spirit $1B out of London days after US indictment of the tech giant Sep 14, 2026

    Recommended reading OVERVIEW Chinese banking giant serves firms linked to oligarchs and autocrats to push Beijing’s agenda Sep 14, 2026 CORRUPTION ICBC promoted corrupt executive, ignored employee misconduct as it pursued global expansion Sep 14, 2026 HUAWEI Chinese bank helped Huawei spirit $1B out of London days after US indictment of the tech giant Sep 14, 2026

    jiang region specializing in power transmission and renewable energy projects, arranged the financing for a project it was contracted by ZESCO to undertake: construct power transmission lines and infrastructure to supply electricity to Zambia’s Northern Province on the border of the Democratic Republic of Congo and Tanzania, and Eastern Province bordering Malawi and Mozambique.

    This sort of “contractor-facilitated lending” became institutionalized in Zambia, where the government found it convenient to start “outsourcing much of the financing and mobilization process directly to Chinese contractor partnerships,” according to a paper by researcher Tianyi Wu at the Global China Initiative, part of Boston University’s Global Development Policy Center. Besides ICBC, the funds came from an array of Chinese financial institutions that were all too willing to provide high-risk loans. In these transactions, China benefited on both ends — as lender and contractor — while Zambia assumed the repayment obligation and much of the financial risk.

    The former Finance Ministry official told ICIJ the ministry was supposed to oversee borrowing, but “a lot went on outside the Ministry of Finance, and they’d find out that ministry X had signed with Y company from China and organized the finance. It was a bit of a free-for-all for a while.”

    Researchers at CARI found that among African countries with Chinese loans, Zambia had the highest number of lenders and the second-largest number of Chinese contractors securing Chinese-financed infrastructure projects. “Only Angola, which has borrowed four times as much from Chinese lenders, has more contractors, and even Angola has fewer Chinese lenders,” the researchers found.

    Many analysts agree that widespread corruption, patronage and institutional weaknesses helped fuel Zambia’s debt spiral. The country’s bureaucracy lacked capacity to negotiate, evaluate and monitor its high levels of debt, while politicians had perverse incentives to keep accumulating it. The money was easily available for large infrastructure projects from which political elites could derive kickbacks and other illicit gains: “Patronage is part of the political landscape of Zambia,” the former Finance Ministry official said. “People were seeing things like roads being built, a new airport and stadium. Things were getting better in terms of infrastructure but at a very high price because of rent-seeking behavior.”

    Chinese banks loan billions to Zambia

    Sources: The China Africa Research Initiative (CARI) at the School of Advanced International Studies, Johns Hopkins University and the AidData research center at the College of William & Mary. The CARI data includes 2015-2019 loan commitments to ZESCO and 2000-2020 loan commitments to the Zambian central government.

    An IMF report noted both that “large public investment projects were often transformed into vehicles for political patronage and rent seeking opportunities,” and that “embedded governance weaknesses cannot be overestimated in accumulation of sovereign debt and the subsequent crisis.”

    Zambia was an increasingly risky prospect, but ICBC continued expanding its interests there. In 2016 and 2017, ICBC committed to finance three other ZESCO electricity supply projects worth over $100 million and, together with the Export-Import Bank of China (known as China Eximbank), was a joint lender in the $1.5 billion syndicated loan for the 750 megawatt Kafue Gorge Lower Hydropower Station, for which ICBC claimed $15 million in management fees from ZESCO. It also signed six additional loans with the central government between 2016 and 2018, committing over $1 billion to a range of projects, from police and defense force housing to the construction of a hospital and an international airport, not all of which were fully implemented. Borrowing “mushroomed during the [Lungu] administration … to the degree they couldn’t even disburse the loans,” said Dutzler — a view backed by findings of Zambia’s auditor general. This led to growing alarm among Zambian opposition politicians and civil society groups over alleged Chinese predatory lending, as well as international headlines warning of “debt-trap diplomacy” — where a creditor country overloads a borrower with debt with the intention of extracting concessions.

    Meanwhile, Gerald Soko, the butcher, was still trading on Zambia’s good years and focusing on expanding his business, unaware of an approaching debt cliff and the years of economic strain ahead.

    r the $20 million from a reserve account it held on behalf of ZESCO. This caused a stir among ICBC London staffers when they “later learned that [head office] had pushed [the London branch] to make the payment” without the necessary documentation being in place, according to an internal ICBC report in the China Capital documents.

    The reserve account was firmly under ICBC’s control. “What this means is a bank doesn’t have to go to a separate bank, to ask for permission to touch the money in the [debt service reserve account]. They’re like, ‘I am the escrow account bank, I can do whatever the hell I want with this money,’ ” said Bradley Parks, executive director of AidData, a research center at the College of William & Mary that has tracked Chinese lending globally.
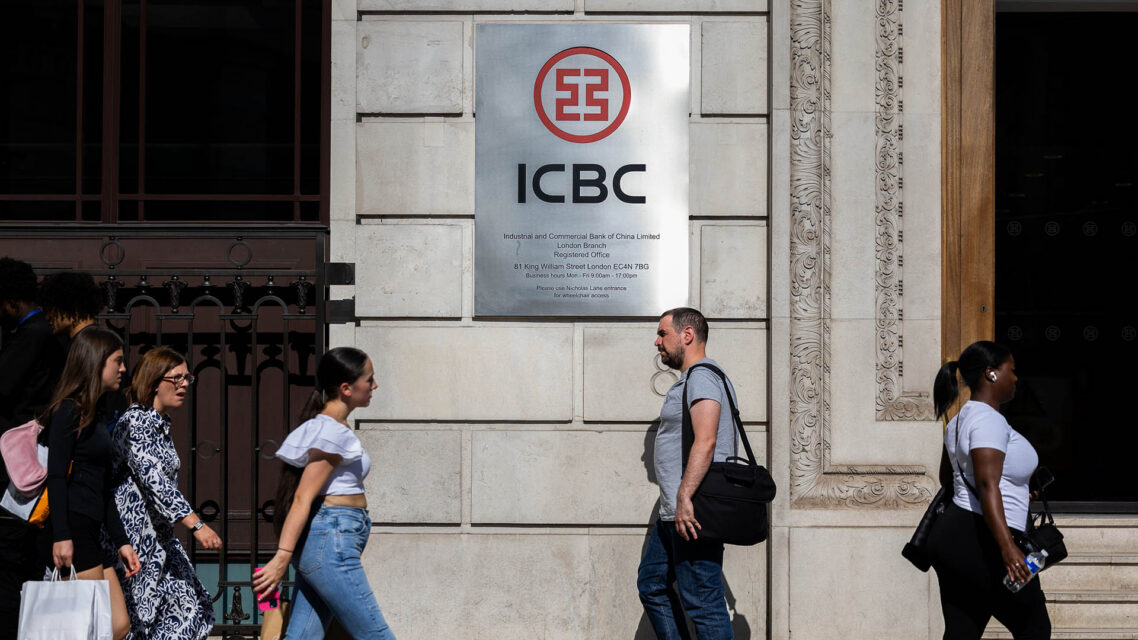
    Photo of people walking past a building with a sign that reads ICBC

    ICBC’s London branch was pressured to transfer $20 million from a ZESCO reserve account without securing the proper paperwork first, according to confidential bank records. Image: May James/SOPA Images/LightRocket via Getty Images

    Later that year, S&P Global again downgraded Zambia “on rising fiscal deficits and debt burden.” In its analysis, it referred to mounting government arrears “to contractors involved in the construction of new roads and to ZESCO … which had to import emergency power to replace a shortfall of hydro-generated power.” It added that “the increase in debt accumulation has also been accompanied by rising debt service payments.” Between 2014 and 2019 the government’s debt to foreign creditors as a percentage of GDP more than quadrupled.

    The effects of a severely strained economy soon reached ordinary Zambians. Zambia’s currency, the kwacha, depreciated, inflation rose and high interest rates made borrowing more expensive. “This has affected the ordinary person, this high inflation without GDP growth that can match the cost of living,” said Hambayi, the Zambian financial analyst.

    By 2019, ICBC was “reportedly reluctant” to release funds because Zambia began defaulting on payments to other creditors, according to an AidData analysis. In 2020, a ZESCO subsidiary defaulted on its repayment obligations for the $1.5 billion China Eximbank-ICBC hydropower loan. ZESCO — which had guaranteed higher electricity prices from independent power producers than the tariffs it charged its customers — was insolvent. So was the country, after defaulting on its debt that year. Lungu’s government had run out of options and had begun talks to restructure its debt.

    Among other measures to recover costs and reduce losses, the government began cutting subsidies, including for fuel, and increasing electricity tariffs. The escalating cost of living weighed heavily on Soko’s butchery business. “People complain about the cost of electricity … and are struggling to make ends meet. They keep asking for meat on credit, the same people who used to spend a lot,” he said, before listing the many neighboring businesses that had closed in recent years: barbers and salons, welders and fast-food franchises.

    Zambia’s weakened fiscal position left it extremely vulnerable to the worst drought in four decades, which began in 2023 and led to the relentless power cuts that nearly ended Newlove’s farming business. During the most intense period of cuts, as her crops wilted, she and the farm supervisor scrambled to find a generator and eventually found someone willing to rent them an old one. It sputtered and shook and looked as if it would give out, but it got her through those difficult days. The generator’s high costs ate into her dwindling margins, though, forcing Newlove to use her personal savings to keep the business afloat. “If we didn’t have that reserve of money, we would have sunk,” she told ICIJ.
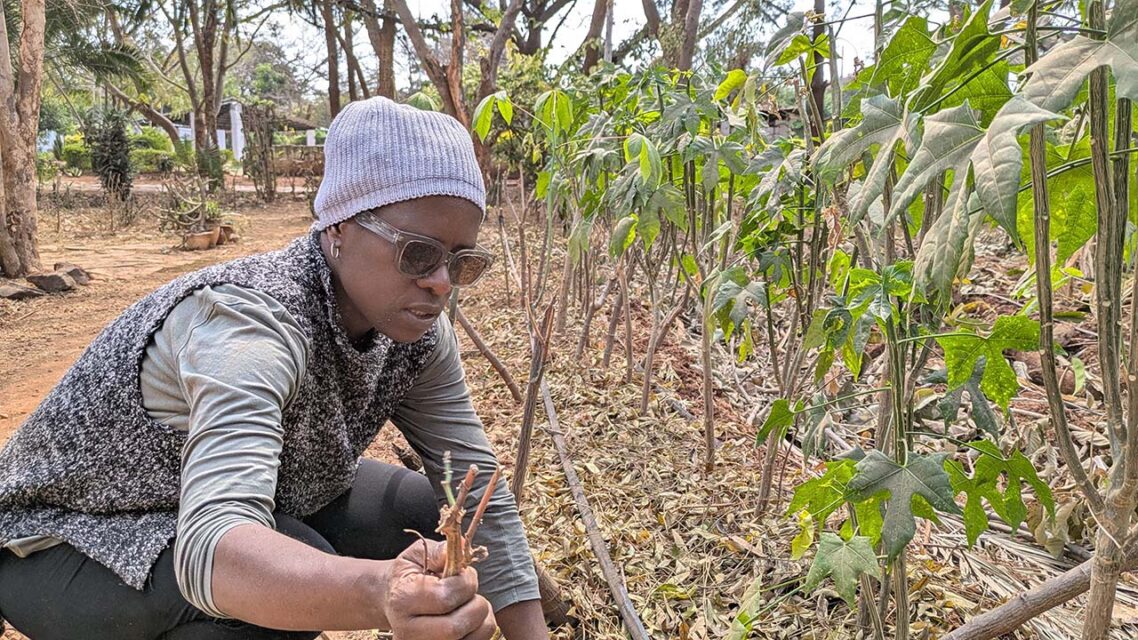
    Photo of a woman farming.

    A crippling drought that began in 2023 wilted crops and led to rolling electricity outages, which made it difficult for Newlove to run pumps for irrigation and pushed her business to the brink of collapse. Image: Micah Reddy / ICIJ

    The electricity crisis also dealt a heavy blow to Soko’s butchery, leaving fridgefuls of rotting meat. Customers stopped buying in bulk, worried that they would face the same problem, what Soko called the “trickle-down effects” of load shedding. He said that burglars twice took advantage of the darkness during power cuts to target his shop. To get through the worst of the outages, Soko too had to fork out for a generator he could barely afford to run. Sales from the butchery these days is less than half of what it was before load shedding, and he has had to put all his plans for expanding his business on hold. “There is no profit,” he told ICIJ.

    Negotiating the future

    After China became the world’s largest source of bilateral official lending to developing countries, it faced a critical test in Zambia: How would it negotiate to restructure an unusually complex mountain of debt? How would it work with other external creditors? As a creditor nation, China has not joined the Paris Club — an informal group of mostly high-income lending countries that coordinates solutions to heavily indebted developing countries — and Chinese creditor loan agreements often contain provisions to exclude them from collective debt-restructuring initiatives. Chinese lenders also had a reputation for taking a hard line and refusing to accept markdowns on their loans, “a core Chinese position,” said Dutzler of Good Financial Governance in Zambia. “They don’t give a haircut.” Among those at the negotiation table, she said, “China was the big unknown.”

    The restructuring efforts began on shaky ground, as the negotiating parties — numerous governments and private lenders — went through back-and-forth talks that dragged on for years, hamstringing Zambia’s development and economic recovery.

    The true scale of the country’s debt remained hidden, adding to the tension. Researchers at CARI, which had been tracking Chinese lending to Africa for almost a decade, found that “Zambia’s outstanding external debt to all Chinese financiers, official and commercial, was approximately $6.6 billion in August 2021.” This was nearly double the highest figure cited by the Zambian government. Part of the problem stemmed from the structure of the Chinese loans, which were cloaked in confidentiality clauses.

    debt restructuring.” At the time, holders of Zambia’s bonds were “refusing to proceed with debt renegotiation, citing insufficient information about China’s claims on the country.”

    In an email to ICIJ, the Chinese Embassy in Zambia said that claims about opaque lending were “baseless” and that China’s “overseas financing cooperation is fully open and transparent.”

    Ultimately, the worst fears of Chinese predatory lending, rumors of China seizing national assets like ZESCO and screaming international headlines about debt-trap diplomacy turned out to be alarmist. China agreed to co-chair Zambia’s official creditors’ committee alongside France, signaling a willingness to work with others rather than go it alone. An important milestone came in 2024, when Zambia reached agreements in principle to restructure debt with Chinese commercial lenders, including ICBC. As of 2026, debt-restructuring negotiations were largely concluded, with most of the talks occurring under the government of Lungu’s rival and successor, Hakainde Hichilema.

    Ordinary Zambians still feel the lingering effects of years of intersecting crises that battered the economy and shifted perceptions of China’s role in Zambia. At Soko’s spartan butchery, the long queues of customers have been reduced to a trickle. Turnover is less than half of what it was, he said, leaning against a mostly empty display cabinet. Survey data shows that Zambians have grown increasingly skeptical of China’s role in their country. In 2014, 72% of those polled by Afrobarometer — an independent public opinion research network — viewed China’s economic and political influence positively. By 2022, that figure was down to 42%. China too was burnt by the debt troubles of developing nations; that’s part of the reason it has shifted focus to what it calls a “small and beautiful” approach to infrastructure projects, with smaller loans and shorter repayment windows.
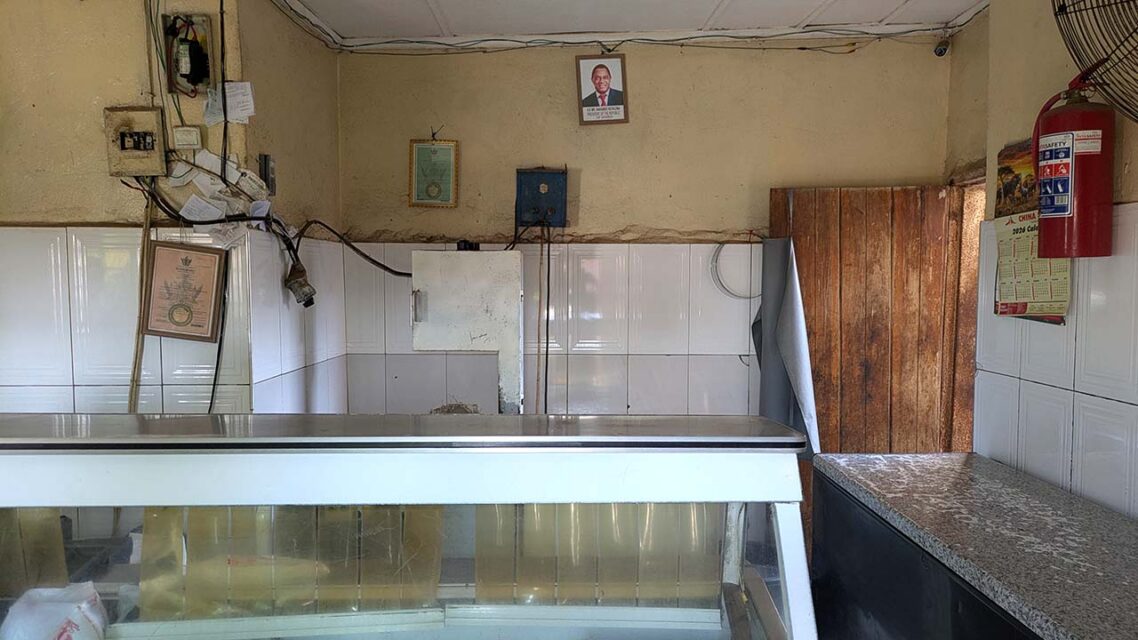
    Photo of an empty butcher shop, with a picture of Zambian president Hichilema hanging on the wall.

    A photo of Zambian President Hakainde Hichilema hangs on the wall of Soko’s butcher shop, which was a thriving business until the country’s electricity crisis hit and the economy stalled. Image: Micah Reddy / ICIJ

    Newlove, the farmer, told ICIJ that she feels she has made it out of the crisis intact. Her farm is fully operational, and she avoided laying off any of her 14 full-time staff. They have begun replanting on portions of the land they were forced to abandon. The chickens, goats, rabbits and pigs survived, and she has since crisis-proofed her farm with large solar panels that soak up energy from Zambia’s mostly sunny skies. But on the other side of Newlove’s stone perimeter wall is dry, dusty scrubland — a graveyard for failed farms and a constant reminder of her close brush with disaster. “Our resilience was tested,” she said. “I knew a lot of farmers who shut down or changed business. … They were very lucrative, and I thought, ‘We’re next.’ ”

    Contributing reporters: Scilla Alecci, Denise Ajiri, Jelena Cosic and Delphine Reuter (ICIJ)

    Source: ICIJ · 2026-10-26
  • ISC Stormcast For Monday, October 26th, 2026 https://isc.sans.edu/podcastdetail/10150, (Mon, Oct 26th)

    ISC Stormcast For Monday, October 26th, 2026 https://isc.sans.edu/podcastdetail/10150, (Mon, Oct 26th)

    Source: SANS Internet Storm Center · 2026-10-26

  • Space Modernization for the 21st Century

    In this document, the Federal Communications Commission (Commission or we) adopts a Further Notice of Proposed Rulemaking (FNPRM) that seeks comment on and/or proposes additional reforms.

    • Agencies: Federal Communications Commission
    • Document type: Proposed Rule
    • Document number: 2026-21818

    Source: Federal Register — Cybersecurity · 2026-10-26

    Documents

  • CVE-2026-109619: PHP Stale Internal Request-State Vulnerability

    PHP contains a stale internal request-state vulnerability that allows for unauthenticated remote code execution.

    • Vendor / product: PHP Group PHP
    • Required action: Apply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset’s internet exposure and ensuring adherence to BOD 26-04 patching guidelines.
    • Federal due date: 2026-10-29
    • Known ransomware campaign use: Unknown
    • CWE: CWE-416, CWE-755, CWE-824, CWE-1325, CWE-1419

    This vulnerability affects an open-source component, third-party library, protocol, or proprietary implementation that could be used by different products. For more information, please see: https://www.php.net/ ; https://www.cisa.gov/news-events/alerts/2026/10/21/critical-vulnerabilities-php-require-immediate-patching ; BOD 26-04: https://www.cisa.gov/news-events/directives/bod-26-04-prioritizing-security-updates-based-risk ; Forensics Triage Requirements: https://www.cisa.gov/news-events/directives/bod-26-04-implementation-guidance-prioritizing-security-updates-based-risk ; https://nvd.nist.gov/vuln/detail/CVE-2026-109619

    Source: CISA Known Exploited Vulnerabilities · 2026-10-26

  • CVE-2026-109618: PHP Memory Corruption Vulnerability

    PHP contains an out-of-memory corruption vulnerability that allows for unauthenticated remote code execution.

    • Vendor / product: PHP Group PHP
    • Required action: Apply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset’s internet exposure and ensuring adherence to BOD 26-04 patching guidelines.
    • Federal due date: 2026-10-29
    • Known ransomware campaign use: Unknown
    • CWE: CWE-416, CWE-755, CWE-824, CWE-1325, CWE-1419

    This vulnerability affects an open-source component, third-party library, protocol, or proprietary implementation that could be used by different products. For more information, please see: https://www.php.net/ ; https://www.cisa.gov/news-events/alerts/2026/10/21/critical-vulnerabilities-php-require-immediate-patching ; BOD 26-04: https://www.cisa.gov/news-events/directives/bod-26-04-prioritizing-security-updates-based-risk ; Forensics Triage Requirements: https://www.cisa.gov/news-events/directives/bod-26-04-implementation-guidance-prioritizing-security-updates-based-risk ; https://nvd.nist.gov/vuln/detail/CVE-2026-109618

    Source: CISA Known Exploited Vulnerabilities · 2026-10-26