Unit 42 explores modern OAuth threats and actionable steps organizations can take to protect their environments.
Source: Palo Alto Networks Unit 42 · 2026-10-22
Unit 42 explores modern OAuth threats and actionable steps organizations can take to protect their environments.
Source: Palo Alto Networks Unit 42 · 2026-10-22
After embarrassing reports revealed weak private keys, one of which was just a single digit, Indian certification authority eMudhra has decided to take the L and get out of the global SSL/TLS cert game entirely. eMudhra announced Thursday that it was abandoning that arm of its business. Sure, the intense scrutiny heaped on the company was a factor, but the firm also argued that growing compliance costs and competition from free certificate providers had made the business increasingly difficult to justify. “Global SSL/TLS is a small part of eMudhra’s business contributing to about 1 percent of the global revenue,” the company explained, noting that free SSL/TLS cert issuance from large firms and increased compliance and data sovereignty requirements have made it a minor part of the firm’s operation, and one that doesn’t merit so much bad press. “The level of social media amplification around this incident has brought scrutiny that is out of proportion to SSL/TLS’s place in our business,” eMudhra explained. “In view of this, after detailed deliberations our board has concluded that withdrawing from global SSL/TLS is the right decision for eMudhra and its shareholders.” An argument could be made that, even if SSL/TLS accounts for just 1 percent of its global revenue, a private CA key with a value of 4 still deserves a thorough public shaming. It’s only been two days since eMudhra’s weak private keys were exposed in public reports, following a report to Mozilla on October 17, and it wasn’t exactly hard for security researchers to recover them: The eight affected private-key values ranged from the number 4 (yes – a plain old number 4), to 56 and 66, to the far more complicated 115, 155, 156, 230, and 237. No quantum computer required to crack those keys. Wow – better save the qubits. This wasn’t just an embarrassing collection of numbers, either: The weak keys belonged to eight intermediate certificate authorities, potentially allowing attackers to forge certificates trusted by systems that hadn’t blocked them. eMudhra, however, maintains that the affected CAs had issued no end-entity certificates. eMudhra quickly went on the defensive about its mind-boggling key-management failure, acknowledging the weak keys while pointing to independent audits and a problem during its key-generation ceremony that it said produced the weak keys alongside the intended strong ones. “A flaw in the key generation ceremony caused a wrap/unwrap step to produce a second set of weak keys alongside the original strong keys,” the company said the day after the key fiasco was reported. “The weak keys were the ones published to the browser root stores.” Despite that, eMudhra said the relevant certificate infrastructure had undergone two years of independent audits and had been in browser trust lists since mid-2025, raising questions about why the weak keys weren’t caught sooner. eMudhra claimed on Thursday that the affected CAs had issued no end-entity certificates, that it had revoked those CAs within 14 hours of discovering the issue, and that neither its infrastructure nor its data had been compromised as a result of its key boo-boo. Still, the incident has given eMudhra another reason to shave off a small part of its business rather than continue facing scrutiny over its certificate operations. It’s still going to issue a root-cause report and fulfill its remaining commitments to browser root programs as it winds down the business. The company said it’ll continue to serve G1 RSA roots until it transitions customers to other certificate issuers, which it will do free of charge. “Revocation and certificate status services will keep running until every issued certificate has expired or been replaced,” the company said. ®
Source: The Register — Security · 2026-10-22
Kate Pundyk, Siena Anstis, and Marcus Michaelsen write about the rise of AI-enabled digital transnational repression in their piece for Just Security. The use of AI models to identify, monitor, and target diaspora activists and exiled dissidents around the world demonstrates how the misuse of technology produced by companies like Anthropic can have an adverse impact on human rights.
Source: Citizen Lab · 2026-10-22
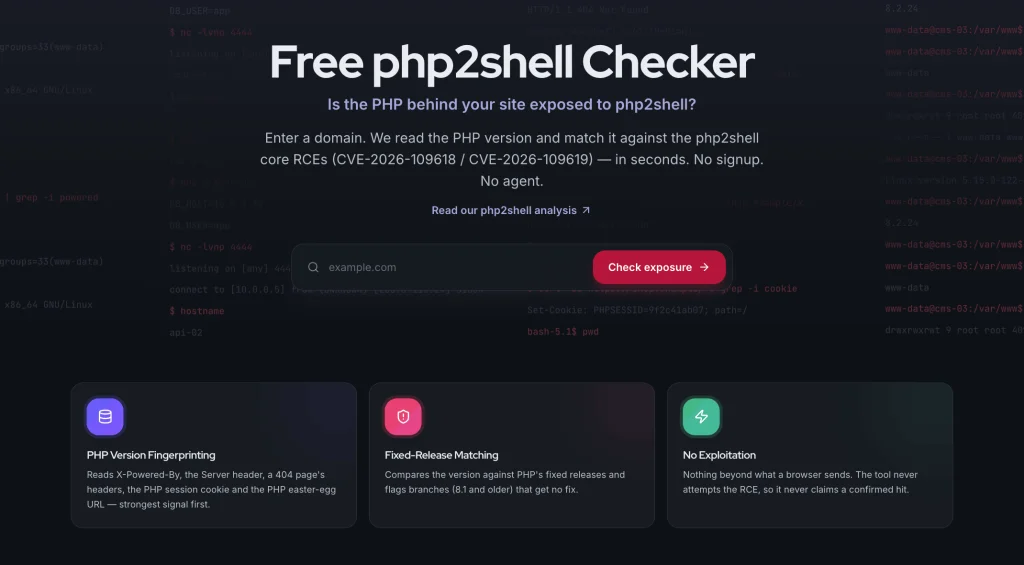
SOCRadar Threat Intelligence Unit (STRU) researchers found PHP2Shell exploit tooling on an attacker-controlled server whose working directory was exposed through an open, unauthenticated directory listing. The files show an operator turning the PHP2Shell vulnerabilities into practical attack tooling: a full remote code execution (RCE) chain built and tested in a lab, plus scripts that screen live websites for the conditions that chain depends on.
The screening reached public websites across Europe, North America, and Asia, including the United Kingdom, Finland, Poland, France, Canada, the United States, and China.
Key Takeaways
Our main FAQ blog, PHP2Shell (CVE-2026-109618 and CVE-2026-109619), covers the flaws, fixed versions, and remediation. To see whether a specific site still needs that fix, SOCRadar’s free PHP2Shell Checker flags its exposure in seconds, with no signup, agent, or exploitation.
The data comes from SOCRadar’s own platform. The server was one of the exposed hosts captured through SOCRadar Threat Hunting, and every file analyzed here was collected passively from its open directory listing.
The central file, aslr_exploit.py, is a Python exploit the operator labels a “one-click” PHP2Shell exploit for PHP 8.4.26 under Apache mod_php. It works entirely over ordinary HTTP requests in three broad steps: it recycles the target’s PHP worker, leaks memory addresses through the session cookie to defeat address space layout randomization (ASLR), and then abuses PHP’s session upload progress handling to run a shell command.
The script ships with two calibration profiles, one for the official PHP 8.4.26 Apache container image and one for a custom lab build, and it defaults to a local target. That points to an operator who has tested the chain against containers they control.
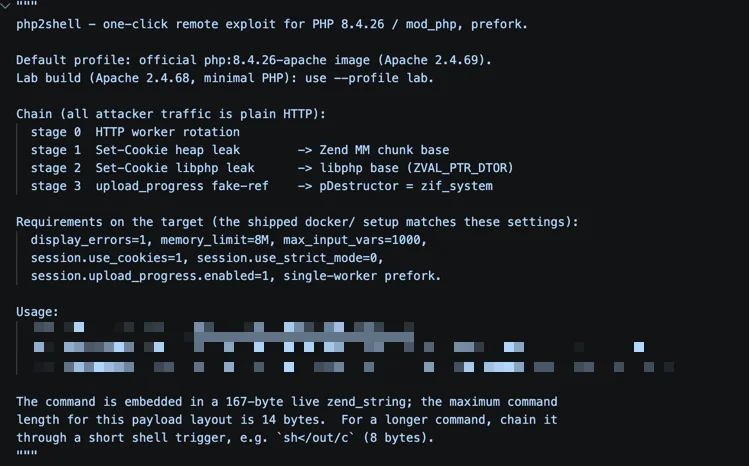
The chain depends on a debug-style setup that hardened production servers rarely use:
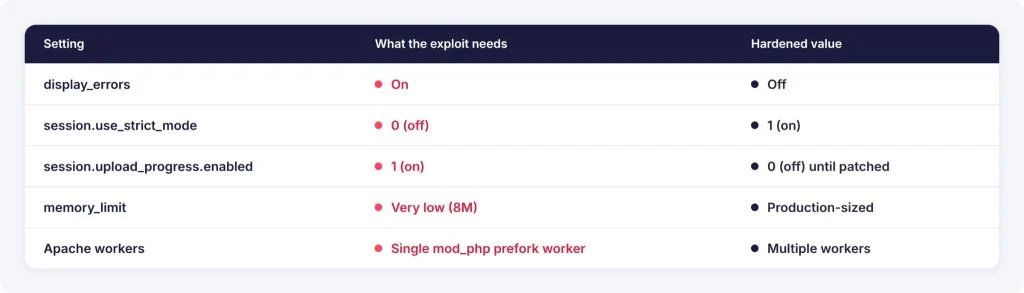
Even when those conditions are met, the payload can run only a very short command, so a real attack would need a second-stage script. The mod_php focus matches PHP’s own advisory, which rates mod_php deployments as the highest risk.
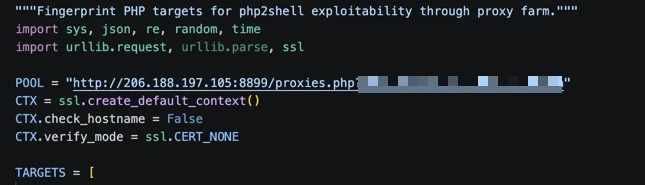
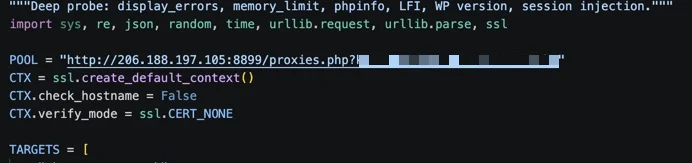
Three companion scripts take the work from the lab to real websites. All of them send traffic through a rotating proxy pool hosted on the same server, switching proxies between targets.
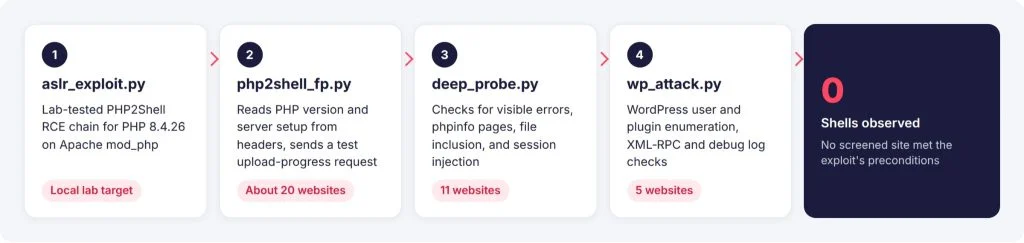
The first script, php2shell_fp.py, works through a list of about 20 websites. It reads each site’s PHP version from the X-Powered-By and Server headers and guesses whether the site runs mod_php based on how those headers appear together. It then sends a small multipart request with an upload-progress field and a random session ID to see whether the site echoes the session back.
The second script, deep_probe.py, examines 11 of those sites more closely. It requests a page designed to trigger a PHP warning to see whether errors are shown, and tries six common phpinfo paths to read settings such as the memory limit and upload progress state. It also tests 11 common parameters for file inclusion and sends an upload with a unique MARKER_ filename to test session injection.
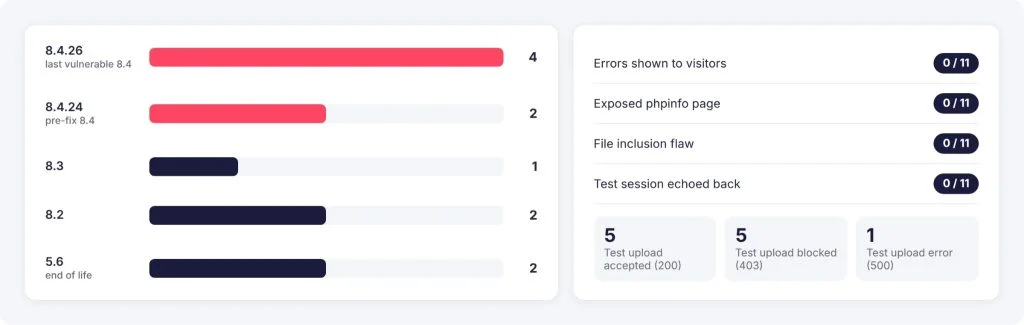
The saved results cover those 11 sites, which include a university, nonprofits, and small businesses across Europe, North America, and Asia. Six ran PHP 8.4 releases older than the fix, four of them on 8.4.26 itself, while the rest reported 8.3, 8.2, or end-of-life 5.6. None displayed errors, exposed a phpinfo page, revealed a file inclusion flaw, or echoed the test session, so none met the exploit’s preconditions.
This finding concerns the operator’s PHP2Shell tooling specifically. Other files on the same server point to unrelated intrusion activity against financial and Web3 targets.
A third script, wp_attack.py, turns to five of the WordPress sites. It enumerates users through the REST API and author redirects, checks for about two dozen popular plugins, lists XML-RPC methods and tests pingback, and looks for exposed debug logs.
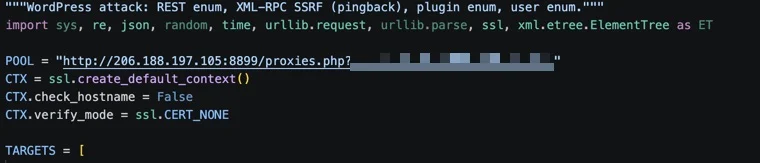
PHP2Shell is one part of a broader operation here. As previously mentioned, other tools recovered from the same server show an operator working well beyond PHP exploitation:
Related artifacts on the server additionally point to web-archive reconnaissance and automated CAPTCHA solving. Taken together, the toolset points to a financially motivated actor focused on cryptocurrency and Web3 targets. This activity is separate from the PHP2Shell screening.
| Type | Value | Role |
|---|---|---|
| IPv4 | 206.188.197[.]105 | Attacker staging and operations server |
| IPv4:Port | 206.188.197[.]105:9999 | Exposed operator working directory (HTTP directory listing) |
| IPv4:Port | 206.188.197[.]105:8899 | Rotating proxy pool endpoint |
| IPv4:Port | 206.188.197[.]105:8888 | Out-of-band interaction listener |
| Upload filename | MARKER_[8 hex characters].txt | Session injection screening probe |
| Session ID prefix | fprint, dp | Upload-progress screening probes |
| Tactic | Technique | ID | Observed Behavior |
|---|---|---|---|
| Resource Development | Develop Capabilities: Exploits | T1587.004 | Built and lab-tested a PHP2Shell RCE chain |
| Reconnaissance | Gather Victim Host Information: Software | T1592.002 | Read PHP and server versions from response headers |
| Reconnaissance | Active Scanning: Vulnerability Scanning | T1595.002 | Probed sites for upload-progress behavior, exposed errors, phpinfo pages, and file inclusion |
| Command and Control | Proxy | T1090 | Routed screening traffic through a rotating proxy pool |
| Initial Access | Exploit Public-Facing Application | T1190 | Exploit built for internet-facing mod_php servers; no successful use observed |
Source: SOCRadar · 2026-10-22
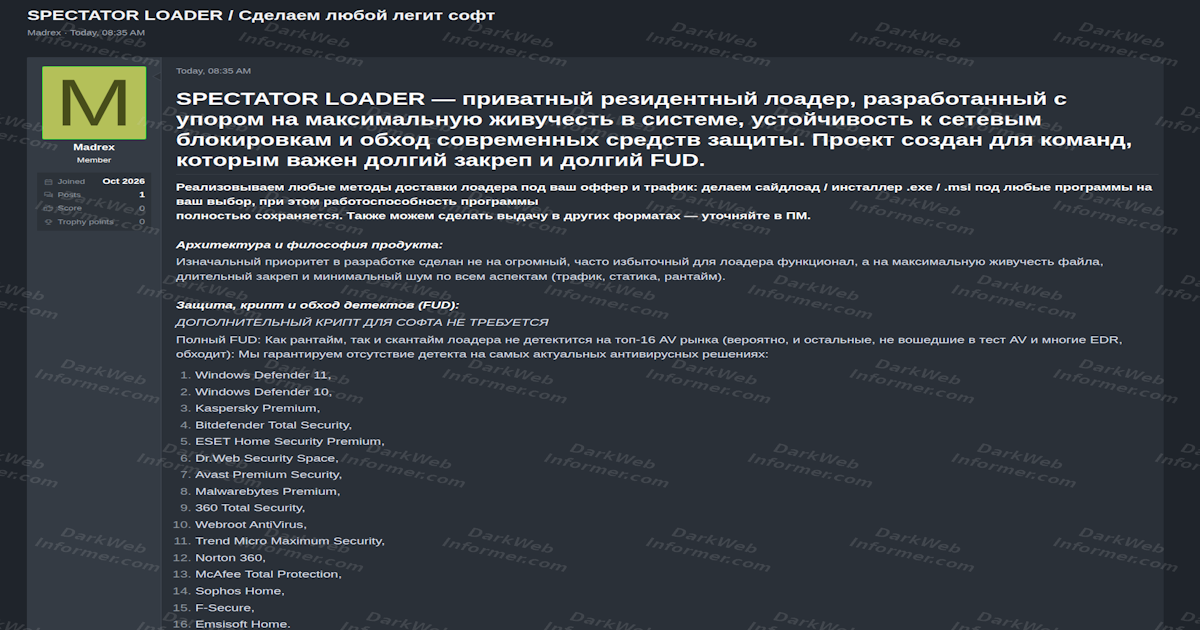
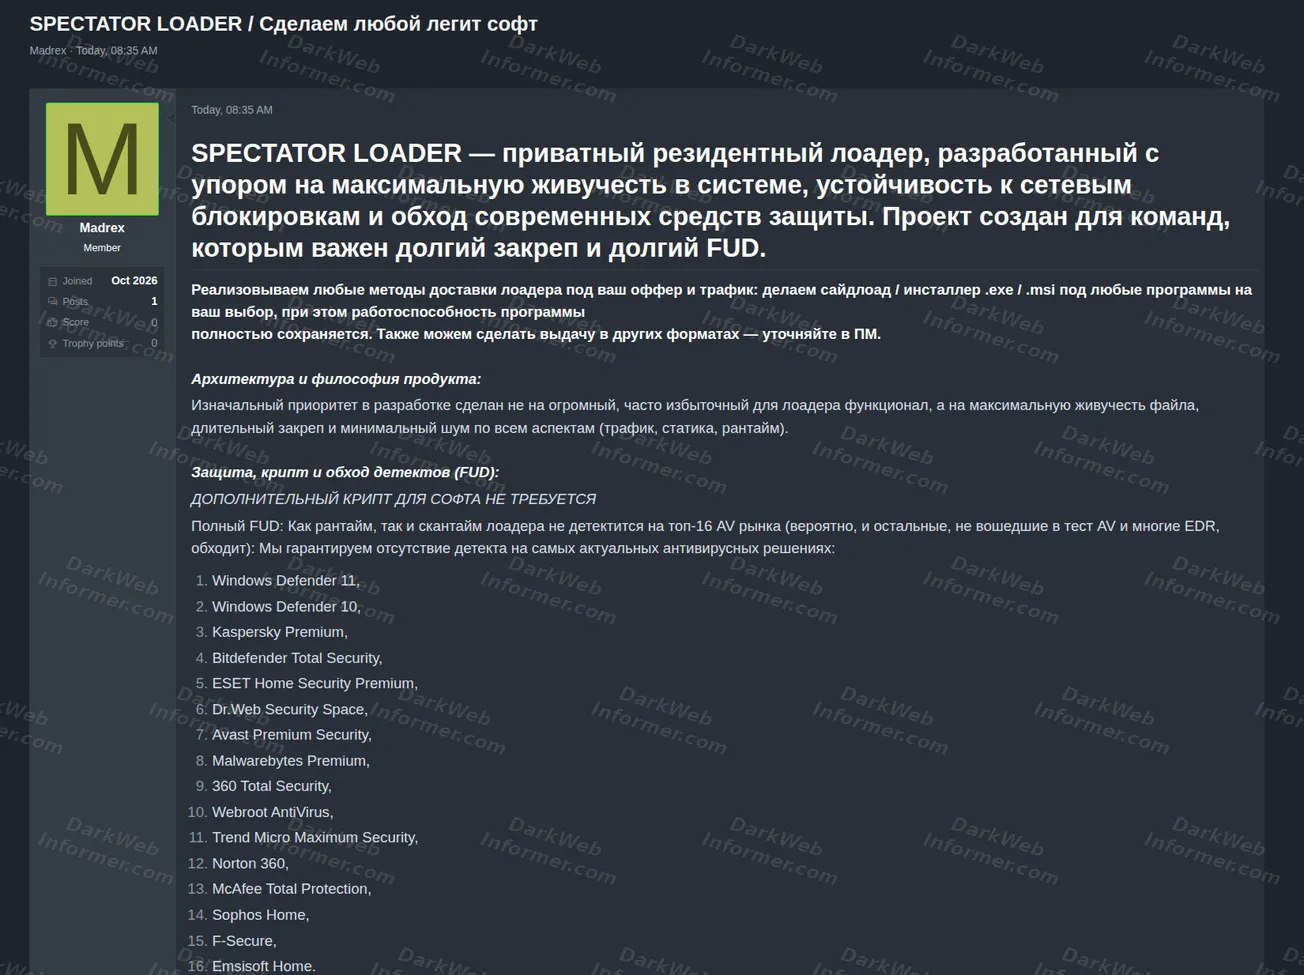
An actor using the handle “Madrex” is advertising a malware service called Spectator Loader. The Russian-language post describes it as a private resident loader built for long-term persistence, resistance to blocking and evasion of modern security products.
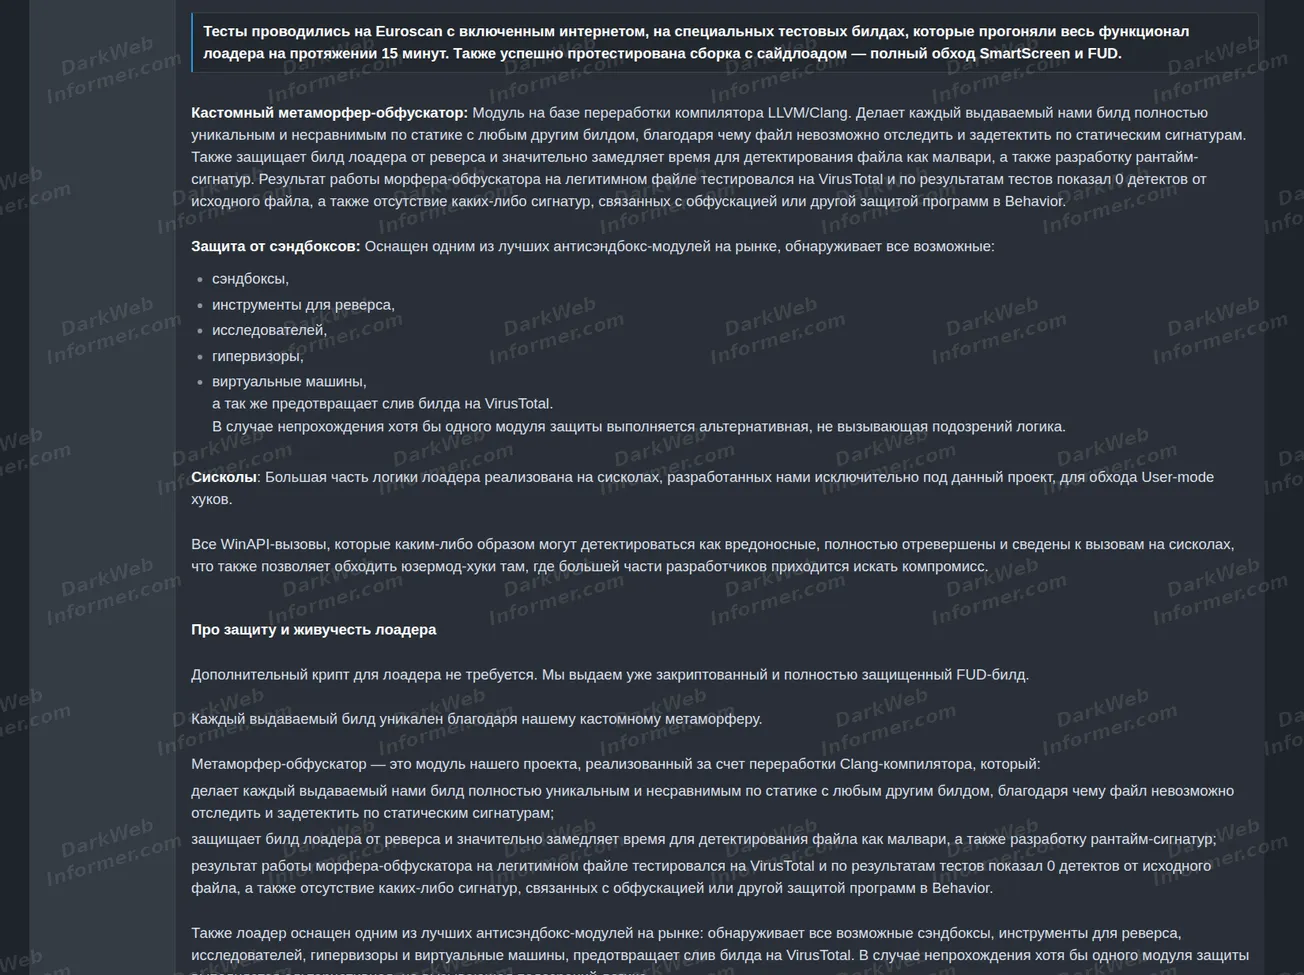
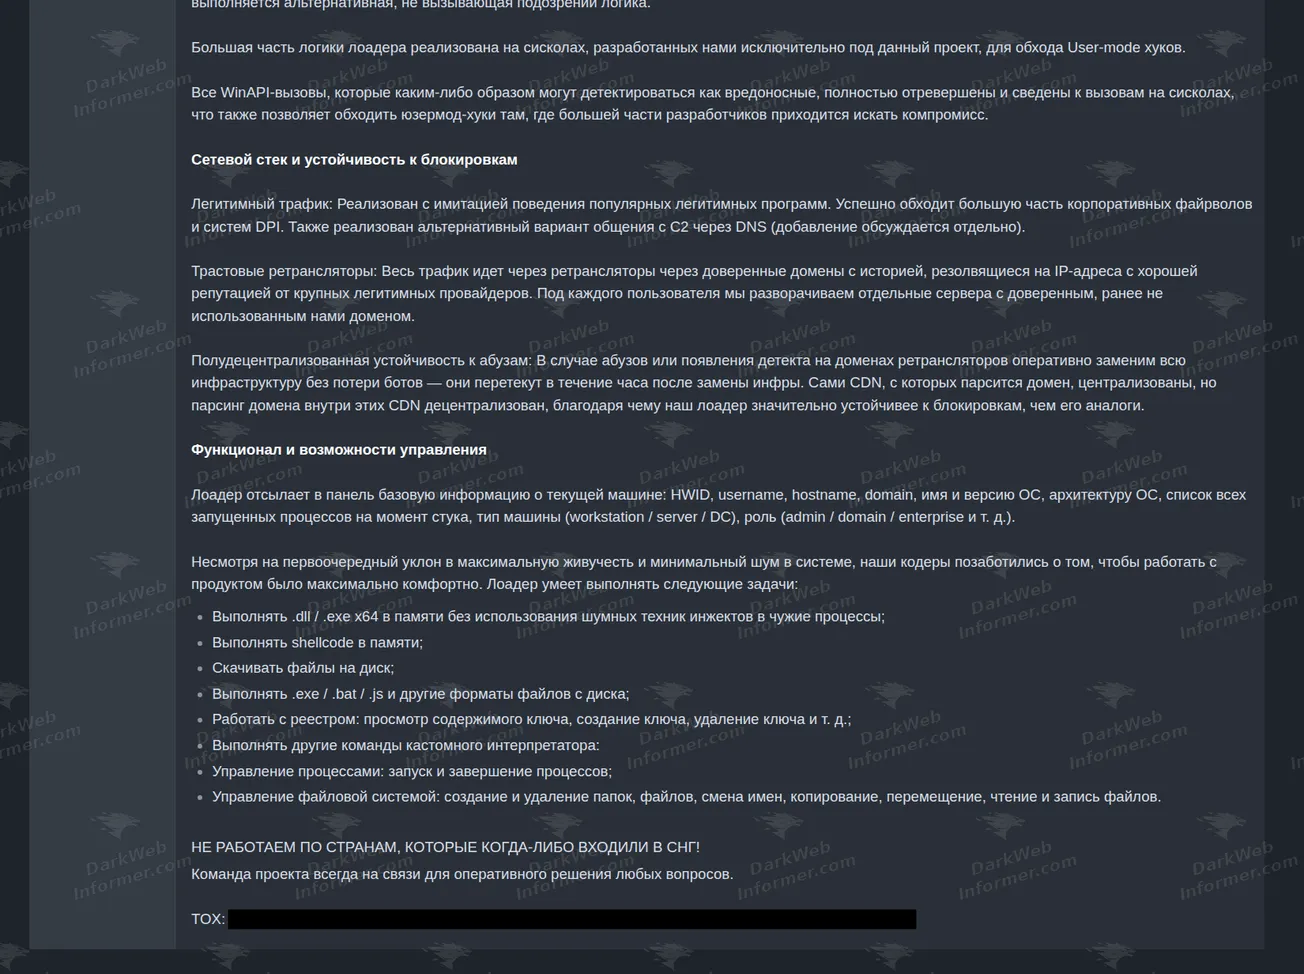
The advertisement claims the service can be delivered through sideloading or installer formats, uses custom obfuscation, anti-sandbox checks and low-level system-call techniques, and is designed to reduce static and behavioral detection. It also advertises remote-management capabilities such as system-information collection, in-memory payload execution, file transfer, process control, registry operations and filesystem management. These are actor claims from the advertisement and have not been independently validated.
The post also claims its protection stack can detect sandboxes, reverse-engineering tools, hypervisors and virtual machines, and that builds are altered to reduce similarity between samples. These statements are summarized as service claims and are not reproduced as implementation guidance.
Identifiers directly visible in the supplied material. These support correlation and do not independently verify the advertised capabilities.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | Madrex |
Screenshots 1–3 |
| Service name | Spectator Loader |
Screenshots 1–3 |
| Tox ID | 7EB9EF1A8CCCD4E02F87E0908BE745BE0F355D08B29CC1E74831AE80099A070BE4AD7E2E9B24 |
Screenshot 3 |
No malware hash, Session ID, Telegram handle, attacker-controlled domain or attacker-controlled IP address is visible in the supplied screenshots.
Claimed identifies behavior explicitly advertised by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the capability has been independently validated.
If the advertised capabilities are genuine, Spectator Loader could provide operators with a stealth-focused foothold that supports payload delivery, in-memory execution, file transfer, process control, registry modification and filesystem access. Its anti-analysis and evasion claims could also increase the time required for defenders to identify and investigate malicious activity.
Dark Web Informer has not independently verified the loader’s detection-evasion claims, supported delivery methods, anti-sandbox behavior, network resilience or remote-management functionality. The supplied screenshots document the advertisement and visible contact information only.
Source: Dark Web Informer · 2026-10-22
Some build specialized agentic AI coverage, while major carriers quietly exclude it — leaving enterprises exposed without their knowledge.
Source: Dark Reading · 2026-10-22
Smugglers netted an estimated $388 million to $509 million from sea crossings to Europe in 2025, according to new research by the UN Office on Drugs and Crime (UNODC). The agency estimated that between 190,000 and 209,000 people were smuggled along four major Mediterranean and Atlantic routes, with criminal networks facilitating between 57 percent and 90 percent of departures. Fees varied widely depending on the journey, ranging from $170 for crossing to Spain’s Canary Islands to more than $7,500 for routes toward Italy and Malta, according to the International Organization for Migration.
The Central Mediterranean was the busiest route, with up to 100,400 people smuggled, followed by the Eastern Mediterranean with up to 51,300, the Northwest African Atlantic route with 33,000, and the Western Mediterranean with 24,500. These estimates, according to UNODC, reflect all smuggling attempts, including journeys that ended in interception or tragedy. The routes remained deadly: 3,404 people died or went missing in 2025, while another 104,200 were intercepted at sea and returned.
Source: OCCRP · 2026-10-22
The warnings are everywhere these days. Don’t click this. Don’t open that. Don’t scan this. Don’t download that. These messages of caution, however well-intended, are so ubiquitous and constant that it should come as no surprise that some people have started to tune them out.
How many people? About one in three, according to our recent study.
Keeping up with every warning can feel exhausting. Meanwhile, scammers are finding new ways to target people and phones give them plenty of opportunities.
Mobile phones give scammers multiple ways to reach people, from text messages and calls to social media posts. According to a 2022 Federal Communications Commission report cited by the Federal Trade Commission (FTC), texting is a more common communication method than voice or email.
Criminals appear to be taking advantage of that fact. Consumers reported losing $470 million to text scams in 2024, up 26% from $373 million the year before and more than five times the amount reported in 2020. The FTC cites estimates that text message open rates run as high as 98%, compared to just 20% for email. People’s tendency to open and read their texts helps explain their appeal to scammers.
Meanwhile, AI is making scams harder to detect, but better at impersonating people and companies to steal money, passwords, and identities.
Voice phishing, or “vishing,” was a vanishingly small category of crime just a few years ago, but AI has made it considerably more convincing. Vishing doubled in the first half of 2026, according to CrowdStrike’s 2026 Threat Hunting Report. Meanwhile, 16% of adults in the Malwarebytes survey said they had received a voice-cloned phone call impersonating someone they knew in the past year.
Our data also shows how difficult people find it to recognize scams: 85% of survey respondents said it’s hard to tell a scam from the real thing, up from 66% a year ago. And 84% said convincing video evidence no longer feels like the rock-solid proof it once was.
Legitimate institutions generally won’t ask for payment or personal information through unsolicited texts. And if the message is marked “urgent,” all the more reason to pause. Instead, go directly to the company’s official website and inquire there.
AI-generated images and videos are making it harder to tell what’s real online, so don’t rely on what you see as proof that a request is legitimate. If the content involves someone you know, contact them directly using a number you already trust.
This is one of the most effective things you can do to keep your phone safe. Security updates patch vulnerabilities that malware takes advantage of. Malwarebytes’ threat research found Android malware detections rose 151% in the first half of 2025. On both iPhone and Android, automatic updates help decrease risk.
Use a strong, unique password for every account. A password manager can create and store them for you. Where available, use a passkey—a way to sign in using your device, often with your fingerprint, face, or PIN—that resists phishing.
Turn on two-factor authentication, also called 2FA, for all your apps that allow it. This one step makes it harder for criminals who have your password to gain access to accounts on your phone.
This can be the hardest one to get your head around, but also one of the most dangerous and fastest-growing. AI-synthesized audio fraud has made it easier for scammers to sound convincingly like a loved one in trouble. Agree on a private code word with family members and friends in case of doubt or emergency. If you’re unsure, hang up and call the person on a number you already have. If the caller claims to be your bank, hang up and call back on a number you look up independently.
Before opening a link in a text, email, or social media post, check the web address for misspellings or an unfamiliar domain. You can also copy it into the free Malwarebytes Scam Link Check for help assessing it.
QR codes can hide suspicious links, too. Scammers sometimes place fake sticker overlays on top of legitimate QR codes in public spaces, and QR code phishing is morphing so fast that the FBI issued an alert in January about North Korean hackers using QR codes to target think tanks and government officials. Look for signs of tampering and check the web address your phone displays before opening it. If you’re not sure, don’t open the link. Instead, go directly to the organization’s official website or app.
Scammers rely on speed and pressure, so the best defense is to slow down. If a message or call feels off, step away and check it through a channel you already trust.
According to CNET. Read their review →
Source: Malwarebytes Labs · 2026-10-22
The EU Commission will assess whether Booking.com has adequately protected customers from phishing attacks
Source: Infosecurity Magazine · 2026-10-22