Defense Evasion
Affiliate Recruitment
Targeting Expansion
Observed
Beelzebub Ransomware Announces Major Rewrite and Recruitment Push for New Operators
HIGH
Overview
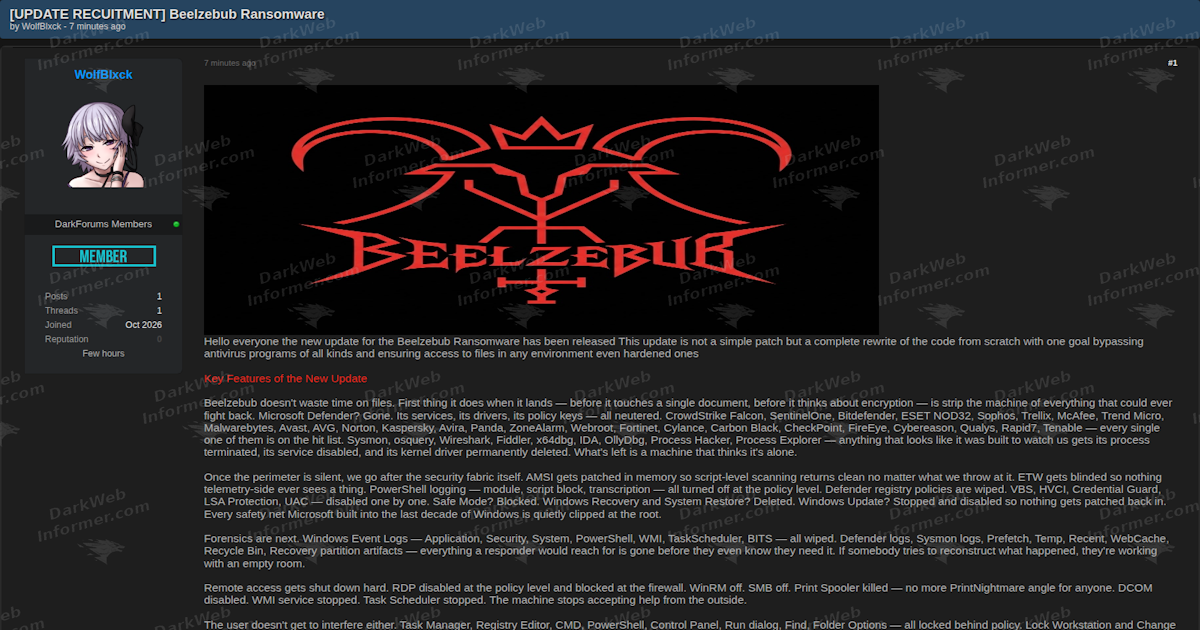
An actor using the handle “WolfBlxck” posted an updated recruitment announcement for Beelzebub ransomware, claiming the malware has been rewritten from scratch with a stronger emphasis on disabling endpoint defenses, suppressing telemetry and making incident response more difficult.
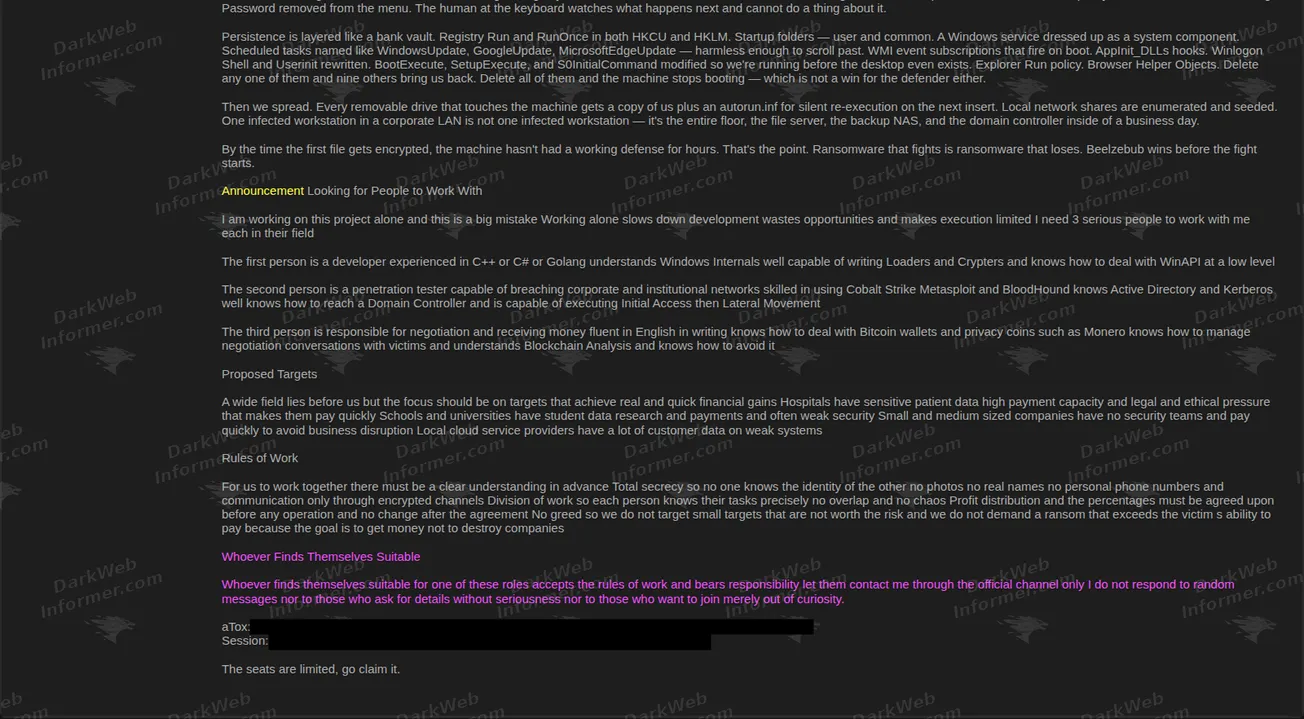
The post also expands the recruitment pitch, stating that the operator is looking for three additional people: a developer, a penetration tester and a negotiator. The actor lists hospitals, schools and universities, small and medium-sized businesses, and local cloud providers as proposed target categories. The recruitment post is directly visible in the supplied screenshots, but the malware capabilities and operational claims have not been independently validated.
Post details
What the post claims
- Complete rewrite of the ransomware codebase
- Focus on bypassing antivirus and EDR products
- Claims to interfere with endpoint-security products
- Claims to terminate monitoring and analysis utilities
- Claims to suppress AMSI and ETW visibility
- Claims to disable PowerShell logging
- Claims to disable Windows security controls
- Claims to remove recovery components
- Claims to wipe Windows event logs and other forensic artifacts
- Claims to disable remote-management and network services
- Claims to restrict common administrative tools
- Claims multiple persistence mechanisms
- Claims propagation through removable media and network shares
- Recruiting one developer
- Recruiting one penetration tester
- Recruiting one negotiator
- Hospitals named as proposed targets
- Schools and universities named as proposed targets
- SMBs and local cloud providers named as proposed targets
The actor also outlines internal operational rules covering secrecy, role separation and profit-sharing. Those details are summarized at a high level here rather than reproduced as procedural instructions.
Screenshots

IOCs & identifiers
Identifiers directly visible in the supplied material. These support correlation and do not independently verify the malware’s capabilities.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | WolfBlxck |
Screenshots 1–2 |
| Ransomware name | Beelzebub |
Screenshots 1–2 |
| Tox ID | 6D29A6A0E0BA4FAB31FA4541F89B800459CBB14736B17557B9DC79019F7B460A450E646FFB1B |
Screenshot 2 |
| Session ID | 051b3888c0b3e561b598579627840af056f2b9cd3600f9ef07157d290551b35442 |
Screenshot 2 |
No malware hash, Telegram handle, attacker-controlled domain or attacker-controlled IP address is visible in the supplied screenshots.
Mapped techniques
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the capability has been independently validated.
-
Defense Evasion
T1562.001
Impair Defenses: Disable or Modify Tools
Claimed
The actor claims the ransomware disables or interferes with security products, monitoring utilities, logging and telemetry. -
Defense Evasion
T1070.001
Indicator Removal: Clear Windows Event Logs
Claimed
The post explicitly claims removal of Windows event logs and other forensic artifacts. -
Impact
T1490
Inhibit System Recovery
Claimed
The actor claims the malware removes or disables recovery-related components before encryption. -
Persistence
T1547.001
Boot or Logon Autostart Execution: Registry Run Keys / Startup Folder
Claimed
The second screenshot explicitly describes Registry Run/RunOnce and Startup Folder persistence.
Potential impact
If the advertised capabilities are genuine, the rewritten malware could increase operational difficulty for defenders by combining security-tool disruption, telemetry suppression, forensic artifact removal, recovery interference, persistence and network propagation before encryption. The recruitment push could also expand the operation’s technical and negotiation capacity.
Status Observed
The supplied screenshots directly document the Beelzebub update and recruitment post. Dark Web Informer has not independently verified that the malware can perform every claimed action, that the listed security products are successfully bypassed, or that the operation has recruited the roles described.
Source: Dark Web Informer · 2026-10-16