Tag: Federal Bureau of Investigation (FBI)

  • Oklahoma man charged with mailing threats, substances to election officials nationwide 

    Oklahoma man charged with mailing threats, substances to election officials nationwide 

    An Oklahoma man has been charged with mailing suspicious white substances to election officials across the country.

    Robin Patrick Martin faces charges of conveying false or misleading information and hoaxes, as well as mailing threatening communications. The charges allege a nationwide effort to intimidate election officials and support President Donald Trump.

    Starting on Sept. 16, 2024, multiple state election officials reported receiving mail containing a white, powdery substance and a three-page letter headed “DECLARATION OF WAR.” Officials in nearly every state have since received similar mailings over the past two years. Election officials provided some of the evidence, while federal authorities intercepted other letters in transit. 

    The letters bore a return address for the “The United States Traitor Elimination Army” in Takoma Park, Maryland. Some envelopes also had threatening messages written on them that could only be seen under ultraviolet light.  

    The letters cited the belief, promoted by some supporters of Trump, that the 2020 election was marred by voter fraud, along with similar concerns about the 2024 election.

    Other envelopes included messages like “No US Jurisdiction!,” “Mailed from the Indian Nation,” and “Are you for us? Or against us?”

    Another message read: “To FBI: What do you want for your children? Peace through strength or nuclear war? Use your common sense! Protect Trump! Protect the election! Protect Legal votes! Throw out illegal votes! That is the motive!”
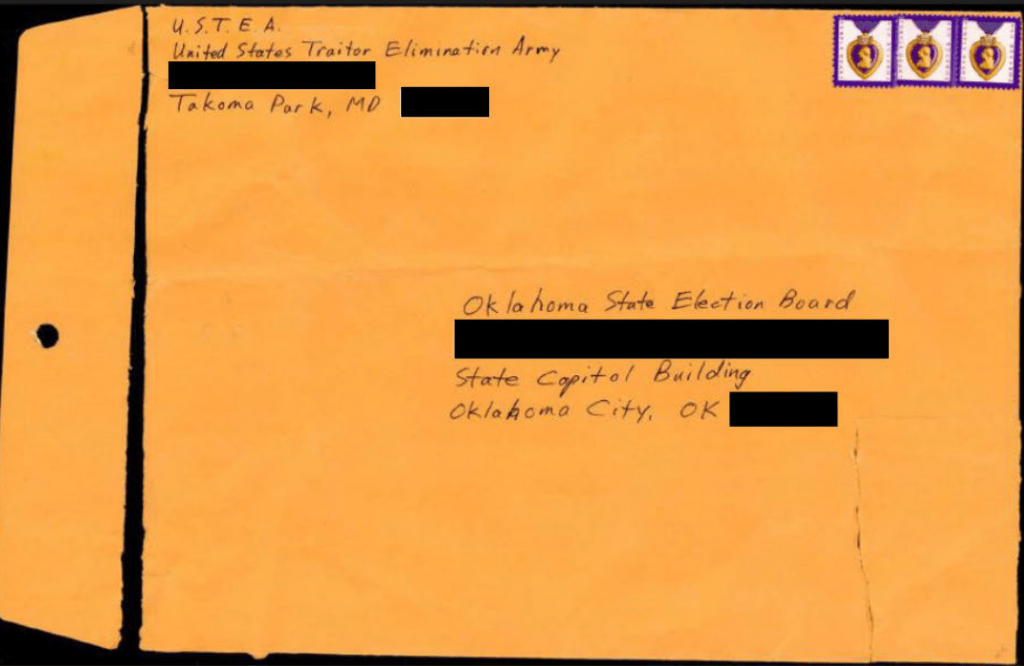
    The case was first reported by the Associated Press.

    Investigators subpoenaed email and phone records listed for the address,  tying it to a burner phone purchased at a Walmart Supercenter in Northwest Oklahoma City. Surveillance video showed an older white man matching Martin’s description purchasing the phone and driving away in a car registered to  Martin.

    Other items purchased at the same Walmart pointed to Martin’s involvement, including a booklet of stamps, privacy envelopes, along with tumeric, white vinegar and povidone-iodine, which are used to make invisible ink. Records from the phone also placed Martin at various postal distribution centers around the state.

    The FBI and Department of Justice did not announce the case or issue a press release about the charges against Martin as of 1pm Tuesday. CyberScoop has reached out to both for comment.

    Source: CyberScoop · 2026-11-03

  • Officials seize domain of top bulletproof hosting provider Virtualine

    Authorities seized the domain of Virtualine, a bulletproof hosting provider that cybercriminals used to commit a large-scale sextortion scheme, ransomware, data theft, malware hosting and money laundering, the Justice Department said Tuesday. 

    Virtualine facilitated prolific criminal activity, including the distribution of child sexual abuse material (CSAM), the Justice Department said. The Russian-speaking bulletproof hosting provider was among the most active this year in crypto-related crime in particular, researchers said. 

    The site and its associated infrastructure stands out among the dozens of bulletproof hosting providers currently tracked by TRM Labs. “It was not among the largest by total inflows, but it received the most illicit-attributed value in 2026 to date,” the blockchain and cryptocrime research firm wrote in a blog post.

    Virtualine received almost one-fifth of all illicit-attributed inflow among bulletproof hosting providers tracked by TRM this year to date.

    A Russian drug marketplace accounted for nearly 44% of the direct payments Virtualine received from customers and attributed counterparties so far this year, according to TRM. A sextortion scheme accounted for nearly 17% of direct payments to Virtualine, followed by a cryptocurrency mixer at almost 13%, ransomware at nearly 5%, cybercrime services at 3% and malware at 2%.

    “Virtualine is another example of Russia’s illicit economy at work: darknet markets, ransomware groups, non-compliant exchanges, and brokers all feeding the same ecosystem,” Ari Redbord, global head of policy at TRM Labs, said in a prepared statement. 

    “Bulletproof hosting is the connective tissue. Seizing a domain matters, but the blockchain record doesn’t disappear with it. It shows who is paying, who is getting paid, and where they go next,” he added. 

    Virtualine attracted many criminals as customers. Ransomware groups, including Coinbase Cartel, The Gentlemen, INC, DragonForce and Qilin all paid the site’s operators, according to TRM. The bulletproof hosting provider also received payments from the StealC infostealer, the Matanbuchu loader, bot and malware-distribution services and sites linked to CSAM. 

    The FBI and prosecutors got a court order to seize Virtualine’s primary domain, which was also known as Secury, Massgod, Spamhouse, Lanedo and Omegatech.

    Officials said Virtualine continued hosting services for a customer that distributed CSAM and a hack-for-hire service after it received numerous notices from law enforcement in Germany, Canada, Australia, the National Center for Missing and Exploited Children and a victim’s attorney.

    TRM underscores that Virtualine was disrupted, but not completely shut down. “A domain seizure disrupts how customers find and access a service,” researchers wrote. “It does not, by itself, establish that the operator has stopped working, or that customers have lost access to all underlying infrastructure.”

    Source: CyberScoop · 2026-10-29