Large language model hijacking attacks, also known as LLMjacking, are generating large fraudulent cloud charges, with some organizations losing more than $100,000 per day. […]
Source: BleepingComputer · 2026-11-03
Large language model hijacking attacks, also known as LLMjacking, are generating large fraudulent cloud charges, with some organizations losing more than $100,000 per day. […]
Source: BleepingComputer · 2026-11-03
The Ransomnews research team counted 484,142 publicly listable cloud storage buckets in October 2026, holding 18.05 billion files. They built the count from the search engines that index open cloud storage and published it as the Ransomnews Cloud Exposure Index, written by Mantas Sasnauskas.
“No file was opened for this index. Every number below comes from bucket names, file extensions, file counts and last-modified timestamps. That is a deliberate limit. It keeps the research on the right side of the line, and it turns out to be enough to see where the sensitive material concentrates.” Ransomnews states. “We are calling it the Ransomnews Cloud Exposure Index, and we will rerun it quarterly so the numbers can be compared over time.”
The researchers used bucket names, file types, file counts and last-modified dates to collect their data. They did not open any files, allowing them to identify where sensitive information might be stored without accessing the content. They plan to repeat the research every three months to track changes over time.
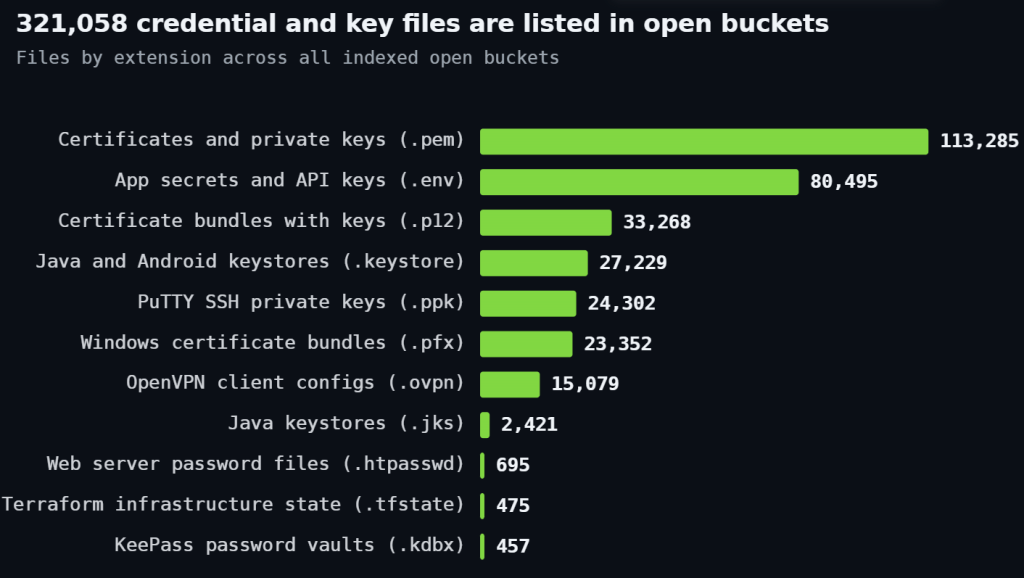
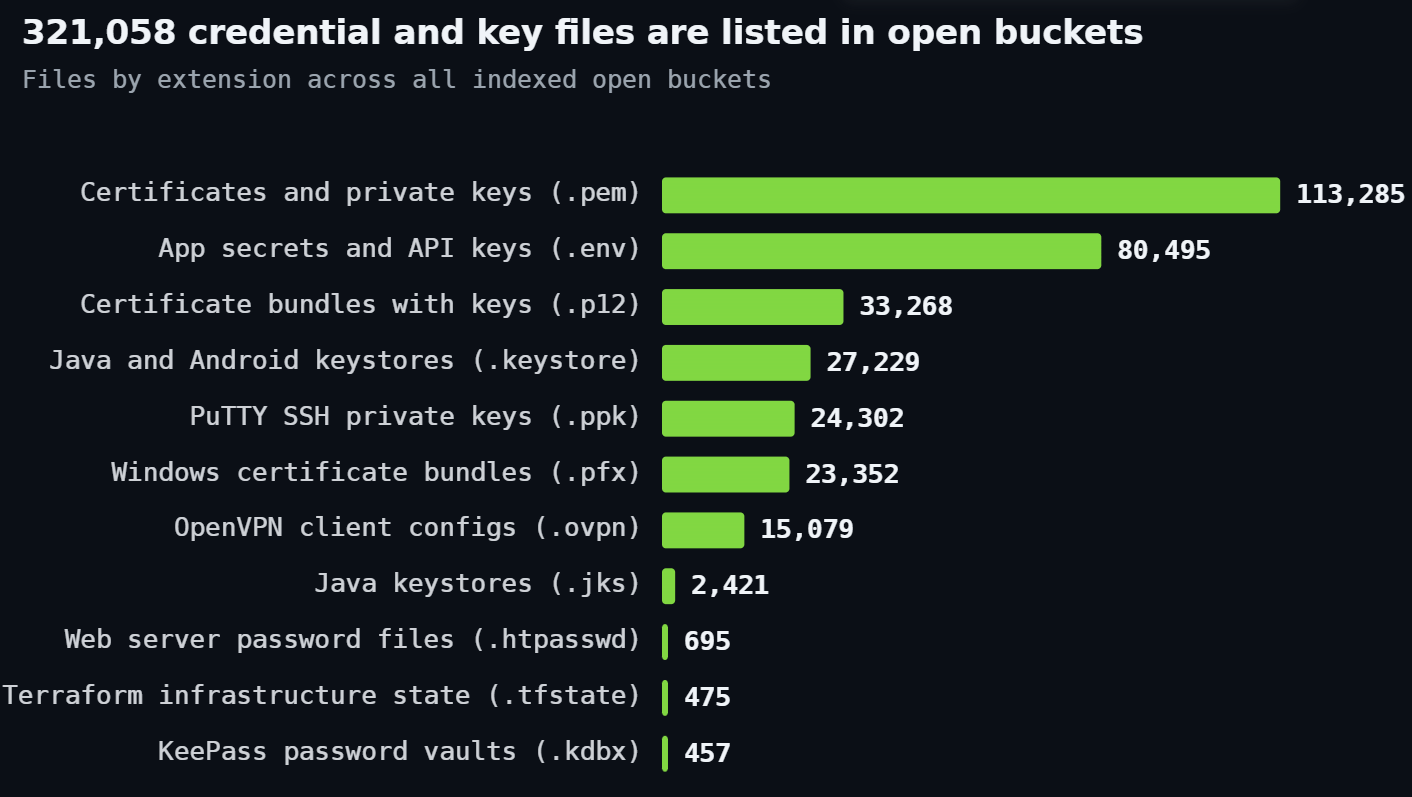
Amazon S3 accounts for 72% of the exposed buckets, roughly in line with its share of the market. This does not mean S3 has weaker security than other providers. Azure Blob, however, appears 2.5 to 3.6 times more often than expected among buckets named for backups, data exports and payroll records. The researchers also found 321,058 files related to credentials and keys. Of the exposed .env files, 67% were last modified in 2026.
Below is the split by provider, from a snapshot taken on October 7:
| Provider | Open buckets | Share |
|---|---|---|
| Amazon S3 | 347,984 | 71.9% |
| Azure Blob | 68,532 | 14.2% |
| Google Cloud Storage | 53,131 | 11.0% |
| DigitalOcean Spaces | 11,069 | 2.3% |
| Alibaba OSS | 3,426 | 0.7% |
| Total | 484,142 | 100% |
A lot of these buckets are public on purpose, holding website assets, CDN mirrors, open datasets and podcast archives. So the index isn’t 484,142 breaches. It’s the pool where breaches hide, and the rest of the report narrows it down to the stores that should never have been listable.
“Azure, by a wide margin relative to its size. Azure Blob holds 14.2% of open buckets, but 37% of the 1,459 buckets with “backup” in the name, 42% of the 399 named for exports, and 51% of the 505 carrying HR or payroll terms.” continues the report. “Buckets named for logs, customers and databases sit at 35% to 36%, all around two and a half times Azure’s baseline.”
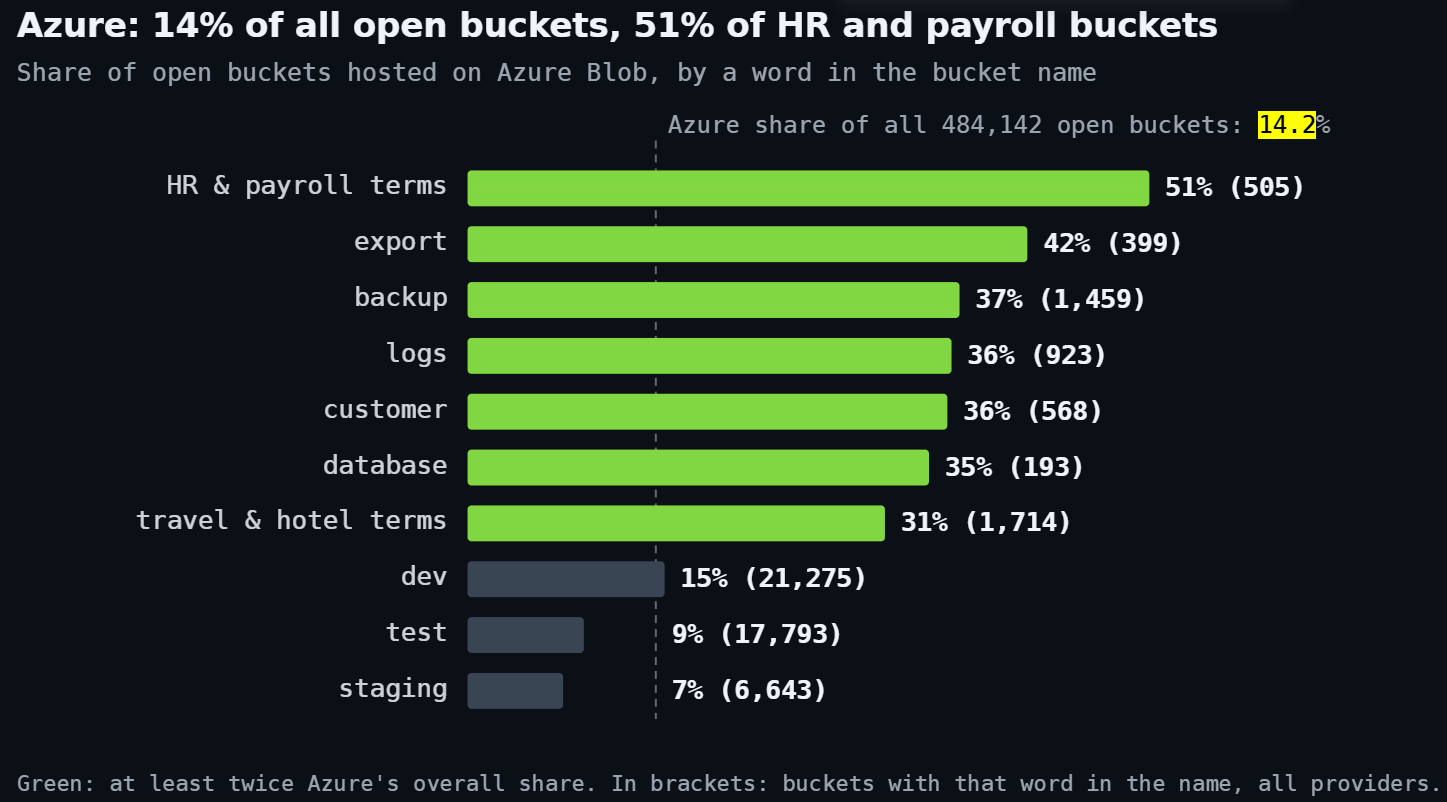
The skew only shows up for operational data. Buckets named “dev” sit at Azure’s baseline of 15 percent, and “test” and “staging” fall below it, at 9 and 7 percent. The authors suspect Azure storage accounts more often hold line-of-business data such as backups, exports and HR systems that enterprises run on Microsoft, while S3 and Google Cloud carry more application assets. They call it a hypothesis the counts suggest and don’t prove, and it’s the first thing they want to test next time.
By sector, retail and e-commerce names lead with 5,666 buckets, mostly storefront assets. The more worrying number is that names tied to regulated sectors (finance, healthcare, education, government, legal and HR) appear on 10,891 unique open buckets. Those are the places where a stray file most likely holds personal, health or financial records, and where regulators expect to hear about it.
| Sector (by bucket name) | Open buckets | Files in them |
|---|---|---|
| Retail and e-commerce | 5,666 | 269.9M |
| Finance and insurance | 3,508 | 58.0M |
| Healthcare | 2,709 | 47.9M |
| Media and entertainment | 2,696 | 136.2M |
| Education | 2,393 | 60.6M |
| Gaming | 2,296 | 79.0M |
| Travel and hospitality | 1,714 | 118.7M |
| Real estate | 1,137 | 60.7M |
| Government and public sector | 1,000 | 36.2M |
| Legal | 978 | 11.3M |
| Crypto | 630 | 11.9M |
| HR and payroll | 505 | 8.4M |
Healthcare-related names appear in 2,709 buckets containing 47.9 million files. The researchers identified them using terms such as “hospital” (135 buckets), “patient” (135), “clinic” (277) and “dental” (331). HR and payroll is the smallest sector, with 505 buckets, 259 of which are hosted on Azure.
These figures are based on names, not proof of ownership. The search matches parts of words, so “store” can refer to object storage as well as shops. A single bucket can also appear in two sectors.
The exposed buckets also list about 4.7 million database and dump files, 15,130 mailbox archives, and tens of millions of spreadsheets and documents. Credential files are particularly concerning because they can turn a cloud misconfiguration into a real intrusion.
| File type | What it is | Files listed |
|---|---|---|
| .pem | Certificates and private keys | 113,285 |
| .env | App secrets and API keys | 80,495 |
| .p12 | Certificate bundles with keys | 33,268 |
| .keystore | Java and Android keystores | 27,229 |
| .ppk | PuTTY SSH private keys | 24,302 |
| .pfx | Windows certificate bundles | 23,352 |
| .ovpn | OpenVPN client configs | 15,079 |
| .jks | Java keystores | 2,421 |
| .htpasswd | Web server password files | 695 |
| .tfstate | Terraform infrastructure state | 475 |
| .kdbx | KeePass password vaults | 457 |
Each of these exists to grant access. A .env file is where developers keep database passwords and API keys. A .tfstate file is Terraform’s record of a whole cloud setup, often with secrets in plain text, and a .kdbx vault is encrypted but now open to anyone who wants to guess passwords offline. Some .pem files are public certificates and some files are test fixtures, so the counts are a ceiling on live secrets and not a measure of them. It’s still a big ceiling.
Database files make up most of the sensitive material by volume:
| File type | What it usually holds | Files listed |
|---|---|---|
| .sqlite | Embedded app databases | 2,561,807 |
| .bak | Database and server backups | 752,055 |
| .sql | Database dumps | 687,446 |
| .sqlite3 | Embedded app databases | 488,176 |
| .dump | Database dumps | 176,603 |
| .mdb / .accdb | Microsoft Access databases | 36,467 |
| .dmp | Memory and crash dumps | 12,809 |
| .pst / .ost / .mbox | Mailbox archives | 15,130 |
| .eml | Saved emails | 4,549,665 |
| .csv | Data exports and records | at least 69,580,112 |
| .xlsx / .xls | Spreadsheets | 42,544,997 |
| .docx | Word documents | 24,936,788 |
| Documents, invoices, scans | at least 106,191,393 | |
| .log | Application and server logs | at least 61,310,809 |
The exposed buckets contain thousands of virtual disk images, including VMware, Hyper-V and QEMU files. A single disk image can contain an entire server, including credentials.
Some exposures involve active systems. Of 80,495 .env files, 67% were last modified in 2026. Certificates and SQLite databases include both recent and older files. Backups appear older, with 89% of the 752,055 .bak files last modified before 2025. Almost all PuTTY key files date from 2024.
Recent leaks need urgent attention, while long-standing exposures point to poor security management. The problem is ongoing: at least 113.6 million files were added to publicly listable buckets in the seven days before September 9. Over the previous 30 days, these included more than 21,000 SQL dumps, nearly 21,000 backup files, 4,477 .pem files and 1,298 .env files.
Public .env files can expose database passwords that ransomware affiliates and initial access brokers look for. Similar credentials appear in stolen-data logs, but in this case, attackers do not need to infect a device. They only need to search for exposed files.
Cloud providers already offer settings to prevent public access. Organizations should enable S3 Block Public Access, disable anonymous access to Azure Blob storage, and enable public access prevention in Google Cloud. These controls should apply at account or organization level to prevent new storage buckets from becoming public.
Organizations should also scan their storage for sensitive files such as .env, .sql, .bak, .pem, .ppk, .tfstate and .kdbx. Terraform state files and virtual disk images should be treated as secrets, stored privately, encrypted and monitored. Backups should never be publicly accessible, and recovery procedures must be tested.
One exposed bucket may be a mistake, but many often indicate a wider process failure. Organizations need to fix the underlying security controls, not just individual buckets.
The research has some limitations. The team queried search engines on October 25, while the bucket list was current to October 7 and the newest indexed file dated September 9. File-level data may therefore be about a month old. Counts are also capped at one million per query, so researchers split larger categories into date ranges and added the results.
Some limits apply. The team queried the search engines on October 25. The bucket list was current to October 7 and the newest indexed file was dated September 9, so file-level figures lag by about a month. The index caps any single count at one million, so larger types were split into date windows and summed.
A last-modified date shows when a file was written, not when it was exposed, and a listed file isn’t proof that its contents can be read. No bucket is named in the report. Exposures with a known owner in regulated sectors are going through responsible disclosure, with national CERTs copied where the owner is public sector or doesn’t respond.
“Rotate any secret that has ever sat in a public bucket. Closing the bucket does not un-leak the key. Assume anything that was listable was copied.” conlcudes the report.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Cloud Buckets)
Source: Security Affairs · 2026-10-29