Tag: budget

  • What Democratic control of Congress means for cybersecurity

    Democrats’ big win on Election Day, which saw them take control of both the House and Senate, has ramifications for the Cybersecurity and Infrastructure Security Agency, artificial intelligence, surveillance policy and much more.

    Here’s what lawmakers and cybersecurity experts have to say about the short-term and long-term prospects on Capitol Hill.

    Leadership plans ahead

    Maggie Hassan, R-N.H. is in line to take the gavel on the Senate Homeland Security and Governmental Affairs Committee, with Sen. Gary Peters, Mich., retiring.

    “Our government’s number one job is to keep people safe, and the Senate Homeland Security and Governmental Affairs Committee must work to ensure that our country remains safe, secure and free from all kinds of threats,” Hassan said in a statement to CyberScoop. “That work involves protecting against terrorism and fentanyl trafficking, but it also includes guarding against emerging threats like artificial intelligence security risks and strengthening our cybersecurity.”

    “The Trump-Vance administration has undermined our security on these fronts, including by diverting resources away from combatting fentanyl trafficking and gutting CISA,” she continued. “We need to reverse these cuts, confront these challenges and put public safety first.”

    Rep. Bennie Thompson, D-Miss., is poised to return once again as chair of the House Homeland Security Committee, said Democrats are taking over at a “pivotal time for CISA,” with it looking to add staff after cutting back by nearly one-third.

    “First and foremost, we will aim to work with CISA to expedite its critical re-staffing effort and to ensure it has the expertise necessary to support stakeholders as they defend against the scale and velocity of AI-enabled cyber-attacks,” he said in a statement to CyberScoop. “Advances in AI can help defenders, but it will also accelerate the consequences of deferred investments in security and CISA must be well-positioned to help critical infrastructure owners and operators rapidly improve their cybersecurity posture.”

    “We will prioritize getting resources straight into the hands for defenders — by extending the State and Local Cybersecurity Grant Program and improving support of under-resourced sectors, especially water,” he continued. “We will work to ensure CISA re-establishes its cross-sector coordination capacity, which was diminished when the Trump administration- terminated CIPAC, by making sure the Anchor-CI is eventually up and running and meets the needs of stakeholders. Finally, we will make sure CISA is well-positioned to support the secure development and deployment of AI.”

    What happens in the lame-duck session

    Before the GOP relinquishes control of the House and Senate to Democrats, though, there’s a lame-duck session ahead. 

    Long-term renewal of the Cybersecurity Information Sharing Act of 2015 (CISA 2015) is a bipartisan and industry priority, with it set to expire Dec. 11. Current Senate Homeland Security and Governmental Affairs Chairman Rand Paul, R-Ky., has been the biggest obstacle to reauthorization, but he could get “rolled” by GOP leadership on an extension, said Michael Garcia, a former government cyber official and vice president of the cybersecurity practice at Monument Advocacy. Possible vehicles for CISA 2015 to hitch a ride include an omnibus funding bill or the annual defense policy bill.

    The Department of Homeland Security, and its subagency CISA, are currently operating on a continuing resolution that’s also set to expire Dec. 11, where lawmakers could temporarily extend CISA 2015 if a long-term solution can’t be reached in the lame duck. Another continuing resolution before Dec. 11 in lieu of an omnibus spending bill is an option for the lame duck. Both a CR and omnibus spending bill would theoretically include DHS funding, although the agency’s funding has been made more difficult in the past by the presence of Immigration and Customs Enforcement within the department.

    Republicans have talked about wanting to get the fiscal 2027 National Defense Authorization Act done in the lame duck. Besides the possibilities of CISA 2015 being included in the bill, Nicholas Leiserson, senior vice president for policy at the Institute for Security and Technology, said the Senate version of the legislation has a pair of very noteworthy cyber provisions: a “very broad” authorization for contractor-owned, contractor-operated offensive cyber operations, and a requirement that every artificial intelligence product sold to the Defense Department have an AI bill of materials.   

    Additional leadership shuffle

    While Paul is losing his gavel, he’s shown he can be a disruptive force on passing cybersecurity legislation through the Senate in the minority. That makes what he does next possibly determinative for cyber bills, Leiserson and Garcia said. “If he leaves HSGAC, let a thousand cyber bills flourish!” Garia quipped on social media. Paul could opt to become the top Republican on the Senate Health, Education, Labor and Pensions Committee instead of HSGAC.

    Nebraska Sen. James Lankford would take over for Paul as top HSGAC Republican in that scenario, and an industry source said he’s viewed as a supporter of CISA 2015.

    On Senate Intelligence, the panel’s leadership goes to a lawmaker who has placed a big emphasis on cybersecurity in his congressional career: Mark Warner, D-Va. 

    On the House side, while Rep. Andrew Garbarino, R-N.Y., moves to the minority on the Homeland Security panel, he has proven willing to collaborate with Democrats on cybersecurity issues. Rep. Delia Ramirez, D-Ill., is poised to take the gavel of the panel’s cybersecurity subcommittee, and Rep. Vince Fong, R-of California looks set to become the subcommittee’s top Republican and has his own history of bipartisanship. Fong would replace current subcommittee chair Andy Ogles, the far-right Tennessee Republican who lost in the primaries.

    One thing to watch in the House, Leiserson said, is how the House looks to tackle AI — through existing committees, a select committee or some other structure. Democrats haven’t put forward a unified front on AI guardrails yet.

    With AI models uncovering as many vulnerabilities as they are, “highly capable frontier models are going to drive a lot of discussion” about AI and cybersecurity, said Craig Albright, the Business Software Alliance’s senior vice president for U.S. government relations.

    Appropriations, oversight, legislation

    If the NDAA or a CISA 2015 extension don’t pass in the lame duck, they’d be priorities in 2027, too.

    “CISA 2015 has to happen, and if we can’t get it done, then we can’t move to the next thing,”  said Henry Young, BSA’s policy director. “Once we get it done, there’s an open question about which of these priorities that we’ve talked about gets to be number one. Is it post-quantum cryptography? Is it government IT modernization? Is it frontier AI cybersecurity systems? We don’t know that yet, and we can’t know until we pass this law.”

    How damaged the agency CISA is by Trump administration’s budget cuts is something Democrats are expected to scrutinize closely. Another top budget issue is what to do with the expired State and Local Cybersecurity Grants Program housed at DHS, since even if it’s reauthorized, it will require appropriators taking steps to invest in it.

    Democrats could take a look at a variety of other Trump administration changes at DHS and CISA, on topics like election security, the Cyber Safety Review Board, the Joint Cyber Defense Collaborative and more. 

    More broadly, Leiserson said an area of Democratic cyber oversight is likely to be the Department of Government Efficiency that cut cyber personnel at agencies at and beyond CISA, and “particularly the integrity of systems that DOGE touched when they were given very high privileged access to federal systems.”

    If the White House puts forward a permanent nominee for director of CISA, Democrats would be poised to vet that person. They also would have a say in who leads the Office of the National Cyber Director, should the incumbent, Sean Cairncross, depart.

    So far, Democrats haven’t put forward a unified posture on expired surveillance authorities known as Section 702, although both Warner and incoming House Intelligence Chairman Jim Himes, D-Conn., have fought in the past for its renewal. The surveillance program is operating similarly still due to a court order, but that order only lasts through next spring.

    Source: CyberScoop · 2026-11-04

  • The Enterprise Threat Intelligence Report: 2026

    Threat intelligence teams are heading into 2027 with more than ever to monitor, driven by an acceleration in the AI threat landscape. However, their expanded mandate typically doesn’t come with a proportional budget windfall. Instead, teams are under pressure to get greater value from the intelligence, systems, and analyst expertise already available to them.

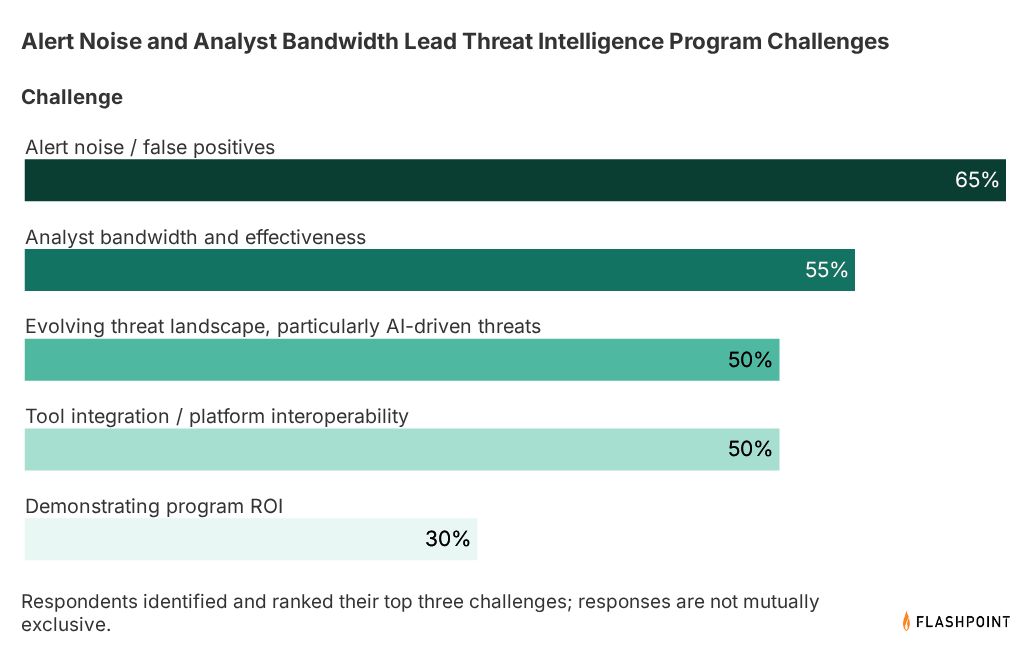
    New independent research commissioned by Flashpoint shows where that pressure is being felt most. Alert noise and false positives are the most frequently cited challenges affecting threat intelligence program effectiveness, followed by analyst bandwidth, changes in the threat landscape, and integration across security tools. At the same time, AI-related threats have emerged as the leading area where practitioners want to expand intelligence coverage.

    These findings point to some of the decisions that will shape threat intelligence programs in the year ahead: where to focus finite analyst capacity, how intelligence requirements need to evolve, and where AI can meaningfully support the work. Organizations are already evaluating agentic AI across threat intelligence workflows, but the research also shows that greater autonomy comes with higher expectations around accuracy, control, and measurable value.

    For security leaders planning their 2027 threat intelligence strategy and budgets, this report examines:

    • Which operational challenges are putting the greatest pressure on analyst capacity and threat intelligence programs today.
    • How intelligence requirements are changing as AI-enabled threats create new coverage priorities.
    • How threat intelligence budgets are trending in the next 12 months, and where incremental budgets will go.
    • Where practitioners see the strongest applications for agentic AI, and which AI-powered workflows face a higher threshold for trust and autonomy.
    • What teams need to prove before expanding AI investment, including the metrics practitioners are using to evaluate time savings, accuracy, risk reduction, and ROI.

    Together, the findings provide a practical benchmark for teams evaluating their own intelligence operations: where to focus limited analyst time, where automation may have the greatest impact, and what to measure as AI becomes part of the workflow.

    Executive Summary

    As threat intelligence teams plan for 2027, the research shows them managing two simultaneous pressures: intelligence requirements are expanding, while the capacity available to address them remains constrained. AI is intensifying that pressure as adversaries adopt new capabilities, but also becoming part of how organizations are thinking about scaling their ability to defend their organizations.

    “2027 will test whether threat intelligence programs can scale their reach as fast as AI is reshaping the threat landscape. The opportunity for agentic AI on the defensive side is significant, and our research shows security leaders are ready to invest. But they aren’t swayed by the hype. They’re holding agentic AI to a high bar, and they want to know where it improves their work, whether they can trust the output, and where human judgment must remain part of the process.”

    Josh Lefkowitz
    Co-Founder and CEO, Flashpoint

    Four findings stand out:

    • The AI threat landscape is accelerating faster than threat intelligence teams can keep up. Alert noise and false positives were the most frequently cited challenge, identified by 65% of respondents, while 55% cited insufficient analyst bandwidth and half pointed to integration gaps across their security tools.
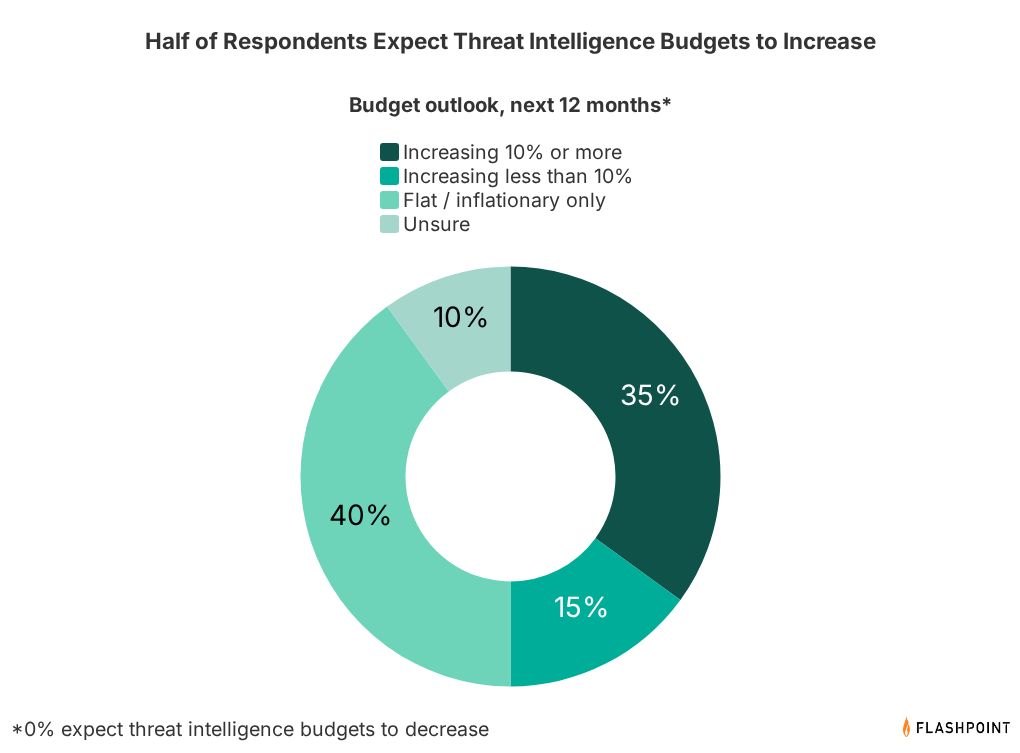
    • Threat intelligence budgets are rising to close the gap. Half of respondents expect their budgets to increase over the next 12 months, including 35% anticipating meaningful increases of 10% or more. Another 40% expect spending to remain essentially flat. No respondents anticipate a decrease. Where budgets are growing, organizations are directing investment toward areas including AI-related threat coverage, additional intelligence feeds and modules, and broader program development.
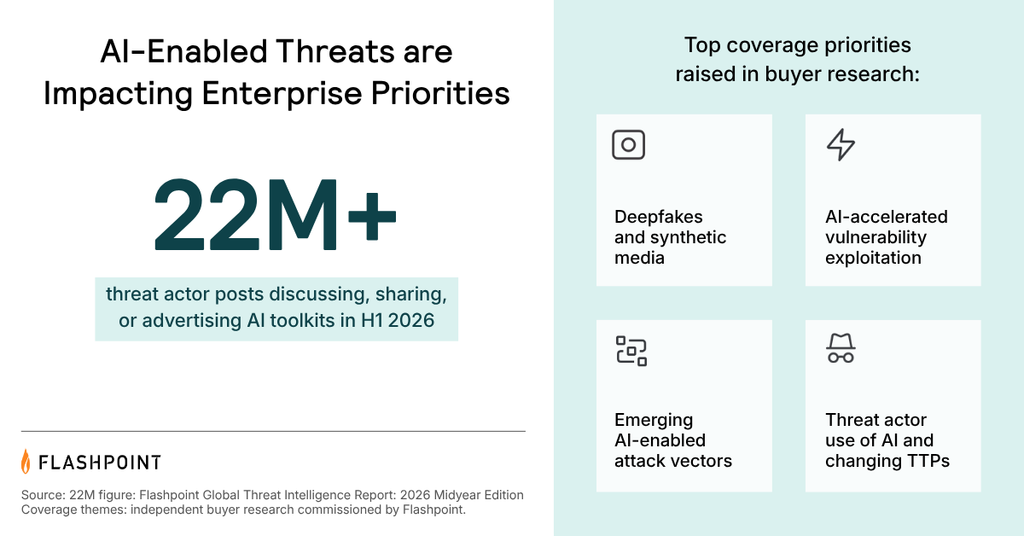
    • AI-related threats are the leading priority for expanded coverage and new investment. Practitioners pointed to deepfake detection, AI-accelerated vulnerability exploitation, and emerging AI-enabled threat vectors as areas where their intelligence requirements are expanding.
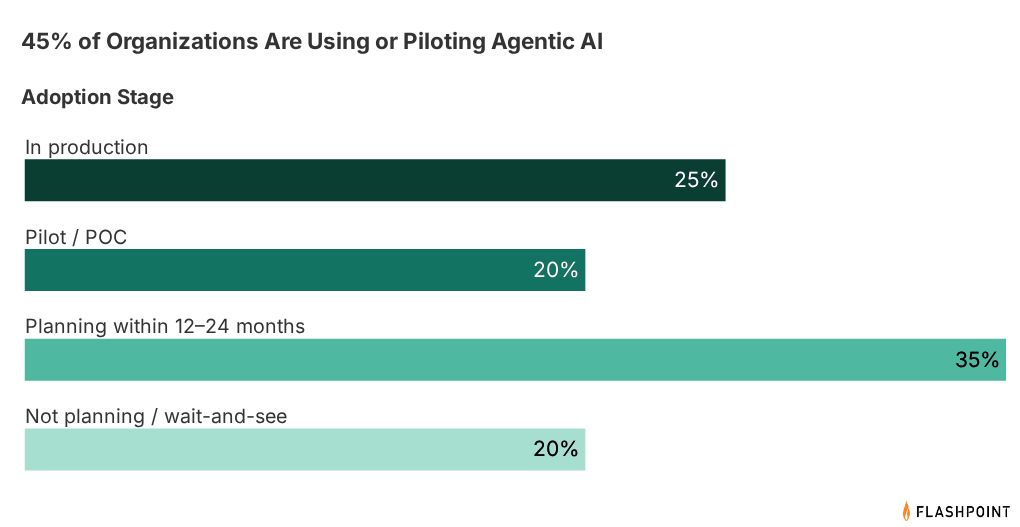
    • Agentic AI adoption is underway, but teams are setting a high bar. Just 25% of organizations interviewed are using agentic AI in production today. Another 20% are piloting it, while 35% are planning adoption within the next 12 to 24 months. Rather than rushing toward autonomy, teams are evaluating where agents can improve workflows while maintaining intelligence quality, appropriate controls, and human oversight.

    Taken together, the findings show where threat intelligence teams are feeling the greatest pressure, where they see opportunities to extend their capabilities with AI, and what will determine whether those tools earn a lasting place in the intelligence workflow. The sections that follow examine each of these findings in greater detail and what they mean for threat intelligence programs.

    Operational Challenges Are Putting Pressure on Analyst Capacity

    The rising AI threat landscape is increasing pressure on organizations to get more capacity from the people and systems they already have. Threat intelligence leaders therefore say the biggest barriers to program effectiveness are operational: too much noise, limited analyst bandwidth, and disconnected tools.

    Alert noise and false positives emerged as the leading challenge affecting threat intelligence programs, cited by 65% of respondents. Analyst bandwidth followed at 55%, while half of respondents pointed to both the evolving threat landscape and integration gaps across their security tools.

    chart visualization

    The impact of these challenges becomes clearer at the workflow level. One healthcare practitioner described receiving alerts about email breaches that were seven or eight years old, with the same data resurfacing each time it was resold and requiring another investigation. Practitioners also described manual steps between intelligence feeds, SIEMs, SOAR platforms, ticketing systems, and response workflows.

    Each unnecessary investigation or manual handoff consumes time that could otherwise go toward analysis. That becomes difficult to solve through hiring alone because threat intelligence expertise takes time to develop. As one healthcare threat intelligence leader explained:

    “Good analysts take time to develop and train, and we can’t hire our way out of that problem.”

    The research suggests an opportunity to look for capacity within the intelligence workflow itself. Reducing repetitive investigations, improving integration between systems, and helping analysts identify relevant intelligence faster can return more of their time to work that depends on context and judgment.

    Threat Intelligence Investment Remains Resilient Heading Into 2027

    The rise of AI-driven threats is driving increases in the intelligence budgets of many organizations. Among respondents who provided a budget outlook, 50% expect their threat intelligence budgets to increase over the next 12 months, while the remaining 40% expect budgets to stay essentially flat. None anticipate a decrease.

    More than a third (35%) expect meaningful growth of at least 10%, suggesting that for many organizations, threat intelligence remains an area of active investment heading into 2027.

    chart visualization

    Where organizations are increasing investment is equally important. Respondents expecting meaningful growth described spending on AI defense capabilities, expanded threat intelligence feeds and modules, and broader program development. AI-related threat coverage also emerged across both flat and growing budgets as the most frequently cited area where teams want to expand coverage.

    For teams heading into 2027, the findings suggest that the question is increasingly where to direct threat intelligence investment for the greatest impact. Organizations are evaluating how existing resources can address new intelligence requirements, where additional capabilities are needed, and which investments can demonstrate clear operational value.

    As organizations decide where to focus threat intelligence investment in the year ahead, AI is the clear priority. AI-related threats were the most frequently cited area where organizations want to expand intelligence coverage, including among teams with relatively flat budgets. Practitioners specifically pointed to deepfake detection, AI-accelerated vulnerability exploitation, and emerging AI-enabled threat vectors.

    These priorities reflect activity already visible across the threat landscape. During the first half of 2026, Flashpoint tracked more than 22 million threat actor posts discussing, sharing, or advertising AI toolkits for criminal deployment. Flashpoint analysts observed AI being used across phishing, malware development, evasion, and vulnerability exploitation.

    For threat intelligence teams, expanding AI coverage requires more specificity than treating “AI threats” as a single monitoring category. Deepfakes may matter because of executive impersonation or fraud. AI-accelerated exploitation may change vulnerability monitoring and prioritization. New attack tooling may affect the adversaries or TTPs a team already tracks.

    The challenge extends beyond visibility into these threats. Organizations also need the expertise to understand how AI is changing adversary behavior and attack chains. That expertise is still developing. As one practitioner put it, “everybody’s learning it at the same time.”

    Connecting those developments to existing PIRs and business risks gives analysts clearer collection priorities and helps teams determine what new sources, expertise, and monitoring they actually need.

    Those requirements are also expanding at a time when analyst bandwidth is already constrained, creating a second question for threat intelligence leaders: where can AI support the intelligence workflow itself?

    Agentic AI Adoption Is Underway

    Nearly half of the organizations interviewed are already using or piloting agentic AI in threat intelligence workflows, while another 35% are planning adoption within the next 12 to 24 months. That makes agentic AI an important part of 2027 planning, but despite the attention surrounding it, threat intelligence teams are taking a measured approach. They are looking for clear business value, evidence that AI can maintain the quality of their intelligence workflows, and appropriate human oversight as agents take on more consequential tasks.

    chart visualization

    The work being handed to agents already varies considerably, from information retrieval and alert prioritization to more active tasks such as blocking IP addresses, updating blacklists, and monitoring suspicious traffic. Organizations in the pilot stage also described use cases spanning detection, validation, context generation, SIEM alert analysis, TIP querying, MITRE ATT&CK mapping, and reversible response actions.

    As agents move from retrieving and analyzing information to taking actions that can directly affect security operations, accuracy and trust become increasingly important. One respondent captured the concern succinctly:

    “An agent that’s confidently wrong is worse than one that’s slow.”

    That concern is reflected across the research. Practitioners raised questions around data leakage, auditability, regulatory requirements, cost, and the level of control agents should have over security workflows. One retail respondent, for example, would only consider read-only AI assistants because of the risks associated with granting agents write permissions.

    For teams evaluating agentic AI, that makes the workflow itself an important part of the decision. Tasks with reviewable outputs, reversible actions, and clear success criteria provide a practical starting point. As autonomy increases, teams need equally clear controls around what an agent can access, what it can change, where human approval is required, and how its actions are audited.

    What the Findings Mean for Threat Intelligence Programs

    As threat intelligence leaders plan for 2027, the research points to a clear set of priorities. Teams have more to monitor, limited analyst capacity, and growing interest in AI as a way to scale the work their programs already perform.

    The findings also show that practitioners are selective about where they see that value. PIR coverage monitoring and intelligence briefings can extend coverage and reduce recurring work while keeping analysts involved in the intelligence process. As agents take on more consequential actions, questions around accuracy, permissions, auditability, and human oversight become more important.

    For teams setting priorities for the year ahead, that creates a practical path forward: understand where analyst capacity is being consumed, connect new intelligence requirements to the risks that matter to the organization, identify workflows where automation can meaningfully extend the team, and establish clear measures of success before deployment.

    The challenge for 2027 will be turning expanding intelligence requirements into an operating model that can scale for threat intelligence programs. That means making better use of existing data, systems, and analyst expertise while being deliberate about where agentic AI can extend those capabilities and where human judgment remains essential.

    Methodology

    Flashpoint commissioned independent qualitative research among a select group of more than 20 threat intelligence budget owners and influencers at large North American enterprises across financial services and insurance, healthcare and biotech, retail, and information technology and telecommunications during the early fall of 2026. 

    See Flashpoint in Action

    Source: Flashpoint · 2026-10-13